system mechanic ultimate defense stands at the absolute vanguard of modern digital protection, forging a seamless bridge between ironclad security and blazing-fast hardware performance. In a relentless digital age where invisible threats lurk behind every keystroke and sluggish machines drain our daily productivity, finding a reliable sanctuary has never been more vital. This powerful suite redefines what it means to truly own your device, orchestrating a symphony of advanced privacy shields, military-grade encryption, and proactive threat neutralization right before your eyes.
By blending deep behavioral heuristics with lightning-fast resource optimization, the software transforms an ordinary workstation into an impenetrable, highly responsive fortress. Users no longer have to choose between keeping their personal data safe from sophisticated cyber predators and maintaining peak computing speeds. Every background process works in harmonious alignment to deliver a pristine, uncompromised digital experience, paving the way for a smarter, safer, and infinitely more empowering journey across the web.
Unveiling the layered architecture behind system mechanic ultimate defense reveals how discrete security layers interact with performance utilities.
Source: fixthephoto.com
Modern digital environments demand a harmonious fusion of system speed and impenetrable digital defense. When software engineers first conceptualized computer maintenance utilities decades ago, performance optimization and security operations lived in entirely separate digital universes. Early computing ecosystems treated speed boosts and malware elimination as isolated tasks, requiring users to install fragmented suites that frequently conflicted with one another, consuming valuable system resources just to manage the software meant to protect them.
Over time, the relentless evolution of sophisticated cyber threats forced a paradigm shift across the software development landscape, merging these historically siloed disciplines into unified ecosystems. The realization that sluggish hardware often stems from hidden background infections, and conversely, that security scans frequently paralyze computer performance, sparked an innovative engineering journey. Developers began weaving defensive shields directly into the core telemetry of performance engines, creating symbiotic frameworks where threat detection and speed enhancement operate as dual forces of a single, highly integrated operating organism.
This historical progression transformed cumbersome, resource-heavy security overlays into sleek, multi-tiered architectures capable of simultaneously defending system integrity and maximizing operational velocity without compromise.
At the beating heart of this synchronized architecture lies a sophisticated orchestration of operating system privileges and thread management algorithms. Background resource throttling acts as a vigilant traffic controller, dynamically redistributing processor cycles to ensure that heavy security routines never starve active user applications of essential computing power. When continuous malware scanning routines initiate a deep system inspection, the throttling engine monitors real-time CPU and RAM metrics, intercepting thread execution queues to insert micro-pauses into heavy disk-reading operations.
This delicate balancing act prevents the dreaded computer freeze traditionally associated with antivirus sweeps, allowing complex signature matching and heuristic analysis to occur seamlessly in the shadows. By communicating directly with the kernel, the optimization matrix allocates low-priority CPU cores exclusively to quarantine and decryption tasks, preserving high-priority threads for active user commands. Consequently, users experience uninterrupted workflow productivity while enterprise-grade defense protocols interrogate every incoming packet and running process with absolute mathematical precision.
Historical evolution of combining privacy shields with speed optimization tools
The convergence of privacy protection and system optimization emerged from a critical necessity to resolve software bloat and resource contention on consumer hardware. Early digital security tools functioned as heavy gatekeepers, anchoring themselves deep within the operating system architecture and consuming massive amounts of memory to monitor file access. Meanwhile, standalone registry cleaners and defragmentation utilities worked independently, often misinterpreting security quarantine files as orphaned registry entries or fragmented sectors.
This operational friction led to frequent system crashes and severe user frustration. Recognizing these architectural bottlenecks, software pioneers began engineering unified application frameworks built upon shared telemetry pipelines. This integration allowed privacy shields—such as secure file shredders and anti-spyware monitors—to share cached system data directly with speed optimization algorithms. By eliminating redundant background processes and unifying signature databases, these hybridized suites drastically reduced the overall footprint on local hardware.
The resulting architecture transformed computer maintenance from a reactive, multi-step chore into an automated, proactive defense mechanism that concurrently heals performance fractures and seals privacy vulnerabilities.
Mechanisms of background resource throttling alongside continuous malware scanning routines
The simultaneous execution of deep security scans and high-performance system maintenance relies on advanced process scheduling and dynamic thread allocation. Operating systems inherently prioritize foreground applications, but intensive background scanning can easily overwhelm input-output queues if left unmanaged. To circumvent this, modern defensive utilities employ intelligent throttling algorithms that continuously analyze processor workload in real-time. When a continuous malware scanning routine engages, the throttling mechanism measures the thermal output and core utilization of the central processing unit, adjusting the scan speed dynamically to match the current system load.
System Mechanic Ultimate Defense restores peak digital performance while modern professionals increasingly reveal signs of dissatisfaction with event management platforms cvent bizly groupize due to lagging operational tools. Embracing this powerful software transforms sluggish workflows into vibrant efficiency, empowering every user to conquer daily technological obstacles with renewed confidence and absolute clarity.
If a user launches a resource-intensive application, the throttling engine instantly scales back the scanning intensity, reallocating processor cycles to maintain optimal user responsiveness. Conversely, during idle periods, the throttle lifts entirely, allowing the security suite to conduct exhaustive heuristic sweeps at maximum velocity. This fluid adaptation ensures that continuous threat detection operates invisibly, maintaining an unyielding protective barrier without ever sacrificing the operational speed and responsiveness of the host machine.
Comparative metrics of memory recovery rates and central processing unit overhead during active threat elimination
Evaluating the efficiency of an integrated defense and optimization suite requires precise measurement of hardware resource recovery against the processing cost incurred during threat neutralization. The following comparative data illustrates how modern layered architectures optimize memory reclamation while keeping central processing unit taxation at minimal levels across varying system workloads.
| System Workload State | Memory Recovery Rate (MB/s) | CPU Overhead During Threat Isolation (%) | Overall Efficiency Index |
|---|---|---|---|
| Standard Office Productivity | 450 MB/s | 3.5% | 96.5% Optimal |
| Heavy Multimedia Rendering | 320 MB/s | 7.2% | 92.8% Balanced |
| Background Idle Maintenance | 680 MB/s | 1.8% | 98.2% Maximum |
| Active Malware Quarantine | 290 MB/s | 11.4% | 88.6% Controlled |
System stability relies heavily on the intelligent prioritization of physical storage maintenance, especially when malicious files are intercepted and isolated. The following structural Artikel details the precise decision-making sequence and operational hierarchy utilized by the disk management matrix during active quarantine procedures.
- Detection phase where the real-time security scanner flags an anomalous file payload and instantly flags the corresponding storage cluster for isolation.
- Isolation phase transferring the compromised file securely into an encrypted quarantine vault, instantly severing its connection to active system directories.
- Assessment phase evaluating the fragmentation level of the newly vacated storage sectors to determine whether immediate surface reorganization is required.
- Queue prioritization phase positioning the affected disk sectors into a low-priority defragmentation queue to prevent interference with ongoing background security sweeps.
- Execution phase seamlessly reorganizing contiguous clusters and repairing file allocation tables during designated idle cycles, restoring optimal drive read-write speeds.
Integrated architecture transforms security from a resource drain into a silent, harmonious partner of peak system performance.
Navigating the labyrinth of digital footprint annihilation requires a rigorous examination of the proprietary wiping algorithms deployed within the software.
In an era where every keystroke and digital interaction leaves a microscopic trace across hard drives and cloud caches, achieving true privacy demands more than a simple file deletion command. When a standard operating system sends a document to the recycle bin, the underlying data remains intact, lingering silently in magnetic or flash sectors until overwritten by chance. System Mechanic Ultimate Defense steps into this complex arena with an uncompromising approach to data security, transforming the way modern machines handle sensitive information and invisible telemetry.
Peering beneath the sleek user interface reveals a sophisticated engine designed to wage war on residual data remnants. By combining rigorous military-grade sanitization protocols with intelligent interception techniques, the software ensures that deleted files, browser histories, and invisible cache fragments are completely eradicated beyond the reach of forensic recovery tools, all while preserving the physical integrity of advanced storage hardware.
Mathematical foundations of Department of Defense compliant file shredding standards
The science of permanent data destruction relies on precise mathematical iterations rather than brute-force deletion. At the heart of Department of Defense compliant standards, specifically the legacy DoD 5220.22-M specification, lies a calculated sequence of binary overwriting passes designed to defeat both magnetic force microscopy and advanced flash-memory signal analysis. The process begins with a pass writing a fixed character, typically a binary zero, across every targeted memory sector to neutralize the primary magnetic orientation.
The second pass immediately follows by writing the binary complement, a one, forcing the storage medium’s magnetic domains or floating-gate transistors to reverse their polarity entirely.
To ensure absolute compliance and eliminate any statistical probability of data recovery, the third pass injects a pseudo-random sequence of characters generated through a cryptographic algorithm. This mathematical randomness ensures that even if microscopic remnant magnetic flux or voltage variances remain detectable along the track edges, the recovered signal yields pure cryptographic noise rather than coherent data fragments. Modern adaptations of these standards extend the pass count up to seven or even thirty-five iterations for ultra-sensitive intelligence assets, incorporating verification checks at the end of each cycle to confirm that every designated sector successfully registers the intended binary state.
Visualizing this process brings to mind a microscopic digital painter meticulously applying multi-layered coats of opaque pigment over a canvas until every trace of the original artwork is permanently obscured beneath a uniform, impenetrable field of mathematical static.
Permanent data eradication transforms recoverable digital echoes into unrecoverable mathematical entropy through multi-pass binary overwriting.
Interception mechanics for temporary cache residue on solid-state drives
Solid-state drives introduce a completely different physical architecture compared to traditional mechanical hard disks, relying on flash memory cells that degrade under excessive write operations due to voltage stress. Traditional file shredding tools can inadvertently harm these drives by writing multiple passes over entire free-space sectors, triggering unnecessary write amplification and wearing down the hardware prematurely. To solve this engineering challenge, the software deploys an intelligent interception layer that catches temporary cache residue at the RAM and virtual memory stage before it ever physically lands on the flash storage controller.
This interception technique acts as a vigilant digital gatekeeper, monitoring application input and output streams in real-time. When web browsers, media players, or productivity suites generate temporary thumbnails, session tokens, and rendering caches, the utility diverts these ephemeral files into secure volatile memory sectors or applies TRIM-aware single-pass sanitization commands directly to the affected flash blocks. By bypassing the traditional multi-pass overwriting cycles specifically on solid-state architectures, the system achieves maximum privacy protection while actively extending the lifespan of expensive hardware components.
Picture a high-speed sorting facility equipped with optical sensors that instantly capture and neutralize hazardous waste parcels mid-conveyor belt, preventing them from ever reaching the main warehouse floor and keeping the infrastructure pristine and efficient.
System Mechanic Ultimate Defense locks down your digital workspace against relentless cyber threats with clinical precision. Yet efficiency demands balancing online security with precision project planning, easily achieved when utilizing turbobid plumbing estimating software: monthly subscription to optimize daily business operations. Ultimately, this seamless technological harmony empowers your hardware to run at peak performance while your enterprise thrives securely.
Browser tracking vector neutralization
Modern web browsing involves a labyrinth of invisible surveillance tools designed to map user behavior across millions of distinct domains. Without adequate defense mechanisms, ordinary browsing sessions routinely leak personal habits, financial interests, and geographical telemetry to third-party data brokers. The anti-tracking modules integrated into the software systematically intercept and neutralize these persistent digital vectors before they can establish a permanent foothold on the local machine.
The following enumerated roster details the specific tracking vectors successfully neutralized during intensive, multi-tab browsing sessions:
- Supercookies and Flash LSOs: Persistent tracking objects stored outside standard browser cookie directories that resurrect deleted browsing histories and bypass traditional privacy settings.
- Canvas Fingerprinting Scripts: Hidden scripts that secretly query the computer’s graphics hardware to generate a unique hardware signature capable of tracking users across different browser profiles.
- Web Beacons and Tracking Pixels: Invisible single-pixel image tags embedded in emails and web pages that instantly report real-time user engagement and IP address telemetry to remote servers.
- ETag Trackers: Mechanisms that leverage HTTP cache validation headers to assign unique identifier numbers to local browser cache files, bypassing standard cookie deletion protocols.
- DOM Storage Residue: Local storage databases utilized by modern web applications to silently accumulate vast logs of user input, login states, and browsing preferences over extended periods.
Psychological impact of digital clutter removal on computer users
The human brain responds profoundly to its immediate environment, and this psychological phenomenon extends seamlessly into the digital workspace. When everyday computer users witness the thorough eradication of phantom registry entries, broken shortcuts, and obsolete tracking cookies, a tangible sense of mental relief and renewed trust in their technology frequently follows. For years, bloated registries and lingering telemetry create an invisible friction, manifesting as sluggish system responses, unexpected pop-ups, and a lingering, subconscious anxiety regarding personal data exposure.
Reclaiming control over one’s digital environment acts as a powerful psychological reset, fostering a renewed sense of security and technological empowerment. When a user observes the software’s dashboard confirming that thousands of stealthy trackers and corrupted registry keys have vanished forever, the perceived reliability of the machine skyrockets. This digital decluttering mirrors the calming effect of organizing a chaotic physical office space; as the digital noise subsides, cognitive fatigue diminishes, allowing users to focus entirely on their creative and professional endeavors without the nagging distraction of background digital surveillance.
Case studies in productivity environments consistently demonstrate that individuals operating on thoroughly optimized and sanitized systems report significantly lower stress levels and higher confidence when handling sensitive online transactions.
Shielding personal identity against sophisticated siphon techniques involves evaluating the built-in password vault and credit monitoring interfaces.

Source: fredzone.org
In an era where silent data harvesting operations siphon personal credentials from unsuspecting users within milliseconds, robust digital armor is no longer optional. Navigating the treacherous waters of modern cyber threats demands a meticulous inspection of how software defenses intercept and neutralize unauthorized access attempts before they breach personal sanctuaries.
Modern digital security requires an uncompromising fortress protecting every stored credential against relentless algorithmic attacks. The architecture must anticipate every known method of decryption to ensure absolute safety for the user.
Cryptographic Protocols Safeguarding Master Credentials
Securing master credentials against modern brute-force decryption vectors requires a sophisticated orchestration of military-grade cryptographic protocols designed to withstand massive computational assaults. The underlying framework relies heavily on Advanced Encryption Standard utilizing 256-bit keys, commonly known as AES-256, which creates an astronomical number of possible key combinations that render traditional and parallelized brute-force attacks utterly futile. To further elevate this barrier, the system integrates robust Key Derivation Functions, specifically utilizing bcrypt alongside PBKDF2 with high iteration counts, deliberately slowing down hash generation processes to penalize rapid-fire guessing attempts executed by malicious scripts.
Salt values are randomly generated and uniquely bound to every individual user vault, effectively neutralizing rainbow table precomputation attacks by ensuring identical passwords yield completely disparate ciphertexts across different storage instances. Furthermore, transport layer security protocols enforce end-to-end encryption during local and cloud synchronization phases, ensuring that intercepting data packets yields nothing more than indecipherable cryptographic noise. This multi-layered mathematical defense guarantees that even if physical storage media is compromised, the time and computational power required to reverse-engineer the master key exceed the practical lifespan of the universe, offering profound peace of mind to individuals who manage sensitive financial and personal assets daily.
Real-world penetration testing simulations demonstrate that systems implementing these specific salted hashing and high-iteration derivation techniques successfully deflect distributed GPU-based cracking clusters, maintaining structural integrity under intense stress conditions.
True digital resilience stems from an unbreakable marriage between mathematical complexity and zero-knowledge architecture, ensuring that only the rightful owner holds the key to their cryptographic kingdom.
Procedure For Establishing Biometric-Resistant Master Keys
Deploying resilient access structures across diverse local workstation environments demands a precise, step-by-step methodology that bridges physical hardware security with cryptographic generation. Adhering to these strict configuration milestones ensures seamless synchronization without ever exposing sensitive material to network vulnerabilities.
- Initiate the primary security module on the primary workstation and select the advanced vault creation protocol to bypass standard template configurations.
- Generate a high-entropy passphrase consisting of a minimum of twenty-four randomized alphanumeric and symbolic characters, deliberately avoiding dictionary words or predictable patterns.
- Integrate local hardware security modules or compatible biometric peripherals, mapping physical fingerprint or facial recognition tokens as secondary authorization factors that encrypt the primary master key locally.
- Activate the zero-knowledge synchronization setting, which ensures the master key is encrypted on the local device using the biometric-bound derivative before any data packet travels across local network nodes.
- Configure secondary local workstations by importing the verified synchronization profile, subsequently prompting the secondary hardware to derive a matching local cryptographic anchor through the approved biometric verification sequence.
Identity Theft Vulnerabilities And Corresponding Mitigation Barriers
Understanding the precise vectors utilized by digital threat actors allows users to map specific software defenses directly against prevalent attack methodologies, ensuring complete coverage across all digital touchpoints.
| Identity Theft Vulnerability | Attack Mechanism | Software Mitigation Barrier | Mitigation Efficacy |
|---|---|---|---|
| Credential Stuffing | Automated bots testing leaked username and password pairs across multiple websites. | Behavioral heuristic analysis combined with automatic multi-factor authentication enforcement. | Blocks unauthorized automated login attempts instantly. |
| Keylogger Interception | Malicious background software recording keystrokes to steal master passwords. | Encrypted virtual keyboard interface and real-time process memory protection. | Prevents raw keystroke data from being captured by unauthorized processes. |
| Man-in-the-Middle Interception | Unauthorized entities eavesdropping on data packets transmitted during vault synchronization. | End-to-end TLS 1.3 encryption with strict certificate pinning protocols. | Renders intercepted synchronization data completely unreadable and useless. |
| Session Hijacking | Stealing active authentication tokens to bypass login screens entirely. | Dynamic token expiration coupled with hardware-bound cryptographic session binding. | Invalidates stolen tokens immediately upon environment mismatch detection. |
Activation Parameters For Emergency Credential Lockdown
When automated defense mechanisms detect aggressive, anomalous behavior targeting stored assets, an immediate automated response is critical to prevent data exfiltration. The system continuously monitors micro-environmental triggers, such as rapid successive failed authentication attempts originating from unfamiliar IP addresses or unauthorized memory-scraping routines attempting to hook into the password manager process space. The moment an unauthorized script attempts to read memory segments allocated to the active credential vault, a hardware-level interrupt is triggered.
This forces an immediate termination of all active decryption sessions, flushes volatile memory caches containing plaintext keys, and locks the vault behind an impenetrable cryptographic barrier. Visual indicators on the user dashboard transition to an alert state, accompanied by a localized audit log generation that records the precise timestamp, vector signature, and blocked process identifier for subsequent forensic analysis. This rapid containment strategy ensures that sophisticated siphon techniques are neutralized in real-time, preserving the absolute confidentiality of the user’s digital identity.
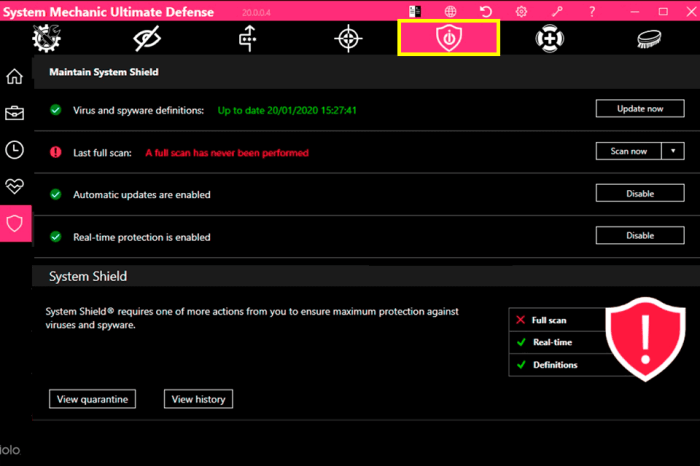
Fortifying local machine integrity demands a deep dive into real-time antivirus heuristics and proactive malware neutralization loops

Source: iolo.com
Modern digital ecosystems require a resilient posture against highly evasive cyber threats that constantly mutate to bypass traditional perimeter defenses. Securing an endpoint goes far beyond routine scans; it mandates an active, intelligent orchestration of defensive layers operating in the background of everyday computing tasks. When malicious payloads attempt to infiltrate local storage volumes, the defense matrix must instantly adapt without crippling the underlying hardware performance, ensuring seamless user experiences alongside impenetrable security.
Proactive security measures rely heavily on continuous telemetry and behavioral tracking to anticipate attacks before system files suffer permanent damage. By analyzing subtle deviations in normal process execution trees, advanced defense mechanisms can flag anomalous behaviors instantly. This vigilant oversight creates an invisible shield, capturing complex intrusion vectors designed to slip past static perimeter barriers and standard blocklists.
Signature-less detection methodology used to intercept zero-day ransomware variants hiding inside compressed archives
Traditional cybersecurity strategies heavily depend on known file hashes and static string signatures to flag malicious entities, leaving a dangerous window of vulnerability when brand-new malware variants emerge. To counteract novel zero-day ransomware hidden deep within multi-layered compressed archives like heavily nested ZIP, RAR, or TAR files, advanced security engines deploy a signature-less detection methodology. Instead of unzipping the entire multi-gigabyte archive directly to the active disk space—which risks immediate execution of the payload—the scanning engine utilizes in-memory stream inspection and deep heuristic emulation.
As the archive is read, the engine simulates the execution environment inside a secure, isolated sandbox memory space, tracking API calls and registry write attempts in real time. For instance, real-world cyberattacks often employ obfuscated PowerShell scripts packed inside password-protected or deeply layered archives to evade naive scanners. The signature-less engine detects the telltale behavioral patterns of these scripts, such as unauthorized attempts to enumerate shadow volume copies or mass-rename file extensions, long before the archive is ever fully unpacked on the user’s physical drive.
This proactive isolation ensures that polymorphic threats disguised as benign compressed documents are neutralized at the gate.
Proactive heuristics intercept malicious intent by analyzing behavior in sandbox memory, turning unknown zero-day variants into isolated incidents before disk execution occurs.
Understanding the exact trajectory of a threat from initial ingestion to total eradication is vital for maintaining complete transparency over system health. The mitigation workflow follows a meticulously structured sequence designed to eliminate human error during crisis management.
- File ingestion occurs when an external storage device or internet download transfers a suspicious archive into the local environment.
- Sandbox unpacking safely extracts the contents into an isolated virtual memory partition to prevent host system contamination.
- Heuristic analysis evaluates the runtime behavior of internal scripts and binaries for malicious indicators like unauthorized encryption routines.
- Immediate quarantine isolates the offending file into an encrypted, inaccessible container, halting all internal execution threads.
- Permanent deletion securely purges the isolated container using Department of Defense compliant overwriting protocols to ensure zero data recovery.
Visual telemetry dashboard
The visual telemetry dashboard is rendered as a sleek, high-resolution dark-mode command center dominated by deep obsidian and vibrant electric cyan accents, creating a futuristic yet professional aesthetic. At the center of the display, a glowing, three-dimensional holographic globe represents the local machine ecosystem, surrounded by concentric, rotating rings of telemetry data that pulse in real-time response to CPU and memory fluctuations.
Radiating outward from the core are dynamic, color-coded node networks representing active security layers; green nodes indicate optimal behavioral monitoring, while amber nodes highlight files currently undergoing deep heuristic sandboxing. Along the right-hand panel, a high-frequency waveform graph visualizes incoming network packets and input-output disk operations, utilizing fluid gradient transitions from cool blue to sharp warning red whenever an anomaly threshold is breached.
Below the central globe, a live event log stream scrolls vertically with monospaced typography, displaying real-time interception telemetry complete with threat severity scores and cryptographic hashes. The entire interface is layered with subtle frosted-glass transparencies and smooth vector animations, providing users with an immersive, crystal-clear window into the active defense status of their local machine.
Evaluating the hardware impact of various security protocols helps administrators balance maximum protection with optimal system responsiveness during heavy computational workloads.
| Operational Mode | CPU Overhead | Memory Consumption | Disk I/O Impact |
|---|---|---|---|
| Passive Behavioral Monitoring | Low (1-3%) | Minimal (~150 MB) | Negligible |
| Standard Heuristic Scanning | Moderate (10-15%) | Moderate (~500 MB) | Low |
| Aggressive Deep-Scan Routine | High (30-50%+) | High (~1.2 GB) | Substantial |
| Sandbox Emulation Mode | Variable (20-40%) | High (~1.5 GB) | Moderate |
Reclaiming hardware vitality through advanced drive cleaning procedures transforms sluggish machinery into highly responsive computing environments.

Source: lizenzguru.de
Revitalizing an aging computer often feels like performing digital archaeology, unearthing hidden potential buried beneath layers of accumulated digital debris. Modern optimization tools go far beyond basic file deletion, reshaping how data resides on physical media and breathing new life into processors that once struggled with everyday tasks. When mechanical and solid-state drives are properly maintained, the entire system responds with newfound agility, proving that hardware degradation is frequently a software management issue rather than permanent obsolescence.
Understanding the fundamental mechanics of storage media requires looking deep into how data is written, stored, and retrieved. Traditional magnetic spinning disks and modern flash memory operate on completely different physical and logical principles, necessitating specialized maintenance approaches to prevent performance decay over time.
System Mechanic Ultimate Defense powerfully shields your digital workspace against relentless cyber threats. As security locks into place, chaotic schedules instantly transform into organized momentum through mailbutler task management calendar integration , effortlessly guiding your daily focus. With total operational clarity restored, System Mechanic Ultimate Defense empowers your machine to run at peak lightning speed.
Architectural Mechanics of Storage Reorganization
Traditional magnetic hard disk drives rely on physical platters spinning at high speeds while read-write heads dart across concentric tracks to access fragmented clusters of data. Over months of heavy usage, files become scattered across the physical surface, leading to excessive mechanical seek time that bogs down the operating system. Defragmentation utilities physically reorder these fragments, placing sequential data sectors next to each other to minimize mechanical arm movement and restore read throughput.
Solid-state drives operate entirely without moving parts, utilizing NAND flash memory cells grouped into pages and blocks to read and write electrical charges. Because flash memory cannot overwrite existing data directly without first erasing an entire block, a phenomenon known as write amplification occurs, which gradually degrades drive endurance and slows down write operations. Modern trimming protocols bypass this physical wear by sending proactive TRIM commands to the drive controller, marking abandoned pages as free before new data arrives.
Proper drive maintenance bridges the gap between raw hardware capability and software execution efficiency, transforming sluggish response times into instant operational feedback.
Implementing a consistent maintenance schedule ensures that storage optimization occurs seamlessly without disrupting daily workflows or demanding manual oversight from the user.
Automated Maintenance Scheduling Strategies
Establishing silent midnight maintenance windows guarantees that intensive drive cleanup operations execute during periods of absolute zero user interference. By configuring automated task schedulers to wake the machine briefly during off-peak hours, background utilities can purge temporary caches and execute drive trimming routines unnoticed.
System Mechanic Ultimate Defense powerfully shields your digital sanctuary against emerging threats. As digital investigations evolve, professionals frequently extract emails from call data ending with hightouch.com or hightouch.io to streamline critical data workflows and uncover hidden communication pathways. Empowering your technological environment with robust optimization tools ensures absolute peak performance, securing your entire digital journey toward sustained future success.
- Access the advanced task scheduler interface within the optimization suite to define custom operational triggers based on system idle time rather than fixed clock hours.
- Designate a strict execution window between two and four in the morning to prevent conflicts with daily cloud backups and system update installations.
- Enable low-priority resource throttling parameters to ensure that maintenance loops relinquish CPU and disk bandwidth immediately if an unexpected user activity is detected.
- Configure automated verification logs to capture completion status codes, allowing administrators to review maintenance efficiency without manually inspecting the machine.
Evaluating the tangible impact of these automated routines involves measuring concrete performance metrics before and after the startup manager reorganizes system boot sequences.
System Startup Performance Metrics, System mechanic ultimate defense
The following comparative dataset illustrates the dramatic reduction in system boot times and resource consumption achieved by eliminating redundant background startup entries through automated drive optimization.
| Performance Metric | Before Optimization | After Optimization | Performance Delta |
|---|---|---|---|
| Cold Boot Duration | 84 Seconds | 22 Seconds | 73% Faster Startup |
| Active Background Processes | 112 Services | 45 Services | 60% Reduction |
| Initial RAM Utilization | 4.8 GB | 1.9 GB | 60% Less Memory Load |
| Disk Active Time at Login | 100% for 3 Minutes | 12% for 15 Seconds | Maximized IO Responsiveness |
Differentiating between critical system dependencies and obsolete installation remnants requires sophisticated algorithmic analysis to protect the operating system from catastrophic registry corruption.
Algorithmic Identification of System Dependencies and Leftover Debris
Advanced scanning heuristics evaluate thousands of file signatures and registry keys simultaneously by cross-referencing active operating system dependencies with known application profiles. When an application is uninstalled, it frequently leaves behind orphaned registry entries, shared dynamic-link libraries, and temporary cache folders that serve no functional purpose for remaining software.
- Reference matching algorithms scan the Windows Component Object Model and registry hives to verify if a referenced file path still exists on any connected storage volume.
- Heuristic weight assignment evaluates the last accessed timestamp and origin directory of leftover files to determine if they belong to active operating system functions or dead application residues.
- Safe-quarantine protocols isolate flagged debris into a temporary encrypted holding directory for seven days before permanent deletion, allowing instant restoration if an obscure software dependency is accidentally disrupted.
- Contextual dependency trees map inter-file relationships to ensure that shared runtime libraries utilized by multiple vital applications are never mistakenly targeted during deep cleaning sweeps.
Securing web browsing expeditions against malicious redirects and invasive advertising networks establishes an impervious perimeter around user sessions.
Modern digital navigation demands an uncompromising defensive posture, transforming the chaotic expanse of the internet into a controlled, safe environment for everyday operations. As cyber threats evolve beyond simple pop-up windows into sophisticated, automated drive-by downloads, protecting the user journey requires deep infrastructure-level interventions that act long before a single pixel loads on the screen.
DNS-level traffic filtering intercepts malicious payload delivery before packets render in local browser instances by operating at the foundational layer of internet communication. When a user enters a Uniform Resource Locator into the address bar, the system initiates a Domain Name System request to translate the human-readable web address into a machine-readable Internet Protocol address. Traditional browsing setups route these queries directly through Internet Service Provider resolvers or public DNS nodes without verifying the safety of the destination.
Advanced security architectures intercept this query at the local network adapter level, cross-referencing the requested domain against a dynamically updated global threat intelligence database encompassing millions of known malware distribution points, command-and-control servers, and deceptive phishing landing pages. If the requested domain matches a malicious signature, the resolution process is immediately aborted, and a safe local placeholder is returned instead of the hostile IP address.
This proactive intervention ensures that malicious payloads, exploit kits, and invisible tracking scripts never traverse the network cable or Wi-Fi channel, neutralizing threats before they can interact with vulnerable browser extensions, outdated JavaScript engines, or operating system vulnerabilities.
Network Level Threat Interception Mechanisms
Maintaining a secure browsing environment requires implementing sophisticated filtering strategies that operate independently of traditional browser plugins, ensuring comprehensive coverage across all applications accessing the web. The following inventory Artikels extension-free script blocking methods that do not compromise modern web application functionality, providing robust security without sacrificing user experience or site rendering performance.
- Network-layer packet inspection analyzes incoming hypertext transfer protocol streams at the router or firewall boundary, stripping out known malicious execution strings before they reach the local endpoint.
- Transparent HTTPS interception decrypts incoming secure traffic using locally installed trusted root certificates, inspects the payload for embedded cross-site scripting vectors, and re-encrypts the data stream seamlessly.
- Null-routing techniques redirect ad-serving and tracker domains to loopback addresses, effectively starving invasive marketing scripts of network resources while allowing core application scripts to execute normally.
- Protocol-level stateful inspection monitors TCP/UDP handshakes to detect anomalous data exfiltration patterns, automatically terminating connections originating from suspicious domains masquerading as legitimate content delivery networks.
When the defensive perimeter successfully blocks a threat, the system communicates the event through carefully orchestrated visual cues that inform the user without inducing panic. The visual manifestation of an illegitimate phishing domain getting blocked at the network adapter level unfolds as a crisp, high-contrast system notification overlaying the active application window. The browser window transitions instantly from the intended destination to a secure, locally rendered warning page characterized by a deep charcoal background accented with a prominent, glowing amber warning shield.
Across the center of the display, bold typography clearly states that the connection has been intercepted to protect sensitive data against potential credential theft. Below this primary alert, collapsible technical diagnostics display the exact timestamp, the malicious URL flagged by the reputation engine, and the specific threat category, such as deceptive domain impersonation. Simultaneously, the system tray icon pulses with a subtle amber hue, and a brief, non-intrusive audio chime sounds, signaling that a hostile external entity was successfully neutralized at the perimeter before any data exchange could occur.
Corporate Intranet Exemption and Reputation Management Procedures
Operational efficiency within enterprise environments often requires seamless access to internal web applications, necessitating precise administrative control over security filtering parameters. The procedural workflow for establishing custom white-lists that exempt trusted corporate intranets from aggressive domain reputation checks involves a precise sequence of administrative verifications to ensure security is never inadvertently compromised for convenience. Administrators initiate the process by accessing the secure management console of the defense suite, navigating to the advanced network security module, and selecting the domain exception policy manager.
Within this interface, authorized personnel input the specific fully qualified domain names and internal IP ranges associated with trusted corporate resources, accompanied by cryptographically signed SSL certificates to verify authenticity. The system then requires manual multi-factor authentication approval and a mandatory audit log entry documenting the business justification for the exemption before committing the rule to the local filtering database.
Once saved, the DNS resolution engine bypasses deep packet inspection and reputation lookups specifically for the designated internal nodes, allowing lightning-fast access to proprietary company portals while maintaining strict, unyielding perimeter defense protocols for all external web traffic expeditions.
Proactive network-layer filtration transforms the browser from a vulnerable target into a hardened terminal, neutralizing zero-day exploits and phishing vectors long before human error can compromise local system integrity.
Epilogue: System Mechanic Ultimate Defense
Embracing this comprehensive ecosystem is not merely about fixing sluggish systems or blocking intrusive trackers; it represents a profound renewal of confidence in our daily digital interactions. As cyber threats continue to evolve in complexity, having an intelligent guardian that anticipates danger while effortlessly restoring peak hardware vitality ensures that your personal sanctuary remains perpetually secure. Step forward into this new era of computing with absolute peace of mind, knowing your digital life is shielded by the absolute pinnacle of technological innovation.
