zix email encryption emerges quietly as a vital shield in our hyper-connected world, safeguarding sensitive conversations as they traverse vast, unseen digital pathways. Every single day, organizations face daunting challenges in protecting their most private communications from persistent cyber threats, making robust technological defenses an absolute necessity rather than a mere luxury.
Beneath the surface of everyday digital correspondence lies a sophisticated architecture of cryptographic mechanics, administrative frameworks, and regulatory safeguards designed to preserve absolute confidentiality. By exploring these intricate security layers, we uncover not only the technical brilliance required to keep data safe but also the empowering assurance that our most critical messages will always reach their intended destinations untouched and secure.
Unraveling the cryptographic mechanics behind Zix email encryption reveals how confidential messages travel securely across modern digital networks.
Beneath the seemingly effortless simplicity of clicking send on a sensitive electronic message lies an intricate choreography of advanced digital protection mechanisms. When confidential communication traverses the vast expanse of interconnected global servers, it is constantly exposed to interception, making the implementation of robust cryptographic safeguards an absolute necessity for modern digital correspondence. Through a sophisticated fusion of mathematical algorithms and secure routing pathways, the architecture transforms vulnerable text into unreadable ciphertext that can only be deciphered by the intended recipient.
The journey of a secure message begins the moment the author finalizes their thoughts and initiates transmission, triggering a cascading series of security protocols designed to lock the data away from prying eyes. This continuous protection relies on a harmonious blend of speed and impenetrable security, ensuring that sensitive corporate intellectual property, medical records, and financial disclosures remain shielded from sophisticated cyber threats lurking within open network environments.
Underlying cryptographic protocols safeguarding messages during transit
The foundation of secure digital transit relies heavily on robust transport layer security protocols that establish an encrypted tunnel between the originating mail client and the destination server. As the electronic envelope leaves the safety of the local network, Transport Layer Security version 1.3 actively negotiates a secure handshake, verifying the identities of both communicating parties before a single byte of actual message data is transmitted across the open web.
This rigorous handshake process utilizes ephemeral Diffie-Hellman key exchange mechanisms to generate unique session keys for every distinct communication session, meaning that even if an adversary manages to compromise a key at a later date, past and future transmissions remain completely safe from retroactive decryption.
Once the secure tunnel is successfully established, the data stream is continually wrapped in cryptographic envelopes that incorporate advanced hashing functions like SHA-256 to guarantee message integrity. These hashing algorithms generate a unique mathematical fingerprint of the payload before transmission, which the receiving server instantly recalculates upon arrival to confirm that the text has not been intercepted, manipulated, or altered in transit by malicious intermediaries.
Furthermore, forward secrecy ensures that compromise of long-term private keys does not compromise past session keys, fortifying the digital perimeter against persistent eavesdroppers who harvest encrypted traffic today with the hope of decrypting it using tomorrow’s quantum computing advancements.
True digital confidentiality is achieved only when data in motion is guarded with the same mathematical rigor applied to data resting in secure offline vaults.
End-to-end delivery workflow across network nodes
Understanding the multi-tiered transit process requires observing how a message transitions through distinct operational phases, moving from initial composition to final authorized decryption by the recipient. The following table delineates the precise responsibilities handled across different nodes within the secure architecture.
| Sender Actions | Server Routing | Recipient Decryption |
|---|---|---|
| Composes confidential text, attaches documents, and clicks the designated secure send button within the native email client interface. | Intercepts outbound transmission, evaluates compliance policies, and wraps the payload in an encrypted transport layer tunnel. | Receives the secure notification or direct message payload, authenticates identity via multi-factor credentials, and unlocks the content locally. |
| Applies local cryptographic sealing, utilizing the system’s generated symmetric session key before the data officially leaves the device. | Navigates public and private relay nodes using obfuscated headers to prevent metadata leakage and traffic analysis by outside observers. | Executes the private key retrieval sequence, matching the digital certificate to successfully revert the ciphertext into readable plain text. |
Certificate authority validation sequence through trust verification steps
Establishing absolute trust between disparate mail servers requires a strict hierarchical validation sequence managed by recognized certificate authorities. This systematic verification prevents man-in-the-middle attacks by ensuring that communicating servers are precisely who they claim to be before exchanging any sensitive encryption parameters.
- The initiating mail server presents its digital certificate to the receiving gateway during the initial connection handshake.
- The recipient system cross-references the presented root certificate against a pre-installed, trusted store of globally recognized certificate authorities.
- An automated online certificate status protocol query is dispatched in real-time to confirm the current validity and rule out any unexpected revocations.
- Upon successful cryptographic validation of the digital signatures, a mutual trust relationship is formally established, enabling the safe exchange of encrypted session keys.
Symmetric versus asymmetric encryption algorithms utilized within the platform architecture
The architectural brilliance of modern secure email systems lies in their hybrid employment of both symmetric and asymmetric cryptographic algorithms, leveraging the distinct advantages of each methodology. Asymmetric encryption, utilizing public and private key pairs based on complex mathematical problems such as RSA or Elliptic Curve Cryptography, is primarily employed during the initial handshake and authentication phases to securely exchange session keys without risking exposure over public networks.
This mathematical complexity makes asymmetric methods computationally heavy, which is precisely why they are reserved for the critical task of key establishment rather than processing entire message bodies.
Once the secure channel and session keys are established, the architecture transitions seamlessly to high-speed symmetric encryption algorithms, predominantly Advanced Encryption Standard utilizing a 256-bit key length. Symmetric encryption uses the exact same key for both locking and unlocking the data, offering phenomenal processing speeds capable of instantly encrypting massive attachments and extensive message threads without introducing noticeable latency for the end-user.
Zix email encryption safeguards sensitive digital conversations with unwavering precision, shielding confidential messages from prying eyes. As professionals constantly seek robust software upgrades, exploring alternatives via tools like pct matchcad reveals dynamic pathways to enhance operational security and workflow efficiency. Embracing these innovative advancements ultimately empowers your organization to master total data privacy through reliable Zix email encryption protocols.
By combining the secure key distribution of asymmetric cryptography with the lightning-fast processing power of symmetric ciphers, the system achieves an optimal balance between uncompromising security and seamless operational efficiency in high-volume enterprise environments.
Organizations deploying Zix email encryption frequently encounter intricate deployment hurdles that demand careful administrative planning and precise execution.
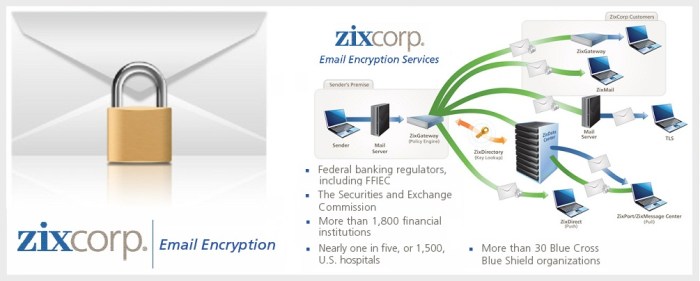
Source: ansnetworks.com
Stepping into the realm of enterprise communication security often feels like navigating a sprawling, high-stakes labyrinth under the cover of dusk. System administrators charged with deploying advanced cryptography find themselves holding the architectural blueprints to a digital fortress, where every single foundational brick must be laid with absolute precision. Behind the polished facade of seamless encrypted messaging lies a complex web of directory synchronizations, routing adjustments, and boundary defenses that test the patience of even the most seasoned IT professionals.
This grand undertaking requires a harmonious blend of foresight, technical rigor, and an unwavering commitment to operational resilience.
The journey begins long before the first secure message ever traverses the wire, demanding a deep appreciation for the invisible gears turning beneath the surface of enterprise infrastructure. Organizations that underestimate the sheer gravity of initial configuration parameters frequently stumble into costly delays, dropped message threads, and authentication bottlenecks. Picture a vast, luminous control room filled with cascading digital dashboards, where administrators trace glowing data pathways across global networks, meticulously tightening every security protocol.
Success in this domain is forged through rigorous preparation, transforming potential vulnerabilities into impenetrable bastions of trust.
Infrastructural roadblocks during initial tenant configuration
Embarking on the initial tenant configuration for enterprise email encryption introduces administrators to a cascade of infrastructural roadblocks that can severely strain existing resources. At the very core of these challenges lies the synchronization of global directory services, such as Microsoft Entra ID or traditional Active Directory, with the cloud-hosted encryption gateway. Administrators frequently grapple with latency issues, schema mismatches, and fragmented user attribute mapping that prevent the system from accurately recognizing who holds the authorization to send and receive confidential payloads.
When directory synchronization falters, user provisioning grinds to a halt, leaving large segments of the workforce stranded without the ability to securely dispatch sensitive outbound correspondence.
Compounding these directory hurdles is the intricate labyrinth of routing policy adjustments and certificate management. Provisioning the tenant requires the careful generation, validation, and binding of Transport Layer Security certificates to ensure end-to-end data integrity. If a single intermediate certificate is missing or untrusted along the validation chain, external mail servers reject the handshake entirely, resulting in silent message drops.
Furthermore, administrators must redesign their inbound and outbound mail flow rules to route traffic through the encryption relay without triggering internal mail loops or exceeding relay connection thresholds. Visualizing this environment reveals a delicate ecosystem where a single misaligned parameter can cascade across thousands of concurrent mail sessions, demanding exhaustive log analysis and real-time packet inspection to isolate the root cause.
Beyond directory and routing complications, storage allocation and journaling configurations present significant hurdles during the early deployment phase. Archiving encrypted streams requires dedicated storage tiers that comply with stringent regulatory frameworks like HIPAA or GDPR, yet integrating these repositories with legacy retention policies often creates severe bottlenecks. Administrators must calculate anticipated message volume spikes, factoring in payload expansion caused by cryptographic encapsulation.
Real-life enterprise migrations vividly illustrate this friction; for instance, a multinational financial institution moving fifty thousand mailboxes to a secure encryption tenant recently experienced a temporary mail queue saturation because their journal rules attempted to process unindexed encrypted attachments simultaneously. Overcoming these barriers requires deliberate pacing, phased rollout strategies, and continuous stress testing before cutting over live production traffic.
Diagnostic framework for deployment troubleshooting, Zix email encryption
System administrators require a systematic diagnostic approach to rapidly isolate and neutralize anomalies that emerge during the deployment lifecycle. The following structured table provides a comprehensive troubleshooting framework designed to address the most frequent operational friction points encountered in enterprise environments.
| Symptom Identification | Diagnostic Checks | Resolution Paths | Prevention Strategies |
|---|---|---|---|
| Outbound messages bypassing encryption policies and leaving the network in plaintext. | Inspect outbound connector routing tables and evaluate header tags using SMTP trace tools. | Reconfigure transport rules to explicitly force TLS and update domain routing match criteria. | Implement strict pre-deployment validation scripts to test routing rules against a sandbox tenant. |
| External recipients reporting inability to access secure web portal notifications. | Verify DNS CNAME records for branding portals and test external HTTPS handshake validity. | Correct DNS propagation delays and renew expired web service SSL certificates on the proxy. | Establish automated certificate expiration monitoring and rigorous DNS health check routines. |
| Directory synchronization failures resulting in orphaned user accounts. | Review synchronization agent event logs and audit user attribute mappings in the LDAP schema. | Restart the sync service, clear local cache files, and re-establish secure API credentials. | Schedule regular health audits of directory schemas and maintain up-to-date documentation. |
Proactive mitigation methods for domain name system mail exchanger record misconfigurations
Domain Name System infrastructure serves as the primary navigation map for internet mail routing, making the precision of Mail Exchanger records an absolute necessity for secure messaging. A single typographical error or improper priority weighting can instantly reroute confidential data streams into unmonitored digital corridors, exposing an organization to severe data leakage risks. Adopting a proactive stance toward DNS management ensures that incoming and outgoing cryptographic handshakes occur smoothly without interruption.
System administrators can successfully eliminate DNS-related vulnerabilities and maintain pristine routing integrity by adhering to the following strategic checklist:
- Audit existing DNS zones comprehensively to verify that all MX records point directly to the designated secure encryption gateway rather than legacy mail servers.
- Implement strict Time-To-Live reduction strategies twenty-four hours prior to migration to accelerate global record propagation and minimize downtime windows.
- Deploy Sender Policy Framework, DomainKeys Identified Mail, and Domain-based Message Authentication, Reporting, and Conformance protocols concurrently with MX adjustments to safeguard domain reputation.
- Execute automated external DNS lookup queries from geographically diverse vantage points to confirm record consistency across public resolvers.
- Maintain a version-controlled backup of all zone files to facilitate immediate rollback procedures should unexpected routing anomalies occur post-implementation.
Precision in DNS record architecture transforms a vulnerable routing pathway into an impenetrable digital highway, guaranteeing that cryptographic tokens arrive precisely where intended without interception.
Zix email encryption fiercely guards confidential messages behind an impenetrable digital armor of trust. As enterprises modernize operations, upgrading infrastructure through voip contact center solutions empowers dynamic teams to converse seamlessly across global channels. Ultimately, robust zix email encryption remains the ultimate shield, ensuring every single piece of sensitive correspondence stays perpetually secure and private.
Legacy mail server synchronization challenges and network firewall exceptions
Integrating modern cloud-based encryption architecture with aging on-premises infrastructure introduces a profound architectural dissonance that tests organizational agility. Legacy mail servers, often running outdated operating systems or proprietary mail protocols, lack the native API hooks required to communicate fluently with contemporary cryptographic tenants. Administrators find themselves constructing intricate middleware bridges and protocol translators just to allow older systems to participate in modern security workflows.
This technological friction inevitably leads to session timeouts, protocol downgrade attacks, and synchronization failures that disrupt everyday business operations.
Simultaneously, navigating network firewall exceptions around legacy boundaries requires a surgical approach to perimeter defense. Security policies must be meticulously rewritten to permit secure outbound SMTP traffic over port 587 and inbound TLS connections over port 465, all while maintaining strict inspection protocols against malicious payloads. If a legacy firewall drop rule inadvertently blocks the specific IP ranges utilized by the encryption service, entire communication channels freeze instantly.
Visualizing this physical perimeter reveals rows of heavy steel server racks guarded by rigid, uncompromising software firewalls that must be carefully coaxed into granting safe passage to encrypted data streams. Achieving this delicate balance demands close collaboration between network security teams and messaging administrators, ensuring that rigid perimeter defenses evolve gracefully to support advanced organizational cryptography.
Navigating regulatory compliance landscapes becomes significantly less burdensome when utilizing Zix email encryption tools designed for sensitive data governance.

Source: uapguide.com
Stepping into the intricate world of digital data protection often feels like walking a tightrope above a canyon of legal liabilities, yet modern organizations find steadfast ground through dedicated security frameworks. Healthcare providers and financial institutions face relentless scrutiny from federal overseers, where a single mishandled message can trigger devastating financial penalties and irreparable reputational damage. Within bustling hospital corridors and high-stakes trading floors, communication remains the lifeblood of daily operations, carrying a continuous stream of Electronic Protected Health Information and Non-Public Personal Information across vulnerable digital corridors.
Addressing these formidable challenges requires a robust infrastructure capable of transforming ordinary email into an impenetrable fortress of confidentiality. Healthcare entities operating under the Health Insurance Portability and Accountability Act must guarantee absolute data integrity and restricted access, while financial pillars bound by the Gramm-Leach-Bliley Act face parallel mandates regarding consumer privacy. By implementing Zix email encryption, these institutions weave a protective digital tapestry that intercepts unencrypted outbound traffic, automatically wraps sensitive transmissions in military-grade transport layer security, and stores messages safely behind multi-factor authentication portals.
A vivid mental snapshot depicts a cascading waterfall of digital data abruptly intercepted by a glowing, sapphire-blue biometric gatekeeper, filtering out unauthorized digital footprints while allowing authorized clinical and financial insights to flow smoothly to their intended destinations without ever exposing the underlying payload to interception.
Healthcare and Financial Sector Mandates
Navigating the complex mandates established by federal regulators demands an uncompromising commitment to technical safeguards and administrative oversight. Healthcare institutions leverage this secure messaging infrastructure to satisfy the strict requirements of the HIPAA Security Rule, ensuring that patient diagnostics, treatment plans, and insurance records remain strictly confidential during transit. Meanwhile, banking establishments and wealth management firms rely on the exact same underlying architecture to comply with the safeguarding provisions of the GLBA, preventing unauthorized access to customer account balances, social security numbers, and credit histories.
Real-world implementations across major metropolitan hospital networks demonstrate that automated policy enforcement drastically reduces human error, successfully blocking staff members from inadvertently dispatching unencrypted patient lists to personal webmail domains.
Organizations must establish rigorous verification routines to maintain continuous alignment with evolving federal standards and avoid catastrophic compliance failures. The foundational elements of a successful compliance posture depend heavily on proactive administrative oversight and routine system inspections. To achieve complete operational transparency during federal audits, security administrators must execute a structured series of checks and balances.
- Deploying mandatory cryptographic filters across all outward-facing mail servers to eliminate accidental plaintext disclosures of sensitive records.
- Conducting quarterly access log reviews to verify that only authorized personnel possess decryption credentials for restricted repositories.
- Enforcing strict password rotation intervals and mandatory multi-factor authentication parameters for all external message recipients accessing secure portals.
- Scheduling automated vulnerability assessments to detect and patch potential cryptographic handshake weaknesses before malicious actors exploit them.
Data Retention and Purging Policies
Maintaining regulatory alignment extends far beyond the moment of transmission, requiring meticulous management of digital lifecycles through systematic data retention and automatic purging protocols. Federal frameworks dictate exact timeframes for preserving historical communications, demanding that organizations neither delete records prematurely nor hoard obsolete information indefinitely. The following matrix Artikels the regulatory parameters, retention windows, and archiving protocols typically enforced within enterprise environments.
| Regulation Type | Retention Window | Archiving Protocol |
|---|---|---|
| HIPAA Administrative Simplification | Six Years from Creation Date | Immutable WORM Storage with Cryptographic Hashing |
| GLBA Safeguards Rule | Five Years for Consumer Privacy Disclosures | Indexed Cloud Vaulting with Automated Lifecycle Tags |
| Sarbanes-Oxley Act Financial Records | Seven Years for Audit and Accounting Documents | Tamper-Evident Long-Term Archival Repositories |
Personally Identifiable Information Policy Rule Creation
Proactive defense against data exfiltration relies heavily on the granular configuration of automated policy rules designed to intercept Personally Identifiable Information before it leaves the corporate perimeter. Security architects construct precise regular expression filters within the encryption engine to scan subject lines, message bodies, and digital attachments for specific patterns such as nine-digit social security numbers, credit card sequences, and medical record identifiers.
When the system detects a matching pattern, it immediately triggers a remediation action, either automatically encrypting the outbound message, routing it to a compliance officer for manual review, or blocking the transmission entirely with an bounce-back notification.
Systemic data governance succeeds not through occasional vigilance, but through the seamless integration of automated cryptographic rules that protect sensitive communications without hindering operational velocity.
Institutions frequently deploy customized dictionary matching alongside standard regular expressions to capture industry-specific terminology, such as specific medical billing codes or proprietary financial account nomenclature. This multi-layered inspection methodology ensures that even deeply embedded or obfuscated data elements are successfully captured and secured prior to crossing public network boundaries.
End users interacting with encrypted message notifications often experience friction that modern organizational training programs must systematically eliminate.

Source: softwaresuggest.com
Digital communication security relies heavily on the final recipient successfully navigating the encrypted delivery mechanism, yet this vital handoff frequently breaks down due to unexpected human and operational roadblocks. When an external partner or a patient receives a secure message notification, the journey from their standard inbox to the reading pane is rarely straightforward, turning what should be a seamless interaction into a stressful hurdle.
Organizations must look beyond backend configuration to address the lived reality of everyday users who find themselves locked outside the perimeter of confidential data exchanges. Transforming this critical juncture requires deep empathy for the recipient’s daily workflow and a systematic educational framework that banishes digital intimidation.
Psychological barriers and operational confusion
Opening an encrypted message often triggers an immediate sense of distrust and cognitive overload for unsuspecting recipients. When a notification arrives bearing unfamiliar branding or demanding the creation of an unexpected web portal account, many users suspect a phishing campaign rather than a legitimate business communication. This instinctive skepticism is completely rational given the relentless wave of cyber threats targeting modern digital channels, causing recipients to hesitate, stall, or simply delete critical corporate correspondence out of an abundance of caution.
Operational confusion compounds these psychological deterrents through clunky interface designs and rigid authentication demands. Recipients suddenly face multi-step verification processes, unexpected password creation rules, and expired links that break the natural rhythm of business operations. For an overwhelmed client or a busy medical professional, managing yet another proprietary login credential feels like an unwelcome chore that drains productivity and strains professional relationships.
Companies that fail to account for this friction experience high drop-off rates, delayed responses, and a pervasive frustration that undermines the very purpose of deploying enterprise-grade encryption tools.
Safeguarding sensitive correspondence through zix email encryption remains paramount today, much like creators expanding their digital canvas by downloading the procreate app for windows to unleash boundless artistic potential. Embracing these innovative breakthroughs empowers professionals to protect vital communications fearlessly while simultaneously unlocking remarkable new realms of boundless digital creativity and secure productivity.
Systematic user education bridges the gap between stringent security requirements and human usability, turning anxious recipients into confident participants in secure communication workflows.
Intuitive onboarding manual structure for first-time credential registration
Guiding external stakeholders through their initial secure interaction demands a clear, reassuring roadmap that removes all guesswork from credential establishment. Structured onboarding sequences transform an intimidating technical barrier into an approachable, standardized routine that builds long-term user confidence.
While securing communications through zix email encryption remains vital, modern enterprises must also protect physical assets by budgeting for a camera inventory system cost small business implementation to prevent onsite losses. Balancing these digital safeguards and physical investments unlocks unprecedented operational resilience, ensuring zix email encryption continues to empower your enterprise growth securely.
- Receive the encrypted notification email and click the prominent secure message access button to initiate the connection.
- Review the welcome splash screen that clearly displays the sending organization’s authentic identity to instantly alleviate phishing concerns.
- Select the registration option to establish a secure profile, entering a valid email address and setting a compliant passphrase using real-time validation indicators.
- Check the inbox for an automated verification token, paste the numeric code into the activation prompt, and immediately enter the primary secure message viewing portal.
Visual layout description of the recipient portal dashboard interface
The secure portal dashboard presents a clean, minimalist aesthetic characterized by a sophisticated palette of deep navy and crisp slate gray accents that communicate immediate authority and data protection. Upon successful authentication, the recipient is greeted by a centralized message staging area dominated by an uncluttered reading pane situated directly in the center of the viewport. A fixed left-hand navigation sidebar features understated monochromatic icons for incoming messages, sent archives, and account settings, ensuring that critical navigation options remain persistently accessible without visual clutter.
The typography utilizes highly legible sans-serif fonts optimized for rapid scanning, while status indicators employ soft amber and muted green badges to denote message confidentiality tiers and expiration countdowns. Subtle white space frames every interactive element, consciously guiding the human eye away from extraneous chrome and directly toward the core decrypted content, thereby reinforcing a calm, professional, and secure reading environment.
Authentication methodology performance matrix
Evaluating the operational trade-offs between traditional password systems and modern verification workflows reveals distinct impacts on user experience and organizational overhead, as detailed in the comparative matrix below.
| Authentication Method | User Effort | Security Level | Administrative Overhead | Deployment Speed |
|---|---|---|---|---|
| Traditional Password | High (Remembering complex strings) | Moderate (Vulnerable to reuse/phishing) | High (Frequent password reset tickets) | Slow (Extensive initial user guidance) |
| One-Time Passcode (OTP) | Low (Frictionless code entry) | High (Ephemeral, single-use tokens) | Low (Automated token generation) | Fast (Immediate intuitive adoption) |
| Federated Single Sign-On | Minimal (Existing corporate credentials) | Very High (Enterprise identity control) | Moderate (Directory synchronization) | Moderate (Complex initial configuration) |
| Client-Side Certificates | Extremely High (Manual installation) | Maximum (Hardware-backed trust) | Severe (Rigid device management) | Very Slow (High friction rollout) |
Integrating Zix email encryption alongside existing enterprise security information and event management systems strengthens overall threat visibility and incident response capabilities.
Modern digital enterprises operate within complex threat landscapes where data breaches originate from subtle, coordinated intrusions across multiple communication vectors. Connecting cryptographic email infrastructure directly into centralized security monitoring platforms transforms isolated message flows into actionable intelligence, empowering defensive teams to intercept sophisticated attacks before sensitive intellectual property leaves the organizational perimeter. By bridging the gap between secure messaging and enterprise-wide event correlation, security architects illuminate blind spots that traditional perimeter defenses routinely miss, establishing a resilient posture capable of withstanding advanced persistent threats.
Security operations centers require continuous, high-fidelity data streams to maintain situational awareness across distributed network environments. The telemetry data export mechanisms engineered into enterprise encryption platforms leverage standardized protocols such as Syslog over TLS, secure file transfer protocols, and robust RESTful APIs to stream real-time event logs directly into centralized security information and event management solutions like Splunk, IBM QRadar, or Microsoft Sentinel.
These telemetry export pipelines package critical cryptographic events, user authentication attempts, policy violation flags, and message delivery statuses into structured formats including JSON and Common Event Format. Security analysts configure these ingestion channels by establishing secure forwarding agents on dedicated gateway nodes, ensuring that every handshake, decryption failure, and administrative modification is securely transmitted without introducing latency or compromising payload confidentiality.
As enterprise traffic scales to millions of messages daily, these export mechanisms dynamically manage buffer allocations and retry queues, guaranteeing zero telemetry loss even during network disruptions or high-volume phishing campaigns targeting executive mailboxes.
Telemetry Data Ingestion and Parsing Procedures
Translating raw cryptographic event streams into structured, queryable security insights demands rigorous log parsing procedures that isolate relevant telemetry from background system noise. Security engineers deploy custom regular expression parsers and parsing configurations within their central event collectors to normalize disparate log formats into unified threat schemas.
- System administrators track repeated authentication failures originating from external IP addresses, mapping these occurrences to potential credential-stuffing campaigns targeting the secure messaging portal.
- Monitoring engines parse policy enforcement logs to detect sudden spikes in unencrypted outbound messages containing classified financial markers, signaling potential insider data exfiltration attempts.
- Log collectors analyze cryptographic handshake failures and certificate expiration warnings, generating immediate alerts to prevent service outages and potential man-in-the-middle interception vulnerabilities.
- Automated routines inspect administrative role-elevation events and policy modification timestamps, ensuring that unauthorized configuration changes to decryption rules are flagged instantly.
- Security tools evaluate message revocation requests and bulk download anomalies, identifying compromised end-user credentials before unauthorized actors harvest sensitive archived attachments.
Automated Threat Triage and Remediation Playbooks
Executing swift containment actions upon detecting a security anomaly minimizes dwell time and prevents catastrophic data loss across enterprise communication channels. The following response matrix Artikels systematic triage protocols for high-priority cryptographic events detected through integrated monitoring platforms.
| Threat Category | Severity Rating | Automated Remediation Action |
|---|---|---|
| Brute Force Portal Access | High | Trigger immediate IP quarantine at the web application firewall and enforce temporary account lockout for targeted end-user profiles. |
| Unauthorized Policy Alteration | Critical | Revert cryptographic configuration settings to the last known secure baseline, revoke compromised administrative tokens, and dispatch high-priority page to the security operations center. |
| Certificate Expiration Warning | Medium | Initiate automated certificate renewal request via internal Public Key Infrastructure integration and notify system administrators via secure ticketing channel. |
| Mass Message Exfiltration | Critical | Suspend outbound mail queue for the affected user account, terminate active user sessions, and initiate forensic memory capture for incident analysis. |
Administrative Best Practices for Key Rotation and Access Control
Maintaining the integrity of cryptographic communications requires rigorous lifecycle management of private keys and strict enforcement of the principle of least privilege across administrative tiers. Enterprise security architects must implement automated key rotation schedules that replace primary encryption and signing keys on a strict ninety-day cadence, minimizing the window of vulnerability should a key be compromised. Cryptographic material must be generated inside tamper-resistant hardware security modules that adhere to Federal Information Processing Standards validation levels, ensuring that private keys never exist in plaintext memory or unencrypted storage volumes.
Administrative access to the encryption management console should require phishing-resistant multi-factor authentication, such as hardware-based FIDO2 security keys, combined with role-based access control policies that segregate duties between policy configuration, key management, and log auditing. Regular access reviews must be conducted monthly to prune dormant administrative accounts and verify that elevated privileges are granted strictly on a time-bound, need-to-know basis.
Comprehensive audit trails recording every administrative action must be exported to an immutable, write-once-read-many storage repository to satisfy strict regulatory compliance frameworks and support forensic investigations should a security incident occur. Organizations implementing these rigorous governance standards successfully neutralize internal and external threats, ensuring that their encrypted communication channels remain impenetrable fortresses of trust in an increasingly hostile digital ecosystem.
Last Word

Source: ansnetworks.com
Ultimately, mastering the art of secure digital communication transforms how organizations build trust and protect their most vulnerable data across every boundary. As we embrace these advanced cryptographic safeguards and intuitive user experiences, a brighter and far more resilient digital future remains entirely within our grasp.
