competitors mentioned on g2 page pirani reviews 2026 stand as brilliant beacons of transformation across digital boardrooms, illuminating a vast landscape where modern enterprises bravely redefine their governance futures. Peer review ecosystems pulse with vital intelligence, acting as trusted lighthouses for decision-makers navigating stormy compliance seas. Every single click across these dynamic directories tells a compelling story of ambition, resilience, and the relentless pursuit of operational excellence.
Behind every star rating and detailed testimonial lies a meticulous journey of software discovery, where leaders compare functional metrics, pricing tiers, and integration capabilities side by side. As organizations evaluate their digital options, the collective voice of users shapes the very foundation of tomorrow’s risk management strategies.
Uncovering alternative risk management software platforms featured alongside Pirani user evaluations for the year two thousand twenty-six requires a thorough examination of peer review ecosystems.

Source: piranirisk.com
Navigating the turbulent waters of enterprise software procurement demands robust navigational instruments, and contemporary digital marketplaces have fundamentally transformed how organizations discover critical business applications. As corporate governance grows increasingly complex, enterprise leaders no longer rely solely on vendor-supplied prospectuses or traditional marketing collateral to make high-stakes technology investments. Instead, they turn toward transparent, community-driven discovery engines that capture authentic operational experiences, illuminating the true day-to-day value of compliance ecosystems.
G2 has firmly established itself as the premier digital amphitheater where enterprise software buyers converge to dissect, evaluate, and benchmark governance solutions. Within this vast ecosystem, prospective buyers find a sanctuary of unbiased peer insights, where verified practitioners openly share architectural triumphs and operational friction points alike. The platform operates as an indispensable discovery engine by distilling thousands of individual user data points into actionable intelligence, scoring applications across usability, implementation velocity, and customer support responsiveness.
When organizations seek to fortify their internal controls, scanning these aggregated user sentiment dashboards reveals the hidden nuances that traditional vendor demonstrations routinely gloss over, empowering procurement committees to make decisions rooted in collective industry reality.
Peer review portal filtering methodologies
Enterprise software buyers deploy precise, multi-layered criteria to isolate viable risk applications from the broader marketplace noise, transforming overwhelming choices into manageable shortlists. This analytical process relies on systematic data reduction, ensuring that only solutions matching specific organizational scales and industry verticals remain in contention.
- Buyers initiate the filtration sequence by segmenting software according to verified company size tiers, ensuring the shortlisted applications possess the structural scalability to handle enterprise-grade workloads without performance degradation.
- Reviewers isolate specific functional modules, such as incident management, business continuity planning, or vendor risk assessment, to verify that candidate platforms directly address their primary compliance vulnerabilities.
- Decision-makers apply geographic and regulatory compliance filters, identifying platforms that natively support regional frameworks like GDPR, HIPAA, or ISO standards relevant to their operating environments.
- Implementation timeframe parameters are factored into the filter matrix, allowing organizations to discard platforms requiring prohibitive deployment windows in favor of agile, rapidly configurable alternatives.
Visualizing this analytical sorting process helps clarify how modern compliance architects translate raw marketplace data into strategic asset acquisition.
Enterprise software selection is no longer an exercise in feature accumulation, but a precise alignment between peer-validated operational reliability and long-term strategic resilience.
The interface of a modern software comparison portal resembles a high-resolution command center, where dynamic filters cast sharp spotlights on niche capabilities. Users glide across interactive sliders to adjust pricing thresholds while simultaneous data visualizations redraw themselves in real-time, mapping user satisfaction scores against deployment complexity quadrants. Crisp typography highlights verified badges next to reviewer profiles, while collapsible feature matrices expand smoothly to reveal granular integrations with legacy enterprise resource planning tools.
Contemporary software comparison interface evaluation metrics
Evaluating enterprise platforms requires a standardized set of comparative vectors to ensure apples-to-apples assessment across competing technological architectures. The following matrix Artikels the foundational pillars utilized by modern compliance evaluation interfaces.
| Metric Category | Primary Focus Area | Measurement Vector | Enterprise Impact |
|---|---|---|---|
| Usability Index | User interface design and navigation efficiency | Time-to-proficiency and daily active usage rates | Accelerates user adoption and minimizes training costs across departments |
| Implementation Index | Deployment velocity and technical onboarding | Weeks from contract signing to production go-live | Reduces time-to-value and mitigates operational disruption during transition |
| Relationship Index | Vendor support quality and partnership depth | Customer satisfaction scores and account manager responsiveness | Ensures long-term platform viability and rapid resolution of critical compliance blocks |
| Results Index | Measurable return on investment and risk reduction | Percentage reduction in compliance audit findings and efficiency gains | Justifies software expenditure to executive boards and regulatory bodies |
Behind these structural metrics lies an evolving corporate mindset, driven by professionals who view compliance technology not as a static administrative burden, but as a dynamic engine for sustainable growth.
Shifting operational risk professional expectations
Operational risk professionals operating in today’s high-velocity regulatory climate demand intelligent, predictive digital compliance solutions that transcend traditional reactive reporting frameworks. This evolutionary leap in expectations stems from the increasing frequency of complex cyber threats, macroeconomic volatility, and tightening global mandates that require continuous monitoring rather than periodic audits. Industry leaders at institutions like JPMorgan Chase and multinational supply chain conglomerates increasingly pilot automated control testing frameworks that synthesize external threat feeds with internal incident logs in real-time.
While industry analysts dissect rivals highlighted across recent G2 Pirani assessments, modern risk teams are shifting their gaze toward brilliant new horizons. By exploring ocula.tech product features dashboards , organizations unlock vibrant visual metrics that illuminate hidden pathways to success. Ultimately, this cutting-edge clarity redefines benchmarks, overshadowing the traditional limitations typically debated in standard G2 Pirani reviews.
These forward-thinking practitioners reject monolithic, siloed databases in favor of composable, API-driven risk ecosystems that integrate seamlessly with existing DevOps pipelines and cloud infrastructure.
Furthermore, compliance officers expect artificial intelligence and machine learning primitives to be natively embedded within their risk applications, shifting the professional focus from manual data entry to strategic vulnerability remediation. Platforms must now demonstrate the capability to autonomously categorize emerging operational risks, predict potential control failures before they manifest as financial losses, and generate executive-ready visualizations instantly. As the boundary between operational resilience and digital transformation dissolves, the modern risk manager demands intuitive tools that empower cross-functional collaboration, turning risk awareness into an enterprise-wide cultural asset.
Evaluating rival compliance tech ecosystems mentioned within Pirani feedback threads reveals unexpected patterns in enterprise adoption.

Source: g2crowd.com
Modern enterprises navigate an increasingly labyrinthine landscape of regulatory demands, where traditional compliance mechanisms frequently fracture under the sheer weight of operational data. When modern risk officers gather in digital corridors to exchange candid feedback, their shared frustrations paint a vivid picture of legacy platforms buckling beneath complex multi-jurisdictional mandates. Beneath the polished veneer of standard enterprise software, organizations are encountering persistent friction points that transform routine audits into grueling endurance tests.
The pursuit of resilient governance structures compels decision-makers to look past standard vendor brochures and scrutinize peer-driven feedback ecosystems. Within these vibrant discussion spaces, operational realities collide with marketing promises, exposing the exact friction zones where businesses stumble and begin actively seeking out alternative digital safeguards.
Operational Bottlenecks Driving Alternative Software Exploration
Organizations migrating away from entrenched compliance workflows consistently highlight three major structural failures that severely paralyze daily risk operations. Understanding these specific pain points illuminates why forward-thinking companies abandon traditional pathways in favor of more agile, modern compliance architectures.
- Steep learning curves and rigid user interfaces create massive adoption friction among non-technical departmental stakeholders, drastically slowing down organization-wide risk reporting initiatives.
- Severe integration friction prevents seamless synchronization with existing enterprise resource planning systems, forcing compliance teams into inefficient manual data entry routines that invite costly human errors.
- Opaque pricing tiers and unpredictable scaling costs trap growing businesses in restrictive licensing agreements that fail to deliver proportional value as risk portfolios expand globally.
These mounting operational roadblocks transform minor annoyances into critical business vulnerabilities, forcing compliance leaders to re-evaluate their entire technological foundation.
Comparative Analysis of Risk Mitigation Software Ecosystems
Market evaluation heavily relies on direct feature contrasts, where buyers weigh advanced analytics capabilities against core governance functionality to determine long-term operational viability.
| Software Ecosystem | Core Risk Engine | Integration Flexibility | User Adoption Index |
|---|---|---|---|
| Pirani | Standardized matrix mapping | Moderate API accessibility | Intuitive baseline interface |
| MetricStream | Advanced predictive modeling | Enterprise-grade connectivity | Steep learning curve |
| AuditBoard | Collaborative audit workflows | Robust native integrations | High cross-departmental adoption |
Impact of Peer Review Commentary on Enterprise Procurement Strategies
Decision-making within the enterprise compliance sector has fundamentally shifted away from traditional top-down sales pitches toward decentralized, community-driven validation processes. When procurement committees evaluate potential software investments, authentic peer narratives found on public evaluation platforms carry significantly more weight than glossy promotional materials.
Real-world implementation war stories shared by frontline risk managers expose hidden software limitations and deployment pitfalls that vendor demonstrations routinely conceal. Consequently, enterprise risk budgets are increasingly allocated based on verified peer consensus rather than executive preference.
As industry rivals spark debate across G2 software listings, professionals often wonder about does fieldworker.pl have a blog to share expert insights and industry updates. Uncovering these hidden digital resources empowers growing teams to make brilliant software choices, ultimately turning fierce market competition into a clear roadmap for future operational success.
Authentic peer reviews act as the ultimate corporate lie detector, stripping away marketing hype to expose how compliance software actually performs under extreme operational pressure.
This reliance on collective intelligence accelerates the evaluation cycle, allowing procurement teams to bypass subpar solutions and rapidly shortlist platforms proven to handle complex regulatory burdens efficiently.
Visual Architecture of Modern Software Evaluation Profiles
The digital layout of a contemporary peer review profile is meticulously engineered to guide the human eye through a structured hierarchy of trust signals and comparative data points. At the very top of the interface, a prominent overall satisfaction score anchors the page, flanked by verified user volume metrics and category badges that instantly establish platform credibility.
Immediately below the header section, the page unfolds into a dynamic, multi-column comparison matrix that places competing software features side by side across critical operational dimensions. Visual progress bars represent satisfaction ratings for specific sub-attributes such as customer support responsiveness, deployment speed, and custom reporting capabilities. Surrounding these quantitative metrics, modular user review cards display verified job titles and industry tags, allowing evaluators to filter feedback directly by peer groups that mirror their exact organizational profile.
Mapping out the competitive perimeter surrounding Pirani through recent software rating platform disclosures uncovers hidden market dynamics.

Source: g2.com
Digital risk management ecosystems are shifting rapidly as organizations demand sharper tools to navigate complex regulatory environments. Deep inside peer review repositories, professional communities dissect enterprise software capabilities with surgical precision, revealing an intricate chess match between legacy players and agile disruptors.
Feature parity discussions dominating contemporary software forums represent far more than mere checklist comparisons between competing platforms. When compliance officers and risk analysts debate the exact nuances of incident tracking modules or risk matrix configurability, they are signaling a profound maturation of the governance, risk, and compliance marketplace. Users no longer accept superficial similarities; they scrutinize the depth of automation workflows, API connectivity robustness, and real-time dashboard responsiveness.
This intense scrutiny acts as a powerful catalyst for product development, forcing vendors to accelerate innovation cycles just to maintain perceived parity on public ranking directories. Furthermore, these digital conversations expose the psychological tipping points of enterprise software buyers. A single recurring complaint regarding reporting limitations on a popular review board can instantly trigger widespread market migration, altering enterprise adoption curves overnight and reshaping the competitive perimeter for platforms operating in this specialized vertical.
Migration friction points between enterprise risk platforms
Transitioning from one sophisticated risk management framework to another involves navigating a labyrinth of technical and operational hurdles. Organizations frequently underestimate the hidden resistance embedded deep within legacy data structures and entrenched user habits during enterprise platform migrations.
- Data mapping discrepancies cause unexpected formatting errors when legacy historical incident records fail to align with the rigid schema requirements of modern destination architectures.
- Custom workflow configurations built over years of internal operational adjustments cannot always be replicated out-of-the-box, demanding costly bespoke scripting or process redesign.
- User adoption bottlenecks emerge immediately when teams trained on familiar interface paradigms face steep learning curves, temporarily paralyzing ongoing risk assessment initiatives.
- License overlap costs bleed enterprise budgets dry as organizations are forced to maintain parallel subscriptions for both legacy and incoming platforms during prolonged data verification phases.
- Integration fragility breaks crucial automated feeds connecting the risk tool to enterprise resource planning systems, creating dangerous blind spots in real-time threat monitoring.
Proprietary module positioning strategies within software directories
Enterprise software vendors continuously refine their market positioning within online directory ecosystems to outshine entrenched market leaders and capture high-intent buyer traffic. Emerging challengers systematically isolate specific functional gaps found in legacy architectures and spotlight their own proprietary modules as essential modern antidotes.
By leveraging targeted feature highlights and verified customer success metrics, innovative compliance platforms reframe standard risk assessment tasks into high-performance digital transformation journeys. Market incumbents counter these strategic intrusions by emphasizing enterprise-grade security certifications and extensive historical stability, creating a fascinating contrast between agile modern capability and proven corporate reliability. Review platforms vividly capture this ongoing strategic positioning dance, offering market observers a transparent window into how modern compliance technologies fight for dominance in crowded digital marketplaces.
Triggers for compliance framework evaluation
Enterprise decision-makers rarely initiate software replacement cycles on a whim; instead, their journeys toward alternative risk frameworks are propelled by distinct operational frustrations. Pinpointing these exact catalysts helps industry observers understand the shifting loyalties documented across software rating channels.
Escalating licensing costs combined with rigid tiered pricing models often serve as the primary financial trigger that forces organizations to audit competing marketplace offerings. When an organization outgrows its current software capacity, inflexible user seat caps and prohibitive data storage fees quickly transform a once-favored platform into an operational liability. Additionally, sluggish customer support response times during critical compliance audit windows generate immense internal dissatisfaction.
Compliance teams working under unforgiving regulatory deadlines cannot afford multi-day ticket resolution delays when critical risk assessment modules malfunction.
Enterprise software migration is rarely a spontaneous leap; it is a calculated escape driven by cumulative operational friction, uncompromising regulatory pressures, and the pursuit of genuine technological synergy.
Technical debt accumulation further accelerates the migration impulse, especially when legacy vendors neglect necessary user interface modernizations or fail to release timely integrations for emerging regulatory frameworks. Disappointed users vocalize these shortcomings on peer evaluation networks, creating a public trail of dissatisfaction that immediately alerts competing vendors to pounce on vulnerable enterprise accounts.
Recent market evaluations tracking rivals highlighted on the g2 page pirani reviews 2026 reveal a fascinating shift toward transparency. Organizations frequently explore the mission behind complyflow.com about us to discover how innovative compliance frameworks empower teams. By embracing these evolving industry standards, forward-thinking enterprises surpass expectations set by alternatives featured on the g2 page pirani reviews 2026.
Investigating contemporaneous software alternatives discovered through Pirani rating profile cross-references illuminates broader industry trends
The digital marketplace for governance, risk, and compliance infrastructure has entered a fascinating phase of maturity, where peer review ecosystems serve as diagnostic lenses for enterprise software evolution. When analyzing cross-referenced evaluations across major software discovery portals, distinct patterns emerge regarding what modern risk officers demand from their daily operational tooling. Moving beyond traditional feature checklists, today’s compliance leaders evaluate platforms through the rigorous prism of user experience, architectural responsiveness, and seamless integration capabilities.
Recent G2 insights highlight fierce rivals against Pirani, prompting a sharp industry pivot toward specialized solutions like indyforms target industries and personas. This strategic clarity empowers modern professionals to overcome digital hurdles with remarkable precision. Ultimately, analyzing these dynamic market shifts redefines how brands successfully navigate the competitive landscape outlined in upcoming feedback platforms.
This systemic shift reflects a deeper cultural transformation within corporate risk management departments, where digital adoption directly correlates with employee retention and operational resilience.
Analyzing the historical trajectory of user interface preferences among risk officers reveals a profound departure from the dense, multi-tabbed, data-heavy dashboards that dominated corporate compliance software a decade ago. Chief risk officers and operational analysts now operate under high-velocity environments, requiring platforms that distill complex threat matrices into intuitive, glanceable visual indicators. The modern risk practitioner spends less time manually inputting data and more time orchestrating strategic mitigation protocols, meaning software interfaces must prioritize cognitive ease and frictionless navigation.
Reviewers frequently penalize platforms that retain legacy, utilitarian designs, noting that cumbersome workflows directly hinder incident response times during critical audit cycles.
Furthermore, the democratization of software procurement within enterprises has placed executive leadership and frontline analysts in shared digital workspaces. Consequently, interface design must gracefully accommodate dual-persona utilization: high-level executive summaries for board-level reporting sitting adjacent to granular, configurable parameter controls for daily risk practitioners. This demand for adaptive layout structures has forced software developers to abandon rigid static panels in favor of modular, widget-based command centers.
The evolution heavily favors solutions offering dark-mode variants for long audit sessions, context-aware tooltips that minimize the need for external documentation, and drag-and-drop hierarchy builders for risk taxonomy mapping. Real-life deployments at multinational financial institutions demonstrate that platforms prioritizing these ergonomic principles achieve significantly higher daily active usage rates and notably faster employee onboarding metrics.
To navigate the complex ecosystem of modern governance and compliance suites, enterprise architects rely on structured comparative data regarding cost structures and deployment flexibility. The following table maps out these operational parameters across leading contemporary alternatives in the risk management market.
| Compliance Suite | Primary Deployment Model | Pricing Tier Structure | Core Target Enterprise Size |
|---|---|---|---|
| Pirani | Cloud-Native SaaS | Modular / Usage-Based | SMB to Mid-Market |
| LogicManager | Multi-Tenant Cloud | Annual Subscription | Mid-Market to Enterprise |
| MetricStream | Hybrid Cloud / On-Premise | Enterprise License Agreement | Global Fortune 500 |
| Resolver | Secure Cloud Infrastructure | Tiered User-Based Model | Mid-Market to Large Enterprise |
Enterprise Software Comparison Visual Dashboard Layout
Evaluating multi-vendor metrics requires a sophisticated visual interface that synthesizes quantitative risk scores with qualitative vendor performance indicators. A comprehensive software comparison dashboard presents this complex data through a series of synchronized, high-contrast graphical elements designed for rapid executive comprehension.
The visual architecture of modern risk platforms must transform abstract threat probabilities into immediate, actionable operational intelligence.
The central viewport of the interface features an interactive, multi-dimensional scatter plot where competing compliance suites are mapped dynamically across axes representing total cost of ownership and implementation velocity. Surrounding this central matrix, collapsible modular widgets display real-time API uptime statistics, modular customization scores derived from user reviews, and predictive compliance forecasting curves. Color-coded heatmaps utilize restrained emerald, amber, and crimson palettes to indicate vulnerability density across different deployment architectures.
Typography is strictly minimalist, employing high-legibility sans-serif fonts to ensure that numerical values and performance indices remain instantly readable even on compact mobile supervisory displays.
Unique Value Propositions Highlighted by Competitor Reviewers
Peer review ecosystems consistently highlight specific differentiators that elevate certain compliance platforms above standard market offerings. Understanding these core strengths provides valuable context for software selection committees aiming to align technical capabilities with long-term organizational strategy.
- Reviewers frequently praise platforms that offer highly intuitive, no-code workflow builders, allowing risk officers to autonomously adapt incident escalation paths without requiring dedicated IT intervention.
- Several competing solutions earn high marks for native regulatory intelligence feeds that automatically update internal control frameworks in response to shifting international compliance mandates.
- Advanced collaborative commenting features integrated directly into risk heatmaps receive strong commendation from distributed teams requiring transparent cross-departmental accountability.
- Granular role-based access control configurations are repeatedly noted as a critical asset for enterprises managing stringent data privacy boundaries across multiple global jurisdictions.
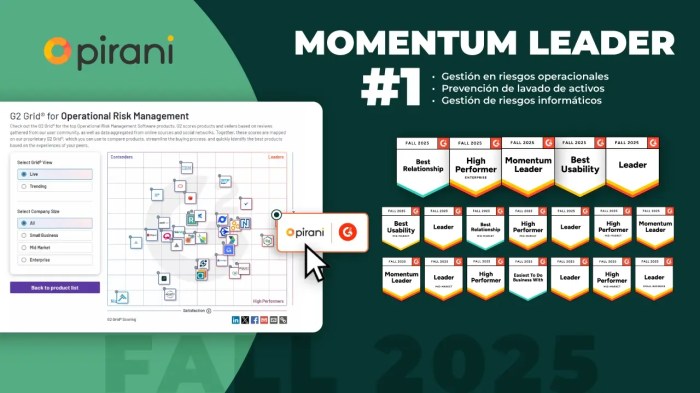
Dissecting the competitive landscape referenced inside Pirani satisfaction metrics provides a clear lens on modern enterprise needs.
Source: piranirisk.com
When enterprise leaders log onto peer assessment portals to evaluate risk management frameworks, the digital footprint they leave behind reveals a fascinating narrative of shifting corporate priorities. Behind every star rating and qualitative user review lies a deeper story about how organizations struggle to balance regulatory demands with operational agility. By analyzing the nuanced feedback embedded within software satisfaction profiles, industry observers can uncover the exact friction points that drive organizations either toward legacy platforms or into the arms of nimble innovators.
This continuous digital dialogue acts as a real-time market barometer, charting the exact trajectory of enterprise risk governance.
The modern boardroom demands technology that functions not merely as a system of record, but as an active engine of strategic foresight. Risk management software can no longer operate in a silo, detached from everyday enterprise workflows and agile project management tools. As regulatory frameworks multiply in complexity across global jurisdictions, compliance officers find themselves drowning in manual data collection unless their chosen platforms offer seamless automated controls.
Examining these satisfaction metrics uncovers a clear dichotomy between static risk registers and dynamic ecosystems capable of predicting vulnerabilities before they materialize into costly operational failures.
Integration capabilities defining software market differentiation
The chasm separating second-tier compliance applications from true market leaders is rarely measured by the sheer volume of features, but rather by the architectural grace with which those features connect to the broader corporate tech stack. Elite compliance platforms distinguish themselves through bi-directional API ecosystems that synchronize effortlessly with enterprise resource planning systems, human capital management databases, and cloud infrastructure monitors.
While secondary tools often rely on rigid, batch-scheduled data exports that leave compliance teams operating on delayed intelligence, industry leaders maintain real-time telemetry pipelines. For instance, when a multinational financial institution updates its cloud security architecture, a market-leading governance platform instantly ingests those configuration changes, automatically mapping them against relevant regulatory frameworks such as ISO 27001 or SOC 2 without requiring human intervention.
This eliminates the latency that typically plagues compliance audits, transforming risk mitigation from a retrospective scramble into a continuous, automated posture. Furthermore, advanced platforms leverage extensible webhooks and pre-built connectors that drastically reduce implementation timelines from months to mere weeks. They empower internal engineering teams to construct custom risk workflows without breaking native data integrity. Conversely, lesser-known alternatives frequently stumble upon proprietary data silos, forcing IT departments to engineer costly, fragile middleware integrations that constantly break during routine software updates.
This architectural disparity explains why discerning enterprise buyers consistently prioritize native integration depth over superficial feature lists when evaluating long-term software investments.
The visual landscape of a top-tier integration dashboard often resembles a living nerve center, pulsing with color-coded data streams that map the exact velocity of risk data moving between disparate corporate departments. Imagine a high-resolution, dark-mode administrative console where glowing nodes represent distinct software endpoints—such as GitHub repositories, Salesforce CRM instances, and AWS security buckets—all feeding a central risk engine in real-time.
Lines of data pulse steadily across the interface, instantly turning amber or crimson the moment an anomaly is detected in an upstream system. This visual immediacy stands in stark contrast to the static, spreadsheet-like interfaces of legacy tools, where administrators must manually refresh tables to discover that an integration script failed overnight. Such architectural elegance directly influences user adoption rates, as compliance analysts naturally gravitate toward tools that mirror the responsive, interconnected nature of their day-to-day digital environments.
Customer support responsiveness across rival software providers
Evaluating the human element behind enterprise software requires looking closely at how vendors handle critical system outages, implementation roadblocks, and ongoing user education. The table below Artikels the support infrastructure and response efficacy of prominent compliance technology providers based on recent aggregate user feedback.
| Provider Tier | Average Ticket Resolution Time | Dedicated Customer Success Manager | Support Channel Availability |
|---|---|---|---|
| Market Leaders | Under 4 hours | Provided for all enterprise accounts | 24/7 Live Chat, Phone, and Priority Ticketing |
| Mid-Market Challengers | 12 to 24 hours | Available for top-tier subscriptions only | Email and Scheduled Video Consultation |
| Second-Tier Alternatives | 48 hours or longer | Rarely assigned | Async Ticketing Portal Only |
Psychological factors driving cross-platform software reviews
Enterprise software buyers do not make purchasing decisions in a vacuum, and the phenomenon of cross-pollinating feedback between competing applications stems from deep-seated psychological triggers. When compliance officers experience acute pain points—such as sudden price hikes, abandoned feature roadmaps, or inadequate customer support—they frequently channel their frustrations into comparative reviews across multiple vendor profiles. This behavior is fueled by a desire for validation and a protective instinct within the professional community, where practitioners feel a shared obligation to warn peers about hidden operational traps.
- Reviewers often project their dissatisfaction with one vendor onto competing platforms to highlight industry-wide shortcomings in user interface design.
- The cognitive bias of recency heavily influences feedback, causing users who experienced a major audit failure to disproportionately penalize a vendor’s reporting capabilities.
- Professional pride drives many evaluators to showcase their deep industry expertise by publicly dissecting the architectural flaws of rival compliance tools.
- A sense of collective industry solidarity encourages buyers to reward transparent vendors by cross-referencing their positive experiences when rating alternative solutions.
Technical prerequisites prioritized during online peer commentary evaluations, Competitors mentioned on g2 page pirani reviews 2026
Modern software evaluators sift through digital peer commentary with a rigorous checklist, hunting for specific technical validations that prove a platform can withstand corporate scrutiny. Before committing capital to a risk management system, technical evaluators look past marketing claims to examine how reviewers describe backend performance under heavy enterprise loads. They know that a platform must not only look sleek during a sales demonstration but also maintain structural integrity when processing millions of transactional risk data points concurrently.
- Reviewers meticulously scan commentary for mentions of multi-tenant cloud security protocols, encryption standards, and independent SOC 2 Type II audit verifications.
- Particular attention is paid to user permission hierarchies, ensuring the software supports granular role-based access control necessary for strict regulatory compliance.
- Evaluators search for real-world feedback regarding database scalability, verifying whether the platform experiences performance degradation as historical risk data accumulates over multi-year audit cycles.
- The presence of robust audit logging features within the software architecture is consistently cited as a non-negotiable prerequisite for maintaining internal accountability.
True enterprise resilience emerges not from avoiding risk entirely, but from deploying adaptive compliance architecture that turns unexpected friction into a measurable strategic advantage.
Ultimate Conclusion: Competitors Mentioned On G2 Page Pirani Reviews 2026

Source: g2crowd.com
Ultimately, traversing this intricate web of enterprise software evaluations unveils an inspiring truth about the power of informed choices. When organizations embrace transparency and peer insights, they unlock limitless potential to elevate their operational resilience and build a remarkably secure tomorrow.
