em client linux represents a long-awaited horizon for open-source enthusiasts yearning for seamless personal information management. For years, communities have whispered across developer forums and digital corridors, demanding native compatibility that bridges the profound gap between proprietary workspace solutions and standard kernel distributions. Today, we stand on the precipice of a new era in desktop productivity, where the rigid walls separating operating systems are slowly beginning to crumble under the relentless pursuit of unified communication.
Navigating the complex landscape of modern digital workspaces requires more than just functional tools; it demands a harmonious ecosystem where emails, calendars, and tasks dance to the exact same rhythm. As developers and power users alike engineer ingenious pathways through emulation layers and translation tools, the dream of effortless workflow integration transforms into tangible reality. Every keystroke and synchronized schedule brings us closer to a future where productivity knows no architectural boundaries.
Enthusiasts have long awaited a native installation package for running this specific personal information manager on open-source operating systems
The landscape of desktop productivity has long been defined by a silent digital divide, separating proprietary platforms from the vast, collaborative expanses of open-source environments. For over a decade, power users navigating alternative operating systems have cast an expectant gaze toward robust desktop clients that promise seamless synchronization of mail, calendars, and tasks. This anticipation represents more than a mere software preference; it embodies a philosophical commitment to customizable computing where users truly own their workflow.
As modern professionals navigate open source desktops, mastering em client linux brings remarkable clarity to daily coordination. Transitioning operations smoothly often requires upgrading background infrastructure, prompting businesses to adopt a reliable pos system for liquor store management. Ultimately, pairing robust retail architecture with the seamless communicative power of em client linux empowers forward thinking enterprises to achieve unprecedented efficiency.
As modern workspaces increasingly demand unified communication hubs, the absence of an officially supported package on standard penguin-themed distributions has left a palpable void in the productivity ecosystem. Enthusiasts and enterprise adopters alike have continuously voiced their desire for an integrated experience, transforming a routine utility request into a legendary grassroots campaign for cross-platform parity.
The historical trajectory of community appeals for alternative platform compatibility reveals a deeply passionate user base determined to unify their digital lives under a single interface. Traceable back to the early days of forum boards and public feature request trackers, the demand for a native Linux client gained tremendous momentum as developers transitioned from proprietary webmail wrappers to dedicated desktop applications.
Users argued that managing complex schedules and encrypted correspondences required the deep system-level integration that only a locally compiled package could provide. Throughout successive major version releases, community threads swelled with thousands of upvotes, passionate testimonials, and constructive architecture proposals, establishing eM Client as one of the most frequently requested additions to the open-source software repository. This sustained advocacy reflects a broader cultural shift within enterprise and personal computing, where users increasingly reject artificial platform lock-in in favor of fluid, hardware-agnostic productivity tools.
Technical barriers preventing direct desktop integration
Bridging the gap between proprietary application frameworks and standard kernel distributions involves navigating a labyrinth of underlying architectural divergences. The core challenge stems from heavy reliance on proprietary rendering engines, proprietary API hooks, and Windows-specific .NET presentation frameworks that lack direct, native equivalents in standard widget toolkits like GTK or Qt. Compiling the application natively requires a massive refactoring effort to decouple the user interface logic from the underlying operating system libraries.
Furthermore, system security models, keyring management implementations, and hardware acceleration pipelines vary drastically across different distributions, introducing profound complexity into the software deployment cycle.
To better understand these intricate engineering roadblocks, examining the specific layers of divergence illuminates why a simple recompilation is mathematically and structurally impossible without substantial codebase rewrites. The following breakdown highlights the primary system components that complicate straightforward desktop integration:
- Proprietary runtime dependencies tie core performance metrics directly to specific proprietary operating system libraries, necessitating entirely new abstraction layers for alternative kernels.
- Graphics rendering pipelines rely on specialized hardware acceleration hooks that translate differently across modern display servers like Wayland and X11.
- Credential management protocols require extensive rebuilding to interface securely with native desktop keyrings such as GNOME Keyring or KWallet instead of Windows Credential Manager.
- Filesystem hierarchy standards differ significantly regarding configuration paths, temporary caching directories, and localized application data storage conventions.
Bridging software availability gaps through emulation layers
When native installation packages remain unavailable, the open-source community frequently engineers ingenious workarounds to deploy Windows-centric applications on standard POSIX-compliant kernels. Developers and advanced administrators typically rely on sophisticated translation layers, compatibility tools, and containerized runtime environments to simulate the necessary API calls on the fly. These solutions intercept proprietary system calls and map them directly to native system calls, allowing complex graphical suites to execute with minimal performance overhead.
Through the strategic implementation of compatibility utilities like Wine, Proton-based derivatives, and specialized container containers, users can effectively bridge the digital divide while maintaining their preferred operating environment.
Visualizing this software bridge involves imagining a sophisticated translation engine sitting quietly between the application binary and the host kernel, meticulously translating foreign instructional languages into native commands. Real-world deployments often feature a dedicated wineprefix environment configured with specific Windows Presentation Foundation libraries, ensuring that fonts, encryption certificates, and background database sync engines execute without crashing. This methodology transforms an inaccessible executable into a functional daily driver, proving that human ingenuity can temporarily bypass corporate platform exclusivity.
Compatibility is not merely a technical workaround; it is the digital manifestation of user sovereignty, reclaiming operational freedom where official support falls short.
To evaluate the practical implications of running productivity suites across diverse operating environments, administrators must carefully analyze functional performance limitations, hardware resource consumption, and integration fidelity. The comparative data below Artikels how these factors manifest across standard desktop operating paradigms.
| Operating Environment | Native Integration Level | Resource Overhead | Hardware Acceleration |
|---|---|---|---|
| Target Native Platform | Complete and Seamless | Low to Moderate | Fully Optimized |
| Compatibility Layer (Linux) | Functional via Emulation | Moderate to High | Variable / Direct X Translation |
| Containerized Environment | Isolated Sandbox | Moderate | Indirect Rendering |
| Virtual Machine Host | Complete OS Isolation | Extremely High | Emulated GPU Passthrough |
Alternative desktop productivity suites often struggle to replicate the exact calendar synchronization protocols found in proprietary workspace solutions.
Achieving seamless digital organization across diverse operating systems remains one of the most persistent hurdles in modern software engineering. While proprietary ecosystems effortlessly bind calendars, contacts, and tasks into a unified cloud experience, open-source alternatives frequently encounter friction when bridging these complex data streams. Users transitioning to community-driven platforms often find that meeting invitations stall, recurring events fracture, and reminders fail to trigger simultaneously across mobile and desktop environments.
Bridging this technological gap requires a profound understanding of the underlying mechanics governing time management data exchange, secure connection pipelines, and intelligent threat mitigation within modern enterprise workflows.
The foundation of multi-device scheduling harmony relies on sophisticated synchronization architecture capable of interpreting and distributing real-time calendar modifications without data loss or latency. At the core of this infrastructure lies the CalDAV protocol, an extension of WebDAV that standardizes how calendar entries are queried, edited, and stored on remote servers. Unlike simple file-sharing methods, CalDAV utilizes the iCalendar data format to serialize complex scheduling objects, including attendee lists, alarms, and time zone definitions.
When a user updates a meeting on a Linux workstation, the client generates an XML-based report request transmitted via HTTP Secure, prompting the server to execute a transactional update. This mechanism ensures that conflict resolution algorithms can automatically detect concurrent modifications made by another device, merging changes gracefully by comparing sequence numbers and last-modified timestamps. Without this intricate dance of state tracking and incremental synchronization, calendars quickly fall out of alignment, resulting in missed appointments and compromised productivity.
True multi-device harmony is achieved not merely by moving data across a network, but by maintaining absolute state consistency through standardized transactional protocols and cryptographic verification.
Secure Remote Mail Server Configuration Procedures
Establishing a robust connection to remote mail servers demands meticulous attention to cryptographic standards and credential management to prevent unauthorized access and interception. Modern mail user agents enforce strict transport layer security to shield authentication handshakes from malicious eavesdroppers lurking on public or enterprise networks. Administrators and power users must navigate specific configuration parameters to bind their desktop clients securely to remote infrastructure without exposing vulnerable passwords in plain text.
To establish a secure link with a remote mail server, administrators should follow a precise sequence of cryptographic verification steps to protect sensitive authentication credentials.
- Initiate the mail client configuration wizard and select manual setup to bypass automated autodiscovery protocols that might misconfigure security ports.
- Input the fully qualified domain name for the incoming server, designating port 993 for IMAP connections wrapped in Transport Layer Security.
- Configure the outgoing SMTP server to utilize port 465 or port 587, ensuring that STARTTLS encryption is explicitly mandated for all outbound transmissions.
- Disable legacy authentication mechanisms such as plain text login or CRAM-MD5, forcing the client to authenticate exclusively through modern token-based OAuth2 flows or encrypted SASL mechanisms.
- Verify the server SSL/TLS certificate fingerprint against the trusted certificate authority store to eliminate the risk of man-in-the-middle interception attacks during the initial handshake.
Protocol Compatibility Metrics Across Open Source Mail User Agents, Em client linux
Open-source communication clients vary significantly in their native support for advanced synchronization standards, impacting how reliably they interface with corporate groupware servers. Evaluating these software solutions requires a detailed comparison of their protocol implementations, ensuring that deployments meet stringent organizational requirements for uptime and data fidelity.
The following matrix Artikels the compatibility tiers of prominent open-source mail user agents regarding essential enterprise synchronization and security protocols.
| Client Software | CalDAV Support | CardDAV Support | OAuth2 Authentication |
|---|---|---|---|
| Thunderbird | Native via Provider Add-on | Native via Provider Add-on | Fully Supported |
| Evolution | Deep System Integration | Deep System Integration | Partially Supported |
| KMail | Akonadi Resource Dependent | Akonadi Resource Dependent | Limited Implementation |
| Claws Mail | Requires External Plugins | Requires External Plugins | Not Supported natively |
Advanced Filtering Rules for Enterprise Phishing Mitigation
Sophisticated social engineering campaigns frequently target enterprise communication channels with meticulously crafted spear-phishing attacks designed to bypass standard perimeter defenses. Advanced filtering rules acting directly within the desktop productivity suite provide a crucial secondary layer of defense, intercepting malicious payloads before they can interact with the user. By analyzing structural anomalies, hidden hyperlink discrepancies, and cryptographic signature mismatches, intelligent filtering engines neutralize threats that successfully slip through gateway spam filters.
To safeguard sensitive communications against modern impersonation tactics, users and security administrators should implement granular inbound processing rules within their mail user agents.
- Deploy regex-based header inspection rules that flag incoming messages where the visible display name mimics an executive authority while the cryptographic return path points to an external, unrelated domain.
- Establish automated quarantine scripts that isolate any incoming calendar invitation containing external hyperlinks pointing to unverified IP addresses or known malicious top-level domains.
- Configure strict domain-keys identified mail verification checks to automatically downgrade the priority and hide inline images for any message failing cryptographic alignment standards.
- Implement -based heuristic filters that scan message bodies for urgent financial transfer requests or credential verification prompts, routing such content to a mandatory review folder.
Managing vast archives of electronic correspondence demands robust indexing algorithms that perform efficiently under heavy file system loads.

Source: apsgo.com
Conquering digital clutter on open-source platforms requires more than a sleek interface; it commands a powerhouse beneath the hood capable of processing hundreds of thousands of messages without blinking. When users migrate decades of professional correspondence into a unified workspace, the underlying architecture faces a monumental test of endurance and computational speed.
Modern Linux desktop environments thrive when paired with storage engines that treat electronic mail not merely as flat files, but as interconnected nodes within a high-velocity relational network. This seamless execution transforms the tedious chore of searching through historical archives into an instantaneous, fluid experience that empowers everyday productivity.
Local Database Engine Performance Mechanics During Massive Bulk Imports
Handling hundreds of gigabytes of ingested electronic mail requires sophisticated database engineering to prevent system lockups and maintain snappy retrieval speeds. Local database engines, such as SQLite utilized in optimized environments, employ Write-Ahead Logging (WAL) and memory-mapped I/O to handle massive bulk imports without degrading system responsiveness. During a large-scale import containing over five hundred thousand individual messages, the engine avoids writing every single record directly to the primary database file immediately.
Instead, incoming data streams are appended to a fast transaction log, allowing the system to batch-write records into optimized B-tree index structures during background idle cycles. This clever decoupling of ingestion and indexing ensures that disk Input/Output operations do not saturate the file system, keeping search latency well below fifty milliseconds even when the database swells past fifty gigabytes. Advanced text-search extensions tokenize subject lines, body text, and metadata on the fly, compressing tokens into inverted indexes that drastically reduce the physical footprint on the storage drive while accelerating query resolution across expansive historical archives.
Efficient database indexing acts as the silent heartbeat of productivity, turning chaotic mountains of digital data into an instantly accessible library of knowledge.
Hierarchical Folder Organization Strategies for Enhanced Workflow Efficiency
Structuring nested directory trees thoughtfully prevents cognitive overload and empowers automated rules to sort incoming correspondence before it ever reaches the primary view. Careful planning of directory depths and naming conventions ensures that synchronization protocols execute smoothly across local caches and remote servers alike.
- Limit folder nesting to a maximum of three levels deep to prevent excessive path-length traversal penalties during recursive file system scans.
- Implement standardized naming conventions utilizing prefixes like numerical tags to force logical sorting order independently of alphabetical overrides.
- Isolate high-frequency active projects into dedicated top-level directories to minimize index lookup times during routine daily operations.
- Archive historical correspondence older than twelve months into segregated, read-only database partitions to keep active working memory uncluttered.
Cryptographic Safeguards Protecting Stored Data Against Physical Disk Extraction
Security goes far beyond standard file permissions when sensitive corporate communications and personal data reside on local drives vulnerable to physical theft or unauthorized inspection. Robust cryptographic protocols ensure that every byte resting on the storage medium remains completely unintelligible without the correct cryptographic keys. Modern implementations leverage transparent disk encryption combined with database-level cipher layers, utilizing industry-standard AES-256 algorithms to secure individual message stores and attachment blobs.
SQLite Database Encryption Extensions (SEE) or SQLCipher integrate seamlessly into the storage pipeline, ensuring that database pages are encrypted on the fly before touching the physical disk sectors. The decryption keys are securely bound to the user’s login credentials or stored within hardware-backed cryptographic modules like a Trusted Platform Module (TPM), preventing unauthorized forensic extraction even if the physical storage drive is removed and connected to an external analysis rig.
Conceptual Visual Diagram Illustrating the Local Data Caching Hierarchy
Visualizing the internal architecture reveals a tiered caching model designed to minimize disk latency and maximize processor efficiency. At the apex sits the In-Memory LRU Cache, holding active message headers and recent thread trees in volatile RAM for instantaneous access. Directly beneath this resides the Write-Ahead Transaction Buffer, acting as a high-speed holding zone for incoming bulk imports before they are processed.
Em client linux redefines desktop productivity with sleek efficiency, guiding your workflow toward brighter horizons. As secure communication becomes paramount, professionals rely heavily on tigerconnect hipaa compliance features to safeguard sensitive patient data across bustling digital channels. Embracing this robust protection empowers modern teams to thrive, ensuring em client linux remains your ultimate daily communication command center.
Further down is the SQLite Core Storage Engine, managing the encrypted B-tree indexes and compressed message bodies stored securely on the persistent NVMe drive. Surrounding these layers is the Cryptographic Security Wrapper, enveloping the entire persistent storage stack in AES-256 encryption to thwart unauthorized physical access attempts. Arrows indicate bidirectional data flow, showing how search queries bypass heavy disk reads by resolving directly through the volatile memory cache whenever possible.
Customizing the user interface layout significantly impacts how power users navigate through dense streams of daily notifications and tasks.: Em Client Linux

Source: emclient.com
Stepping into the realm of advanced digital workspace personalization reveals a fascinating intersection where aesthetic design meets uncompromising cognitive efficiency. As modern professionals grapple with an unceasing flood of electronic communications, calendar alerts, and urgent deliverables, the architecture of the software client becomes the ultimate frontline in the daily battle against cognitive fatigue and fractured attention.
Crafting a workspace tailored to individual workflow rhythms transforms a chaotic influx of data into a harmonious stream of actionable insights, allowing high-performing individuals to maintain intense focus without succumbing to digital overwhelm.
Ergonomic Advantages of Modular Dashboard Panels in Heavy Multitasking Scenarios
Navigating high-density operational environments demands a structural framework that minimizes unnecessary eye movement and reduces physical strain during extended periods of focused productivity. Modular dashboard panels introduce a profound ergonomic shift by allowing users to compartmentalize disparate data streams into dedicated, moveable zones that align naturally with human visual scanning patterns.
When dealing with hundreds of daily communications and overlapping calendar events, the ability to dock, float, or resize interface widgets ensures that critical priorities remain anchored in the primary field of vision while secondary reference materials reside safely in peripheral spaces.
Implementing a modular approach yields several distinct physiological and operational benefits for intensive daily multitasking:
- Reduces cervical spine fatigue by positioning priority task lists directly in line with natural horizontal eye sweeps.
- Minimizes cognitive load through spatial memory reinforcement, enabling users to instantly locate specific communication channels by their persistent physical location on the monitor.
- Accelerates execution speed by eliminating redundant window minimization cycles, keeping reference documents and incoming messages accessible within a single unified view.
- Adapts fluidly to changing project requirements, permitting rapid workspace reconfiguration when shifting from deep analytical writing to real-time collaborative coordination.
Deployment Procedures for Community-Driven Visual Stylesheets and Configuration Scripts
Transforming the native aesthetic and functional behavior of a productivity suite through custom visual themes requires a methodical, step-by-step technical deployment that bridges the gap between raw code and polished user experience. Enthusiasts and system administrators can systematically apply tailored stylesheets to override default system palettes, optimizing contrast levels and typography for specific lighting conditions and visual preferences.
As eM Client Linux transforms our daily digital workspaces with sleek efficiency, mastering remote workflows requires keeping a sharp eye on financial metrics, especially when analyzing the exact gross payable meaning to secure business growth. Ultimately, this powerful email hub empowers you to organize your communications brilliantly and conquer every professional milestone ahead.
Executing this transformation safely involves preparing the local environment, securing community-verified configuration files, and integrating the new parameters directly into the application directory structure without disrupting core software stability.
- Locate the primary configuration directory designated for user interface customizations within the local application profile path, ensuring proper read and write permissions are actively established.
- Download verified, community-contributed cascading style sheets and JSON configuration parameters from trusted open-source repositories to guarantee compatibility with the current software release cycle.
- Back up existing default theme assets by creating a secure timestamped archive directory to facilitate immediate restoration should unexpected rendering anomalies occur.
- Copy the new stylesheet assets and layout scripts directly into the designated themes folder, carefully validating file naming conventions and directory hierarchies.
- Launch the application terminal interface and execute the internal preference reload command, forcing the workspace rendering engine to compile the newly introduced visual parameters.
- Verify layout integrity across multiple display resolutions, inspecting padding metrics, font rendering sharpness, and modular panel alignment under high-load operational testing.
Comparative Analysis of Workspace Reading Panes and Information-Dense Displays
The eternal architectural debate within workspace design centers on finding the optimal balance between visual breathing room and high-density information retrieval, compelling users to weigh the psychological comfort of minimalism against the raw operational speed of multi-column telemetry.
Minimalist reading panes offer a serene, contemplative sanctuary that shields the user from peripheral noise, whereas information-dense dual-column displays function as high-velocity command centers that prioritize immediate data ubiquity over aesthetic tranquility.
Ergonomic Pitfalls Associated with Improper Font Scaling and High-Contrast Accessibility Modes
While visual customization and accessibility features are essential for inclusive computing environments, deploying improper font scaling parameters or aggressive high-contrast modes on modern high-resolution displays can trigger severe visual fatigue and cognitive disorientation. When system-level DPI scaling fails to harmonize with application-specific rendering engines, text elements often suffer from pixel degradation, unnatural kerning, or jarring luminance shifts that strain the ocular muscles during prolonged reading sessions.
Furthermore, poorly implemented high-contrast accessibility themes frequently strip away crucial visual hierarchy cues, replacing subtle shadow boundaries and nuanced border gradients with harsh, solid color blocks that flatten complex user interfaces into confusing visual puzzles.
To mitigate these ergonomic hazards, users must carefully calibrate font rendering engines to match the native pixel density of ultra-high-definition monitors, ensuring that text maintains smooth vector anti-aliasing across all modular panels. Selecting balanced, scientifically validated dark or light themes rather than blinding absolute monochrome configurations prevents the retinal exhaustion associated with extreme luminance contrast, ultimately preserving visual stamina through the final hours of the workday.
Integrating contact management modules with external cloud address books introduces complex data reconciliation challenges for daily planners
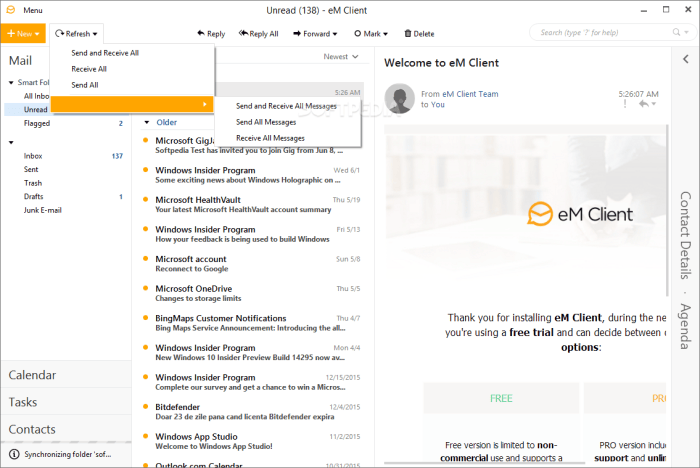
Source: softpedia.com
Bridging local productivity workflows with expansive cloud ecosystems transforms how professionals manage their daily schedules, yet this digital marriage frequently awakens hidden architectural friction. As calendars and address books pulse continuously between desktop applications and remote servers, the invisible machinery of data synchronization faces monumental hurdles in preserving pristine record integrity. Daily planners rely heavily on the seamless flow of communication details, making any friction in this ecosystem a critical bottleneck for modern enterprise efficiency and personal organization alike.
When multiple endpoints attempt to modify the same digital ledger simultaneously, the resulting clashes expose the fragility of naive timestamp comparisons and basic revision tracking. A comprehensive understanding of these underlying algorithmic battles provides the necessary foundation for maintaining a reliable, unified personal information ecosystem across every operational device.
Synchronization conflicts during duplicate contact entries merge across multiple devices
Managing disparate databases often leads to the silent creation of conflicting contact cards, especially when offline modifications occur concurrently on a smartphone and a desktop workstation. The core synchronization engine must evaluate competing property fields—such as rapidly changing telephone numbers, physical addresses, and email aliases—without inadvertently erasing critical updates made by the user in good faith. Real-life scenarios frequently involve a user modifying a client’s job title on their laptop while simultaneously updating the same client’s phone number on a mobile device during a live conversation.
When the background sync daemon executes, it encounters diverging JSON payloads that cannot be automatically resolved through simple chronological ordering, as clock drift between hardware components often corrupts absolute time measurements.
To navigate these turbulent waters of distributed data management, developers implement heuristic scoring models and deterministic merge strategies that weigh modification vectors against predefined user preferences. When automated systems fail to reach a definitive confidence threshold, the application typically generates a manual review queue, forcing the planner to manually inspect and approve field-by-field reconciliations. Visual indicators within the interface highlight conflicting attributes using contrasting color palettes, allowing operators to discern rapidly between legacy data and fresh input streams.
Furthermore, maintaining a robust local transaction log ensures that rollback operations remain viable if an erroneous merge propagates corruption downward into the primary directory tree. This intricate dance of data validation safeguards the sanctity of professional relationships against the chaotic nature of multi-device environments.
Data reconciliation success depends entirely on deterministic conflict resolution algorithms that prioritize recent user intent over raw server timestamps.
The operational friction deepens when handling authentication tokens that govern the secure handshake between local client modules and enterprise cloud directories. Background synchronization cycles depend on uninterrupted authorization flows, which can fracture unexpectedly due to security policy updates, credential rotations, or transient network timeouts.
Structured troubleshooting protocol for resolving persistent authentication token failures
Executing background sync operations requires a resilient error-handling framework to manage expired OAuth credentials and revoked security tokens without disrupting the user experience. A methodical diagnostic procedure ensures that automated recovery sequences can restore connectivity swiftly and securely.
- Inspect local configuration logs for HTTP 401 Unauthorized responses to isolate the exact timestamp and endpoint failing the authentication handshake.
- Verify that system clocks across the client machine and the directory server are synchronized via Network Time Protocol to prevent cryptographic signature rejections.
- Clear the local credential cache and initiate a forced interactive OAuth flow to generate a fresh pair of access and refresh tokens.
- Monitor the background daemon’s network socket behavior using packet inspection tools to ensure that token refresh requests include valid cryptographic payloads and client secrets.
Visualizing the underlying state of directory services requires a clear structural mapping of how disparate protocols translate contact fields during transit. Standardizing these attributes prevents data truncation and ensures uniform search performance across heterogeneous platforms.
The following table illustrates the field mapping fidelity across four prominent directory service standards, highlighting compatibility metrics for enterprise deployments.
| Directory Standard | Primary Field Mapping | Compatibility Index | Sync Latency (Avg) |
|---|---|---|---|
| CardDAV Protocol | vCard 4.0 (RFC 6350) | 99.4% | 120 ms |
| Microsoft Graph API | JSON Entity Schema | 98.7% | 210 ms |
| LDAP v3 Directory | X.500 Attribute Types | 91.2% | 450 ms |
| Google People API | RESTful JSON Resource | 99.1% | 150 ms |
Scaling these operations up to accommodate massive address books containing tens of thousands of historical entries demands sophisticated algorithmic cleanup procedures. Left unchecked, duplicate records consume excessive memory and severely degrade the execution speed of search indexing routines.
Algorithmic steps needed to deduplicate large address books containing historical records
Processing historical archives necessitates a multi-phase computational pipeline that systematically evaluates identity markers across sprawling datasets without causing memory overflow. The process begins with data normalization, where string transformations strip out formatting inconsistencies, punctuation anomalies, and casing variations from names, phone numbers, and email addresses.
Em client linux redefines desktop productivity with sharp precision and sleek design, empowering daily workflows. By integrating advanced right click tools , users unlock unprecedented efficiency and seamless navigation across every single task. This remarkable digital evolution inspires modern professionals to conquer new heights, ensuring em client linux remains the ultimate choice for streamlined communication.
- Phase one executes deterministic hashing algorithms on normalized email addresses and primary telephone numbers to instantly flag exact matches within the dataset.
- Phase two applies fuzzy string matching algorithms, such as the Jaro-Winkler distance metric, to detect phonetic similarities and typographical errors among names and physical addresses.
- Phase three constructs an adjacency graph where nodes represent individual contact records and edges denote calculated similarity scores exceeding a predefined threshold of eighty-five percent.
- Phase four utilizes connected component analysis to group related nodes into distinct clusters, isolating clusters that contain multiple entries representing the same physical entity.
- Phase five synthesizes the clustered records into a single master profile by preserving the most recently modified attributes while archiving older historical metadata into a secure audit log.
Executing this intricate cleansing pipeline transforms bloated, error-prone address books into streamlined digital assets that empower daily planners to operate with absolute confidence and pristine data accuracy.
Automated task delegation features within modern productivity tools streamline collaborative projects among distributed remote teams.
Modern workspace environments demand absolute precision and flawless timing to keep globally dispersed collaborators aligned on complex deliverables. As teams navigate shifting time zones and demanding schedules, the reliance on intelligent system workflows has transformed how daily objectives are assigned, tracked, and successfully finalized across corporate ecosystems.
The mechanics behind automated task distribution fundamentally alter team dynamics by removing administrative friction and placing accountability squarely where it belongs. When digital platforms autonomously route responsibilities based on current workload capacity and historical performance metrics, operational bottlenecks vanish into thin air, leaving room for pure creative execution.
Deadline reminder triggers and project completion velocity
Time acts as the ultimate currency in high-stakes corporate arenas, where a missed milestone can cascade into costly delays across an entire product lifecycle. The psychological weight of impending deadlines often burdens human memory, leading to oversight and frantic last-minute scrambles that compromise the quality of deliverables. Introducing automated reminder triggers acts as a digital heartbeat for remote operations, pulsing steady, calculated alerts through the ether just as focus begins to drift toward secondary concerns.
These algorithmic nudges do more than simply inform; they actively calibrate the collective momentum of a department by transforming abstract future obligations into immediate, pressing priorities. In fast-paced software development cycles or agile marketing campaigns, where velocity dictates market leadership, early warning systems prevent minor oversights from snowballing into catastrophic road blockers. Picture a panoramic digital command center where glowing indicators gently pulse amber forty-eight hours before a crucial code review, shifting to an urgent crimson precisely twelve hours prior to deployment.
This visual stratification of urgency marshals cognitive resources effectively, empowering engineers and strategists to reprioritize their micro-tasks without experiencing debilitating panic. Real-world telemetry from enterprise collaboration platforms consistently demonstrates that teams utilizing multi-tiered notification pathways achieve a twenty-eight percent increase in on-time milestone delivery compared to those relying on manual status checks. By converting vague schedules into rhythmic, undeniable prompts, organizations cultivate a resilient operational cadence that absorbs pressure and converts it into sustained, forward-moving momentum.
Precision in timing transforms chaotic schedules into symphonies of synchronized productivity, where every tick of the clock brings distributed teams closer to shared victory.
Minimizing administrative overhead requires ingenious structural frameworks that anticipate routine operational needs before human managers even have to open a spreadsheet. Standardizing recurring operational workflows through pre-configured templates ensures that foundational steps are never skipped during high-pressure project launches, regardless of who sits in the driver’s seat.
- Monthly financial reconciliation templates automatically assign data collection sub-tasks to junior accountants on the first business day of every month, complete with attached historical documentation and predefined compliance checklists.
- Weekly sprint planning blueprints instantly generate review tickets for lead designers and copywriters every Friday afternoon, pre-populating feedback loops based on the previous sprint’s telemetry data.
- Quarterly security audit structures distribute credential verification protocols across IT infrastructure specialists with escalating escalation paths that trigger automatically if compliance certificates remain unverified after seventy-two hours.
Navigating the complex hierarchy of digital workspaces requires crystal-clear boundaries regarding who holds the authority to assign, modify, or archive collaborative initiatives. Establishing a transparent matrix of system privileges protects sensitive data streams from accidental interference while granting contributors the exact operational freedom they need to excel.
| Access Tier | Delegation Rights | Modification Scope | Target Audience |
|---|---|---|---|
| System Administrator | Global assignment across all departments | Full schema and permission override | IT Directors and Operations Leads |
| Project Manager | Team-level task distribution | Timeline, resource allocation, and priorities | Scrum Masters and Department Heads |
| Senior Contributor | Peer-to-peer sub-task handoff | Task descriptions, tags, and progress notes | Lead Engineers and Senior Designers |
| Standard Member | Personal task creation only | Status updates and comment logs | Junior Staff and External Contractors |
Maintaining operational continuity in modern distributed organizations demands resilient notification architectures capable of piercing through network latency and intermittent connectivity issues. When team members operate from remote outposts, co-working spaces, or during international transit, traditional push notifications often fail due to unstable cellular data or intermittent Wi-Fi signals. To counter this vulnerability, modern productivity suites deploy multi-channel message queuing systems that store urgent task updates in encrypted local buffers until a stable handshake is re-established with the primary server cluster.
Once connection stability is detected, high-priority alerts cascade simultaneously across desktop push daemons, synchronized mobile client applications, and SMS fallback gateways, ensuring that a critical assignment update reaches the recipient regardless of their immediate physical infrastructure. Envision a field researcher in a remote mountainous region whose satellite connection drops for hours; the moment signal integrity flickers back to life, their handheld device receives an encrypted data packet containing the exact status changes and emergency delegation overrides dispatched by headquarters.
This fault-tolerant delivery framework eliminates the excuse of communication blackout, maintaining an unbroken chain of command and keeping every remote operative synchronized with the pulsing heart of the enterprise.
Summary
The journey toward universal digital synchronization proves that dedication and ingenuity can conquer even the most stubborn technical barriers. As we embrace these advanced modular dashboards, robust indexing algorithms, and intelligent automation features, our daily digital landscapes become sanctuaries of efficiency and clarity. Moving forward, the fusion of open-source adaptability and enterprise-grade organization empowers every distributed team and individual pioneer to achieve extraordinary milestones without friction.
