g2 reviews secureframe drata vanta sprinto isms.online risk ledger archer stand as monumental pillars shaping how modern enterprises navigate the treacherous waters of digital trust and regulatory compliance. Beneath the polished dashboards and glowing peer ratings lies a fascinating psychological drive, where overwhelmed buyers seek solace in collective validation before entrusting their security postures to automated guardians. Historically, software procurement has evolved from static vendor brochures into dynamic, crowd-sourced digital marketplaces where a single user’s feedback can alter the trajectory of a multi-million-dollar security suite.
Yet, relying solely on aggregate scores presents a dangerous illusion of perfection, often masking the intricate mechanical realities required to achieve true SOC 2 or ISO 27001 readiness.
As organizations transition away from fragile, manual spreadsheets into automated continuous monitoring ecosystems, understanding the operational friction points becomes paramount for survival. Whether contrasting nimble cloud-native specialists against monolithic enterprise risk suites, or dissecting how agent-based telemetry differs from API-driven log aggregation, the journey toward unbreakable security demands rigorous technical foresight. Every pull request intercepted by automated policy orchestration, and every vendor risk tier meticulously scored, represents a vital step forward.
This comprehensive exploration strips away the marketing gloss to reveal the true cost, mechanics, and transformative power of modern compliance automation in an increasingly interconnected and vulnerable digital landscape.
Navigating aggregator platforms reveals how trust and compliance automation tools shape modern security posture.

Source: cbinsights.com
Modern enterprises navigating the complex terrain of regulatory compliance often find themselves standing at a crossroads of uncertainty, staring down the barrel of grueling audits like SOC 2 and ISO 27001. As the digital perimeter expands and threat landscapes shift dynamically, security leaders no longer rely solely on glossy vendor brochures or traditional sales pitches to make mission-critical software purchasing decisions.
Instead, a profound behavioral shift has occurred across the corporate landscape, pushing buyers directly into the digital town squares of peer review aggregators. These platforms have evolved from simple digital bulletin boards into powerful arbiters of enterprise trust, fundamentally altering how organizations evaluate, select, and deploy continuous compliance automation solutions.
The relentless pursuit of validation in high-stakes enterprise software procurement is deeply rooted in cognitive psychology and behavioral economics. When Chief Information Security Officers and compliance directors face the daunting task of selecting platforms that manage sensitive organizational data, they confront severe information asymmetry. Vendors naturally present their tools in the most favorable light, highlighting flawless capabilities while obscuring implementation friction.
To mitigate the paralyzing fear of making a catastrophic purchasing mistake—an error that could result in devastating data breaches or failed audits—buyers experience an acute need for social proof and risk reduction. Peer review aggregates function as modern digital safety nets, offering collective reassurance through the lived experiences of industry peers who have already walked the treacherous compliance path. This psychological reliance on crowd-sourced intelligence satisfies the fundamental human desire for consensus, transforming isolated decision-making into a collective validation exercise.
Buyers seek comfort in numbers, viewing high aggregate scores and detailed user narratives as tangible evidence of operational reliability, thereby easing the cognitive load associated with evaluating complex, technical compliance ecosystems.
Historical evolution of software evaluation sites
The journey from rudimentary software directory listings to sophisticated, data-driven review ecosystems mirrors the broader maturation of the software-as-a-service economy. Decades ago, enterprise software acquisition was dictated by rigid analyst quadrants, vendor-hosted user conferences, and opaque procurement cycles that heavily favored incumbent giants with massive marketing budgets. As the software market democratized and cloud-native solutions proliferated, a massive transparency gap emerged, leaving mid-market and enterprise buyers starved for unbiased, grassroots feedback.
The advent of modern peer review platforms shattered the traditional gatekeeping model by empowering actual end-users to publicly rate and critique software functionality, customer support, and implementation velocity. This democratization of feedback transformed enterprise security software procurement from a closed-door negotiation into a vibrant, peer-informed marketplace. Decision-makers suddenly gained access to granular, unfiltered insights regarding how platforms perform in real-world production environments, shifting the balance of power decisively back to the buyers.
The transformation of enterprise procurement through user-generated intelligence is vividly illustrated by the operational shift within modern security teams. When evaluating compliance automation infrastructure, procurement committees now routinely audit historical rating trends, reviewer job titles, and specific critique threads alongside traditional technical specifications.
- Enterprise buyers cross-reference feature claims against verified user feedback to identify recurring implementation bottlenecks and hidden deployment costs.
- Organizations analyze reviewer sentiment trends over time to determine whether a software vendor is actively improving its product or neglecting core infrastructure.
- Procurement leads leverage detailed peer narratives to construct targeted vendor demonstration scripts, focusing directly on real-world pain points highlighted by past users.
Collective peer intelligence serves as the ultimate diagnostic lens, exposing the stark contrast between marketing promises and operational reality in compliance automation.
As G2 reviews highlight Secureframe, Drata, Vanta, Sprinto, ISMS.online, Risk Ledger, and Archer for mastering compliance, modern enterprises are discovering that streamlining agreements through robust contract negotiation software unlocks unprecedented operational velocity. Harnessing these breakthroughs transforms complex regulatory hurdles into stepping stones for unstoppable growth, cementing the vital role of Secureframe, Drata, Vanta, Sprinto, ISMS.online, Risk Ledger, and Archer in future success.
To fully grasp how modern software evaluation sites operate as dynamic barometers of industry standards, one must visualize a high-tech corporate observatory during a critical evaluation cycle. Imagine a sleek, minimalist executive boardroom bathed in the soft glow of multiple widescreen monitors, where a security operations team is actively auditing compliance software profiles. On the primary screen, a sprawling digital heatmap glows with real-time sentiment metrics, mapping out user satisfaction curves across various industries such as fintech, healthcare, and SaaS.
Surrounding this central display are cascading data streams featuring verified buyer testimonials, categorized by company size, deployment timeline, and specific framework requirements like SOC 2 Type II or ISO 27001. Detailed graphical breakdowns illustrate the correlation between customer support responsiveness and high retention rates, while interactive comparison matrices highlight the friction points of migrating between different compliance automation platforms. This vivid digital ecosystem captures the relentless pulse of the cybersecurity market, where every review acts as a vital data point shaping the future posture of enterprise defense.
Limitations inherent in relying solely on aggregate ratings
While peer review aggregates provide invaluable initial guidance, treating a high aggregate score as an absolute guarantee of success introduces significant blind spots into the software selection process. Compliance frameworks are deeply nuanced, and an automation platform that excels in streamlining a standardized SaaS startup’s security policies may utterly fail to accommodate the intricate legacy infrastructure of a heavily regulated global financial institution.
Aggregate ratings often flatten complex operational realities into a single, homogenized number, masking critical context about an organization’s specific technical maturity, internal resource availability, and unique risk appetite. Relying exclusively on these high-level metrics without conducting rigorous, contextual due diligence can lead to mismatched tool adoption, prolonged deployment cycles, and severe audit friction.
Navigating the pitfalls of surface-level metrics requires a disciplined approach to vendor vetting that looks far beyond numerical scores.
As modern G2 reviews highlight Secureframe, Drata, Vanta, Sprinto, ISMS.online, Risk Ledger, and Archer for reshaping compliance, curious minds are exploring what is the industry of passwerk.be to uncover unique market niches. Ultimately, mastering these dynamic compliance platforms empowers ambitious organizations to scale securely and triumph globally.
| Evaluation Dimension | Aggregate Platform View | Operational Reality Check |
|---|---|---|
| Implementation Speed | Averages indicate rapid onboarding in weeks. | Actual deployment depends heavily on internal data cleanliness and team bandwidth. |
| Framework Coverage | Broad checklists show support for ISO and SOC 2. | Depth of evidence collection varies wildly across complex cloud environments. |
| Customer Support Quality | High satisfaction ratings reflect general responsiveness. | Specialized technical guidance during critical audit phases may require enterprise-tier contracts. |
Organizations must complement aggregate data with direct proof-of-concept testing, reference calls with peers operating in identical regulatory environments, and deep architectural assessments. Recognizing that no single rating can capture the unique DNA of an enterprise security program ensures that the chosen compliance automation platform acts as a genuine force multiplier rather than a rigid, ill-fitting constraint.
Evaluating automated compliance ecosystems requires contrasting continuous monitoring specialists against enterprise governance suites.
Modern security operations demand a fundamental shift in how organizations approach risk and regulatory alignment. As digital infrastructures expand across multi-cloud environments, the friction between speed and stringent control frameworks dictates market survival.
Navigating this landscape forces security leaders to look beyond basic checklist validation and examine the underlying machinery powering modern compliance frameworks. The architecture chosen directly dictates both operational agility and audit resilience.
Operational Architectures of Cloud-Native Trust Platforms Versus Legacy Risk Management Monoliths
Cloud-native compliance ecosystems are built on API-driven architectures designed to ingest telemetry data in real-time. This continuous automated observation contrasts sharply with legacy risk management monoliths that rely on periodic manual sampling and heavy on-premise databases. The efficiency gap manifests clearly in resource allocation, where agile platforms reduce engineering overhead by automating evidence collection across thousands of infrastructure nodes.
Legacy systems often require extensive custom scripting and manual data mapping, which introduces human error and latency into the audit cycle. Conversely, modern trust platforms leverage pre-built integrations with identity providers, cloud service providers, and code repositories to maintain a living posture state. Organizations transitioning from older architectures routinely report a dramatic compression of audit preparation timelines, moving from months of frantic document gathering to continuous readiness.
Continuous compliance automation transforms security from a reactive annual event into an embedded, real-time operational discipline that reduces overall risk exposure.
To fully understand the divergence in market solutions, comparing core architectural metrics clarifies which tool fits specific organizational maturities. The following structured breakdown contrasts the operational realities of modern specialists against traditional enterprise suites.
| Deployment Speed | Pricing Models | Evidence Collection Capabilities | Target Organization Sizes |
|---|---|---|---|
| Days to weeks via automated API integrations | Subscription-based per-framework or flat-rate tiered | Automated, continuous API polling across cloud assets | Mid-market to high-growth tech enterprises |
| Months to over a year requiring professional services | High upfront licensing with per-module and user fees | Semi-automated with heavy reliance on manual document uploads | Large global enterprises and highly regulated monoliths |
Onboarding Friction Points During the Transition from Manual Spreadsheets to Automated Readiness Frameworks
Shifting away from static spreadsheets and ad-hoc communication channels exposes deeply ingrained organizational habits that can stall digital transformation initiatives. Mid-market firms frequently encounter cultural resistance as engineering and compliance teams grapple with newfound transparency. Automated frameworks abruptly highlight misconfigurations that previously remained hidden within fragmented documentation silos, creating immediate remediation backlogs.
Data normalization represents another substantial hurdle during initial setup, as disparate asset inventories must be reconciled into a single source of truth for the platform to ingest accurately. Furthermore, aligning internal stakeholders on control ownership requires dedicated cross-functional coordination. Without clear executive sponsorship, teams often default to familiar manual workarounds rather than trusting the automated continuous monitoring loops.
- Cultural resistance driven by the sudden exposure of hidden infrastructure misconfigurations and security gaps.
- Data normalization complexities when consolidating fragmented asset inventories from legacy systems into automated ingest pipelines.
- Resource constraints in assigning clear internal ownership for newly automated controls across engineering and legal departments.
Visualizing the onboarding landscape reveals a vivid contrast between chaotic manual workflows and streamlined digital control rooms. Picture a dimly lit office where compliance officers are buried under towers of binder clips and color-coded spreadsheets, frantically cross-referencing policy documents against outdated server logs. In sharp contrast, the modern transition environment resembles a bright, high-tech command center where interactive dashboards pulse with real-time green indicators, cleanly mapping cloud resources to SOC 2 or ISO 27001 requirements with a single click.
Operationalizing framework readiness demands a granular understanding of how evidence gathering occurs across disparate cloud environments.: G2 Reviews Secureframe Drata Vanta Sprinto Isms.online Risk Ledger Archer
Source: beaglesecurity.com
Modern compliance engineering relies heavily on the uninterrupted capture of infrastructural truth. As organizations distribute workloads across heterogeneous cloud providers, the mechanisms responsible for translating raw telemetry into defensible audit evidence become the bedrock of an effective security posture.
Mechanical differences between agent-based telemetry collection and API-driven log aggregation for continuous compliance monitoring
Achieving structural visibility across complex, multi-tenant infrastructures requires choosing the right ingestion paradigm. Agent-based telemetry collection relies on lightweight software daemons deployed directly onto virtual machines, containers, and host operating systems. These local agents continuously observe kernel-level system calls, file integrity changes, and local configuration files, streaming granular metrics directly back to the compliance platform. This approach excels in capturing deep behavioral insights, process executions, and internal memory states that external monitors simply cannot reach.
Conversely, API-driven log aggregation bypasses the need for local endpoint installations by querying cloud provider control planes natively. Utilizing mechanisms such as AWS CloudTrail, Google Cloud Audit Logs, and Azure Activity Logs, API collectors poll or stream resource modifications, IAM policy updates, and network perimeter changes directly from the provider infrastructure. While agent-based collection provides unmatched depth at the host layer, API aggregation delivers frictionless breadth across serverless functions, managed databases, and object storage tiers without risking host performance degradation.
Practical methodologies for mapping multi-cloud assets directly to security controls without triggering alert fatigue among engineering teams
Engineering velocity often suffers when compliance monitoring introduces a barrage of false positives and redundant security notifications. To maintain high developer morale while satisfying stringent SOC 2, ISO 27001, or HIPAA frameworks, security architects must implement systematic asset tagging and dynamic control inheritance models. Establishing a unified tagging taxonomy across AWS, Azure, and GCP allows automated platforms to immediately contextualize workload ownership, environment sensitivity, and compliance scope upon provisioning.
Organizations must adopt risk-weighted ingestion pipelines that suppress low-level informational alerts and only surface genuine control failures requiring remediation. By translating raw telemetry through codified policy-as-code engines, compliance teams ensure that notifications are actionable, context-rich, and routed directly to the appropriate service owner. The following strategies Artikel effective integration patterns for sustainable engineering workflows:
- Implement immutable resource tagging standards at the infrastructure-as-code stage to automatically assign compliance ownership.
- Deploy policy-as-code frameworks like OPA (Open Policy Agent) to evaluate configurations locally before infrastructure deployment occurs.
- Establish centralized notification thresholds that aggregate recurring minor deviations into scheduled weekly digest reports instead of immediate pages.
- Leverage automated remediation playbooks for common misconfigurations, such as correcting public S3 bucket ACLs instantly without human intervention.
Automation succeeds not when it collects every possible data point, but when it filters out the noise to present an undeniable narrative of continuous security alignment.
Detailed visual description illustrating the data flow trajectory from a cloud infrastructure event to a finalized audit-ready artifact
Visualizing the lifecycle of compliance data reveals the intricate choreography required to turn transient cloud events into permanent, cryptographically verified audit evidence. A comprehensive blueprint of this digital assembly line highlights every stage of data transformation, validation, and storage within the compliance ecosystem.
The visual representation unfolds across a panoramic canvas divided into distinct operational zones, rendered in a crisp, architectural blueprint aesthetic with dark navy backgrounds and luminous cyan data streams. On the far left, an initial cloud infrastructure event occurs: a developer modifies an identity and access management role in a distributed AWS environment, generating a raw JSON log entry within CloudTrail.
This event instantly triggers an API-driven webhook that dispatches the payload across an encrypted transport layer into the ingestion gateway of the compliance orchestration engine.
In the central processing zone, the data packet enters a normalization pipeline. Here, the platform strips proprietary cloud provider metadata, standardizes the schema, and evaluates the attribute against codified regulatory requirements such as SOC 2 CC6.1. The interface dynamically updates, displaying a glowing green validation badge that signifies successful control adherence. The telemetry record is then cryptographically hashed to ensure non-repudiation and immutability.
On the right side of the canvas, the finalized artifact flows into a secure, write-once-read-many (WORM) storage vault. A structured dashboard view emerges, showing the mapped control index, timestamped evidence trails, and an auditor-facing portal view. Subtle, pulsing vector lines connect the original infrastructure event to the final compliance report, demonstrating a seamless, unbroken chain of custody ready for instant inspection by external certification bodies.
Quantifying information security management systems implementation reveals the true cost of maintaining persistent audit readiness.

Source: brightdefense.com
Organizations embarking on the journey of information security management systems implementation often underestimate the financial gravity required to sustain continuous compliance. Beneath the surface of shiny dashboard interfaces and automated evidence collection lies a complex ecosystem of hidden expenditures, resource reallocation struggles, and tiered subscription economics that dictate the true cost of ownership.
Navigating this digital landscape requires a clear-eyed financial perspective. When security leaders peel back the layers of modern compliance automation platforms, they discover that the initial software license fee is merely the tip of a much larger budgetary iceberg.
Hidden overhead expenses associated with maintaining third-party vendor integrations and managing custom policy templates within digital vaults
Deploying compliance automation tools often introduces unforeseen maintenance costs that steadily erode initial projected savings. Organizations frequently discover that third-party cloud integrations require constant API recalibration whenever underlying cloud service providers update their security postures or telemetry endpoints. Furthermore, custom policy templates demand dedicated engineering hours to ensure they continuously align with evolving regulatory frameworks like SOC 2, ISO 27001, or HIPAA.
Enterprises often visualize this overhead as a sprawling, interconnected web of data pipelines where a single broken API token can quietly stall evidence collection across hundreds of critical cloud assets, resulting in expensive emergency remediation cycles.
The financial impact of these maintenance obligations manifests in several distinct operational drains across the enterprise architecture:
- API connector breakage requiring immediate developer intervention during routine cloud infrastructure updates.
- Version control drift between customized policy templates stored in digital vaults and the actual operational controls enforced in production environments.
- Subscription tier inflation triggered by unexpected asset growth and the addition of mandatory premium security modules.
- Specialized compliance consultant fees required to audit and validate complex, non-standard custom integration scripts.
Internal resource allocation shifts from reactive firefighting to proactive mitigation after deploying automated policy orchestration tools
Embracing intelligent compliance orchestration fundamentally transforms how internal security teams spend their working hours, shifting the organizational heartbeat from chaotic crisis response to calm, strategic oversight. Instead of engineers spending countless sleepless nights manually screenshotting AWS configurations and hunting down missing access logs before an audit window, automated systems continuously capture and map telemetry data in the background. This operational evolution frees up valuable human capital, redirecting high-paid talent toward strengthening application security, threat hunting, and architectural resilience rather than drowning in administrative compliance paperwork.
Observing this transformation feels akin to watching a frantic, manual assembly line convert into a sleek, precision-engineered automated factory floor where quality is built directly into the process. Security analysts no longer act as perpetual firefighters rushing from one compliance violation to the next. They evolve into strategic architects who design resilient systems capable of self-healing and continuous self-assessment.
Step-by-step procedure for calculating the total cost of ownership across various compliance automation subscription tiers, G2 reviews secureframe drata vanta sprinto isms.online risk ledger archer
Determining the exact financial commitment of compliance automation demands a rigorous, methodical evaluation framework that accounts for both predictable licensing costs and unpredictable internal labor expenses. Organizations must carefully analyze their unique cloud footprint, team composition, and integration complexity to project long-term expenditures accurately across different vendor pricing models.
To accurately compute the total cost of ownership, organizations should systematically execute the following analytical stages:
- Establish the baseline annual subscription fee for the targeted compliance platform tier, accounting for the total volume of connected cloud accounts and employee headcount.
- Quantify the internal labor hours spent monthly on maintaining custom integrations, fixing broken API links, and updating policy documentation within digital vaults.
- Estimate the cost of professional services or dedicated compliance personnel required to manage the platform configuration and interpret automated gap analyses.
- Calculate potential productivity gains and risk reduction savings achieved by shifting engineering hours from manual evidence collection to core product development.
- Sum the direct software costs, internal maintenance labor overhead, and integration expenses, then subtract the estimated operational savings to derive the true net total cost of ownership.
The true cost of compliance automation is never just the price on the vendor invoice; it is the calculated sum of platform licenses, integration maintenance labor, and the strategic opportunity cost of internal engineering resources.
As modern enterprises meticulously evaluate compliance platforms through g2 reviews secureframe drata vanta sprinto isms.online risk ledger archer, emerging innovations fundamentally reshape security standards. Organizations now harness tools like proctor ghost ai to brilliantly safeguard digital integrity while empowering growth. Ultimately, mastering these dynamic solutions via g2 reviews secureframe drata vanta sprinto isms.online risk ledger archer unlocks unprecedented operational resilience.
Balancing agile development velocity with stringent regulatory mandates necessitates seamless integration of security policies into developer workflows.

Source: brightdefense.com
Modern engineering organizations face a relentless tug-of-war between shipping code at lightning speed and satisfying exhaustive governance requirements mandated by frameworks like SOC 2, ISO 27001, and HIPAA. When security is treated as a late-stage gatekeeper rather than a native part of the software development lifecycle, friction mounts and deployment pipelines grind to a halt. Bridging this chasm requires embedding guardrails directly into the daily habitats of software engineers, transforming compliance from an administrative bottleneck into an automated byproduct of quality code.
Visualizing this operational shift reveals a vibrant digital ecosystem where code repositories pulse with real-time intelligence. Imagine a developer writing a feature branch in a modern integrated development environment while a subtle, glowing status indicator reflects live policy alignment. As the code takes shape, automated scanners silently map the syntax against hundreds of compliance controls, projecting a transparent window of accountability without ever breaking the developer’s creative flow.
Infrastructure drift prevention mechanisms through pull request interception
The journey toward secure agility begins at the exact moment a developer submits a pull request, turning the code review process into an automated first line of defense. Modern compliance automation platforms continuously intercept these merge requests by hooking directly into source code management systems like GitHub, GitLab, and Bitbucket. As soon as a pull request is opened, webhook listeners trigger a battery of policy-as-code evaluations that parse infrastructure-as-code files—such as Terraform scripts or Kubernetes manifests—against pre-defined compliance baselines.
These systems meticulously inspect cloud resource definitions to detect unauthorized configurations, such as unencrypted storage buckets, overly permissive security groups, or public database instances, long before any changes touch staging or production environments.
By shifting security checks far to the left, organizations eliminate the hazardous gap between infrastructure provisioning and compliance auditing. When a policy violation is detected mid-stream, the platform automatically blocks the merge button and injects precise diagnostic comments directly into the pull request interface. This immediate feedback loop educates the engineer on the spot, providing exact remediation snippets that align with regulatory mandates while keeping the velocity of the development lifecycle intact.
The infrastructure remains pristine, drift is neutralized at the source, and auditors are provided with an immutable cryptographic trail proving that non-compliant code never breached the perimeter.
Automated ticketing synchronization bridging communication gaps
Translating abstract regulatory controls into actionable engineering tasks has historically been plagued by miscommunication, delayed tickets, and cultural friction between security officers and software developers. Automated ticketing synchronization fundamentally rewrites this dynamic by acting as an intelligent translator between the boardroom’s compliance frameworks and the developer’s kanban board. When platforms like Vanta, Drata, or Secureframe detect a failing control—perhaps an expired access review or a missing Multi-Factor Authentication enforcement—they do not merely log an error in a compliance dashboard.
Instead, they dynamically generate structured, contextual tickets within issue-tracking systems such as Jira, Linear, or GitHub Issues, assigning them directly to the appropriate engineering squad with zero human intervention required.
This seamless synchronization establishes a shared operational reality where compliance officers and software engineers finally speak the same language. The generated tickets arrive pre-populated with technical context, including affected repository identifiers, exact asset classifications, regulatory framework references, and recommended remediation steps. As engineers resolve the issues in their native development environments and commit the fixes, the compliance platforms automatically detect the state change, close the corresponding tickets, and update the continuous monitoring evidence vault in real time.
This bidirectional feedback loop eliminates the dreaded end-of-quarter spreadsheet scramble, ensuring that compliance status is always an accurate reflection of engineering health. For instance, high-growth fintech enterprises scaling to meet PCI-DSS requirements utilize this automated synchronization to manage thousands of infrastructure alerts daily without expanding their compliance headcount, proving that rigorous security governance can scale efficiently alongside rapid product development.
Best practices for embedding security awareness training into pipelines
Integrating security education directly into the continuous integration and continuous deployment pipeline ensures that engineering teams learn secure coding principles contextually rather than through generic, once-a-year compliance seminars. Modern organizations leverage automated pipeline integrations to deliver bite-sized, actionable learning moments precisely when developers introduce risky patterns, transforming continuous integration tools into active educational hubs.
As G2 reviews highlight top platforms like Secureframe, Drata, Vanta, Sprinto, ISMSonline, Risk Ledger, and Archer, digital clinics now elevate compliance by adopting patient portal software to protect sensitive health metrics. This seamless digital integration ultimately empowers teams to conquer regulatory audits with unwavering confidence, proving that robust security and brilliant patient care truly walk hand in hand.
- Trigger automated interactive micro-learning modules within developer chat applications the moment a static analysis security testing tool flags a recurring vulnerability pattern, ensuring the educational context is immediate and relevant.
- Incorporate peer review checklists directly into continuous integration status checks, requiring explicit verification of secure design principles before pull requests can advance toward deployment environments.
- Gamify secure coding achievements by integrating pipeline security scores into internal engineering dashboards, rewarding teams that maintain zero-vulnerability streaks with recognition and autonomy.
- Utilize automated feedback loops that supply clear, human-readable remediation guides inside failing build logs, turning every blocked deployment into an opportunity for hands-on technical growth.
- Establish feedback channels where engineering teams can easily contest false positives or suggest policy adjustments, fostering a collaborative security culture rather than an authoritarian compliance mandate.
Automated compliance is not merely about passing audits; it is about building a resilient engineering culture where security and velocity reinforce one another.
Ultimately, harmonizing speed with compliance relies on the relentless pursuit of automation, removing manual burdens from human shoulders and placing them onto intelligent software platforms. By weaving security policies directly into pull requests, synchronizing workflows through smart ticketing, and continuously educating developers inside their native pipelines, organizations construct an impenetrable yet frictionless digital foundation. This approach ensures that as markets evolve and regulatory landscapes shift, businesses remain simultaneously innovative, trustworthy, and audit-ready.
Assessing third-party vendor risk management functionality uncovers critical vulnerabilities in supply chain security oversight.
Modern digital ecosystems resemble interconnected webs where a single compromised thread can destabilize an entire enterprise infrastructure. Organizations frequently focus inward while leaving their digital gates wide open to external partners, software vendors, and cloud service providers whose security postures directly impact operational integrity. Regulatory bodies and market forces now demand absolute visibility far beyond primary operations, transforming third-party oversight from an administrative afterthought into a core pillar of defensive resilience.
Navigating this complex terrain requires looking past glossy vendor brochures to inspect the foundational mechanics of automated risk governance tools. Platforms provided by compliance leaders utilize deep telemetry and continuous surveillance engines to map out vendor ecosystems, exposing hidden blind spots before malicious actors exploit them. Behind the sleek dashboards lies a rigorous methodology of continuous evaluation, replacing static annual spreadsheet audits with dynamic, real-time threat intelligence feeds that keep pace with rapid enterprise growth.
Methodologies for automated vendor questionnaire distribution scoring and periodic reassessment
Eliminating the heavy administrative drag of manual vendor oversight relies on intelligent automation frameworks that streamline information gathering and analysis. Modern compliance ecosystems deploy smart ingestion engines that intelligently route tailored security assessments based on data access levels, completely removing human bottlenecks from the initial intake phase. These systems ingest responses against standardized compliance frameworks such as ISO 27001, SOC 2, and HIPAA, instantly translating qualitative answers into quantifiable risk profiles.
Continuous monitoring layers actively ingest threat intelligence data, dark web mentions, and external attack surface scans to recalibrate vendor scores autonomously without requiring continuous human intervention. When a vendor’s security posture drifts or a critical CVE emerges within their infrastructure, the platform immediately adjusts their risk tier and triggers automated workflows for remediation teams. This hands-off yet deeply rigorous approach ensures that vendor ecosystems remain perpetually vetted, allowing security personnel to focus on high-priority strategic mitigation rather than chasing late paperwork.
Continuous automated oversight transforms static vendor assessments into living metrics, ensuring that supply chain vulnerabilities are identified and neutralized before they manifest as catastrophic breaches.
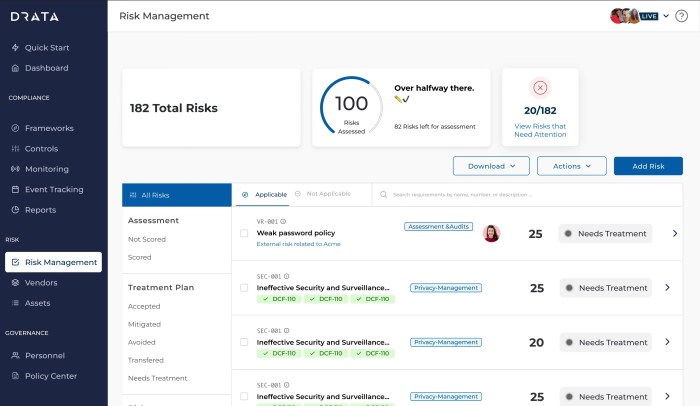
Visualizing a modern third-party risk management command center reveals a panoramic interface featuring real-time geographic mapping of global vendors, color-coded risk heatmaps highlighting high-exposure cloud integrations, and dynamic trend lines tracking remediation velocities over multi-quarter audit cycles. Detailed drill-down panels display automated questionnaire completion rates alongside continuous external vulnerability scan scores, painting a transparent picture of holistic supply chain health at a single glance.
Comparative matrix of vendor tiering criteria risk metrics remediation timelines and escalation protocols
Establishing clear operational thresholds across an enterprise supply chain requires a structured framework that categorizes vendors according to their access depth and operational criticality. The following matrix Artikels the standardized parameters used by automated compliance suites to govern vendor lifecycle management:
| Vendor Tiering Criteria | Automated Risk Scoring Metrics | Remediation Tracking Timelines | Escalation Protocols |
|---|---|---|---|
| Tier 1 Critical: Direct access to core production databases or PHI/Financial data systems. | Continuous external attack surface score below 70; unresolved critical CVEs > 0 days. | Critical findings must be resolved within 7 calendar days; high severity within 14 days. | Automated notification to CISO and vendor executive sponsor; contract review initiated at 14 days. |
| Tier 2 Important: Access to internal corporate networks or secondary SaaS applications. | Moderate external vulnerability score (70-84); pending SOC 2 Type II attestation. | Critical findings resolved within 14 days; high severity within 30 calendar days. | Automated ticket assignment to vendor account manager; restriction of data flow at 30 days. |
| Tier 3 Standard: Non-integrated peripheral vendors with zero access to internal data. | Basic compliance questionnaire verified; low external threat intelligence footprint. | Standard findings addressed within 60 calendar days of annual review cycle. | Automated reminder notifications at 30 and 45 days; administrative flag for non-renewal. |
Regulatory implications of failing to monitor downstream subcontractors in financial and healthcare sectors
Regulatory authorities across highly sensitive industries have unequivocally established that outsourcing operational execution does not equate to outsourcing ultimate legal and fiduciary liability. In the financial sector, stringent guidelines from bodies like the OCC and SEC mandate rigorous oversight of fourth-party and downstream subcontractors who handle sensitive transactional routing or consumer data storage. Similarly, HIPAA enforcement mechanisms in healthcare hold covered entities directly accountable for downstream vendor compliance failures, levying severe financial penalties and mandatory corrective action plans for unauthorized data exposures originating deep within the supply chain.
Failing to maintain comprehensive visibility over downstream entities often results in cascading compliance failures that trigger multi-jurisdictional audits, severe public reputational damage, and crippling class-action lawsuits following a data breach. Enterprises operating within these high-stakes environments must utilize compliance automation platforms to map multi-tiered vendor relationships, ensuring contractual flow-down provisions are actively monitored and validated through continuous technical verification rather than blind trust.
Closure
Ultimately, mastering the art of continuous compliance requires a harmonious blend of technological precision and proactive cultural alignment within your engineering teams. By bridging the eternal communication gap between rigid auditors and agile developers through automated workflows and seamless ticketing synchronization, organizations can permanently transcend reactive firefighting. As you implement these robust frameworks, remember that true security is never merely about passing an annual audit checkbox; it is about building a resilient, trustworthy foundation that empowers your business to innovate fearlessly and securely into the future.
