processunity pricing model reveals the intricate blueprint behind modern vendor risk management, weaving financial clarity into the often turbulent waters of enterprise software procurement. Organizations navigating these sophisticated digital ecosystems must carefully balance subscription tiers, operational expenditures, and long-term strategic investments to secure a resilient operational future.
Beneath the surface of standard software licensing lies a dynamic landscape of modular add-ons, user limitations, and hidden deployment costs that demand meticulous evaluation. By examining how financial commitments translate directly into robust security postures and streamlined administrative workflows, forward-thinking enterprises can unlock unprecedented value while safeguarding their supply chains against unforeseen vulnerabilities.
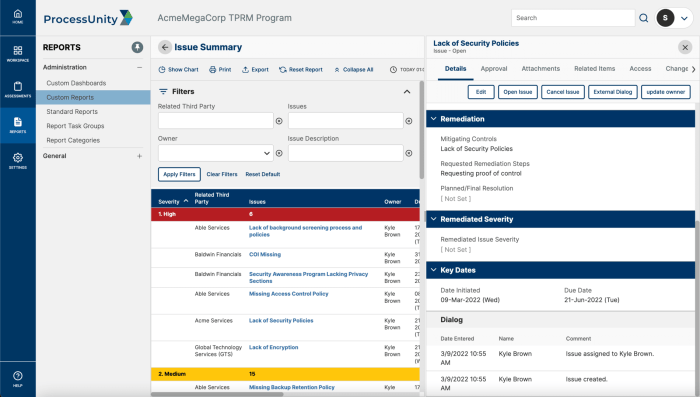
Organizations navigating the financial landscape of vendor risk management software must evaluate how ProcessUnity structures its subscription fees.
Source: website-files.com
Stepping into the modern corporate arena means recognizing that third-party relationships form the very backbone of daily operations, yet they also introduce sprawling webs of unseen vulnerabilities. Picture a bustling enterprise headquarters where dozens of departments continuously onboard digital vendors, software tools, and cloud partners without a unified map to track exposure. In this high-stakes environment, financial decision-makers face the intricate task of balancing robust operational security with unpredictable technology budgets.
Evaluating how modern governance platforms structure their financial commitments is no longer just an IT concern; it is a fundamental pillar of executive strategy that determines how safely an organization can scale in a hyper-connected global market.
Beneath the surface of every software acquisition lies an intricate philosophy regarding how value is delivered, measured, and sustained over multi-year cycles. Platform licensing in the third-party risk management sector operates far beyond simple software-as-a-service billing. Vendors construct their financial architectures around the premise of continuous risk mitigation, shifting the paradigm from passive data storage to active, real-time threat intelligence.
Evaluating the processunity pricing model reveals clear financial structures that empower modern enterprises. Observing the sharpcloud ltd company status 2022-2026 highlights resilient corporate growth amidst shifting market tides. Ultimately, mastering these fiscal frameworks allows organizations to invest wisely and accelerate toward a prosperous future with confidence.
When enterprises invest in these digital ecosystems, they are essentially purchasing a dynamic shield that adapts to regulatory shifts, market volatility, and emerging cybersecurity threats. This philosophy dictates that licensing costs should reflect the depth of ecosystem connectivity, the volume of automated workflows, and the breadth of cross-departmental collaboration rather than mere user seat counts.
Underlying Philosophy Behind Vendor Risk Management Platform Licensing
The core philosophy of modern risk platform licensing rests on the principle of proportional value realization and risk-adjusted scalability. Providers design their economic models to mirror the maturity curve of the client organization, ensuring that small compliance teams and massive multinational conglomerates alike pay an amount proportional to their third-party footprint. Imagine a rapidly growing financial institution that begins its risk journey by monitoring a mere fifty vendors, only to expand globally and ingest five thousand third-party profiles within twenty-four months.
Navigating the flexible processunity pricing model reveals smart financial clarity, much like exploring insightful kaon interactive 3d capabilities reviews that showcase brilliant visual transformation and engagement. Embracing these dynamic tools empowers organizations to scale confidently, proving that smart strategic investments truly drive lasting operational excellence and robust enterprise growth.
The licensing framework must gracefully accommodate this exponential growth without penalizing the organization for maturing its security posture. This approach treats software licenses not as a static utility bill, but as an elastic partnership engine that grows intelligently alongside the enterprise’s risk appetite and operational complexity.
To capture value effectively, platform architects tie financial tiers directly to the complexity of automated assessments, the integration of external threat feeds, and the reduction of manual administrative toil. Organizations are encouraged to automate tedious vendor questionnaires, transforming compliance officers from paper-pushers into strategic risk advisors. Successful licensing models recognize that security is an enterprise-wide sport involving procurement, legal, IT security, and executive leadership.
Consequently, the philosophical framework behind these pricing structures aims to break down traditional operational silos by incentivizing widespread stakeholder engagement across every functional department. When pricing aligns with risk reduction rather than feature restrictions, organizations achieve a healthier balance between fiscal discipline and uncompromising security standards.
Detailed Overview of Primary Cost Tiers Associated With Third-Party Governance Software
Navigating the marketplace requires a clear-eyed look at how vendors segment their offerings into distinct financial brackets designed to cater to varying organizational sizes and risk profiles. Entry-level subscriptions typically target mid-market companies seeking foundational repository management and standardized vendor assessment templates. Moving upward, mid-tier packages introduce advanced workflow automation, custom risk scoring algorithms, and moderate API connectivity for seamless integration with existing enterprise resource planning systems.
Enterprise-grade packages unlock the full spectrum of capabilities, featuring unlimited third-party profiles, deep analytical dashboards, dedicated customer success architects, and bespoke regulatory compliance mapping tailored to stringent global mandates such as GDPR, HIPAA, or SOC 2.
Organizations often visualize this pricing spectrum through a tiered architectural pyramid where each ascending level delivers exponential capabilities rather than incremental updates. Below is a comprehensive breakdown comparing base subscription tiers against enterprise-level packages:
| Subscription Feature | Base Tier (Starter) | Professional Tier (Mid-Market) | Enterprise Tier (Advanced) |
|---|---|---|---|
| Active Vendor Limit | Up to 100 Vendors | Up to 1,000 Vendors | Unlimited Vendors |
| Assessment Automation | Standard Templates Only | Customizable Questionnaires | AI-Driven Dynamic Risk Scoring |
| API & System Integration | Limited Export Options | Standard CRM & ERP Connectors | Bi-Directional Custom Integrations |
| Support & Advisory | Standard Email Ticketing | Priority Support & Webinars | Dedicated Customer Success Manager |
Hidden Fees Encountered During Vendor Onboarding and Deployment
The journey toward full operational deployment frequently uncovers financial obligations that remain obscured during initial sales demonstrations and contract negotiations. Enterprises often budget strictly for the baseline software subscription, only to discover that legacy data migration, custom API development, and specialized user training incur substantial professional services charges. For instance, a global logistics enterprise migrating ten years of fragmented vendor spreadsheets into a modern platform might face unexpected data cleansing and schema mapping fees that inflate deployment budgets by twenty to thirty percent.
Furthermore, organizations frequently overlook the internal resource cost of dedicating specialized engineers and compliance officers to oversee the integration timeline, which diverts valuable talent away from core revenue-generating projects.
Additional financial friction arises when organizations demand bespoke reporting modules or advanced third-party threat feed integrations that fall outside standard out-of-the-box configurations. To maintain complete fiscal transparency, risk committees must thoroughly examine the fine print regarding implementation milestones, sandbox environments, and ongoing maintenance retainers. Overlooking these peripheral expenses can rapidly turn a promising software deployment into a budget overrun, forcing leadership to justify unpredicted expenditures mid-cycle.
Navigating the transparent tiers of the processunity pricing model reveals a clear path to fiscal clarity, much like understanding what is a marketing agency illuminates the mechanics of brand growth. By aligning structured operational costs with strategic vendor risk management, organizations unlock unprecedented efficiency, ensuring that every financial investment directly fuels resilient, long-term enterprise success.
“True financial governance in third-party risk management demands looking past the initial software price tag to account for the total cost of ecosystem integration, continuous administration, and strategic scalability.”
Impact of User Licensing Limits on Daily Administrative Workflows
Administrative efficiency within a risk management ecosystem is heavily dictated by how user licenses are allocated and enforced across diverse operational departments. Many platform pricing models impose strict caps on fully privileged administrative seats while offering discounted or free read-only access for general business stakeholders. When user limits are overly restrictive, bottlenecks inevitably form during critical peak periods, such as annual vendor re-assessment cycles or unexpected security audits.
Imagine a scenario where the procurement department urgently needs to onboard a critical cloud vendor, but the single available administrative license is locked by a compliance officer conducting deep risk analysis in another division.
To overcome these operational hurdles without constantly purchasing expensive supplementary seats, organizations must implement structured internal governance policies governing license rotation and role-based access control. Understanding the operational rhythm of daily workflows helps administrators assign seats dynamically, ensuring that high-impact users retain uninterrupted access while casual reviewers utilize restricted stakeholder views. This strategic approach maximizes the return on investment for every purchased seat, preserving fluid cross-departmental collaboration and preventing administrative gridlock during high-pressure compliance windows.
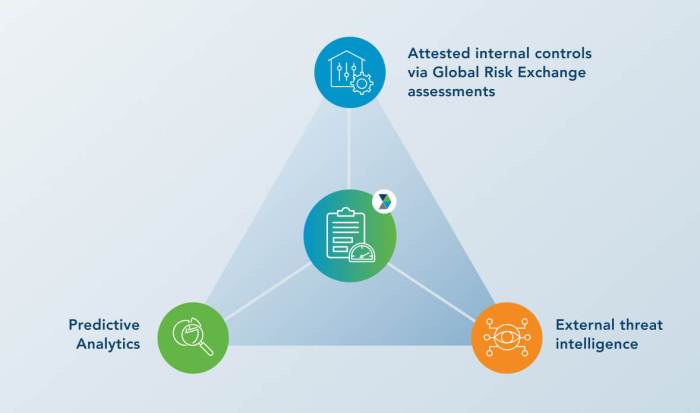
Procurement teams often struggle to calculate the total cost of ownership when adopting automated third-party oversight platforms.
Source: processunity.com
Stepping into the realm of automated vendor risk management resembles navigating a dense financial fog where the true destination remains obscured by unexpected fiscal turns. Modern enterprises frequently find themselves captivated by the sleek interface of a software dashboard, only to realize later that the sticker price is merely the opening chapter of a much larger ledger. Procurement leaders are tasked with deciphering complex pricing architectures that extend far beyond baseline vendor quotes, demanding a clear-eyed view of what it truly takes to sustain an enterprise-grade oversight engine over time.
Unlocking the full potential of automated third-party governance requires looking past the initial software contract to uncover the intricate web of operational realities that influence the corporate balance sheet. When organizations commit to these digital transformation journeys, they are not just buying a tool; they are injecting a massive new operational framework into their existing corporate ecosystem. This transition sets off a chain reaction of resource allocation, architectural adjustments, and specialized staffing needs that quietly reshape annual technology budgets.
Hidden operational expenses beyond initial software licensing fees
Deploying a sophisticated vendor risk platform invariably triggers a cascade of hidden expenditures that rarely appear on the initial sales proposal. Organizations must immediately contend with the intricate labor costs associated with workflow configuration, data cleansing, and historical vendor record migration. Moving thousands of legacy supplier profiles from fragmented spreadsheets into a centralized, automated repository demands dedicated human hours, often requiring specialized external contractors who command premium hourly rates.
Furthermore, user adoption friction introduces productivity dips across business units, as internal stakeholders and external vendors alike grapple with steep learning curves that temporarily slow down procurement velocity.
Technical integration expenses represent another formidable blind spot for unwary budget planners. Seamlessly connecting a risk management platform to existing enterprise resource planning software, human resources databases, and single-sign-on identity providers requires custom API development and rigorous security testing. Maintenance of these integration pipelines demands ongoing developer attention to prevent data synchronization failures whenever underlying enterprise systems undergo routine updates.
Below is a detailed breakdown of the fundamental budget categories required to achieve seamless system integration without destabilizing corporate finances.
- Custom API middleware development and ongoing maintenance for seamless data synchronization across enterprise architecture.
- Comprehensive data migration audits, legacy record cleansing, and standardization of disparate vendor taxonomies.
- Specialized internal staff training programs, continuous certification courses, and change management consultancy fees.
- Rigorous third-party penetration testing, cybersecurity compliance validation, and continuous vulnerability assessment protocols.
Visualizing this operational footprint reveals a sprawling blueprint of interconnected costs, resembling a complex industrial machinery setup where the engine purchase is just the beginning. Imagine a sprawling control room glowing with live data feeds, surrounded by specialized technicians meticulously calibrating dials, writing custom code bridges, and continuously feeding raw materials into the system to keep it running smoothly. This vivid mental picture illustrates that the platform is a living, breathing ecosystem that constantly consumes human capital and technical resources long after the ink on the initial software contract has dried.
Financial implications of scaling internal assessment modules
As organizations mature in their risk maturity lifecycle, the appetite for deeper, more frequent vendor evaluations expands exponentially, directly impacting multi-year financial projections. Scaling internal assessment modules from a baseline Tier-1 vendor inventory down to a comprehensive Tier-3 and Tier-4 supplier network triggers tiered software licensing bumps and unpredictable consumption-based fees. This growth trajectory mirrors the real-world trajectory of global supply chain giants like Target or Procter & Gamble, where expanding oversight from critical direct vendors to thousands of sub-tier component providers multiplied their monitoring volume by a factor of ten, fundamentally altering their recurring software expenditures.
Expanding the scope of automated questionnaires, continuous monitoring feeds, and specialized risk modules—such as cybersecurity ratings, anti-bribery screening, and environmental, social, and governance metrics—creates a compounding financial commitment. Over a multi-year deployment, these modular expansions can easily outpace the baseline contract inflation, turning a predictable software subscription into a volatile operating expense. Strategic financial planning must account for these inevitable growth vectors by locking in multi-year price ceilings and carefully modeling how supplier onboarding velocity dictates license tier thresholds.
Influence of external advisory services on overall project expenditures
Navigating the complex regulatory requirements of modern vendor risk management often forces organizations to enlist external advisory firms, transforming software adoption into a hybrid technology and professional services engagement. Big Four accounting firms and boutique risk consultancies play a pivotal role in designing custom assessment frameworks, mapping compliance mandates like GDPR or HIPAA into the platform, and interpreting complex vendor security telemetry.
These external partnerships introduce substantial financial commitments that can occasionally rival or even exceed the annual software licensing costs, demanding rigorous oversight from procurement executives.
The financial gravity of external advisory services is most acutely felt during the initial policy design and framework configuration phases, where expert guidance is indispensable for establishing defensible risk methodologies. However, relying on external consultants for routine questionnaire reviews and tier-1 vendor validations can create a dangerous dependency that inflates ongoing project expenditures. Establishing a clear transition plan to phase out high-priced external advisors as internal teams gain proficiency is paramount to protecting the long-term return on investment of the oversight platform.
Budgeting methods for long-term maintenance and internal resource allocation
Securing the longevity of an automated third-party oversight platform requires moving away from reactive spending models and embracing a disciplined, multi-year financial runway built on precise internal resource calculations. Organizations must treat software maintenance not as a static line item, but as a dynamic pool of funds reserved for continuous optimization, administrator certifications, and regular framework audits. Neglecting this long-term budgetary discipline frequently leads to platform stagnation, where the software ceases to reflect evolving corporate risk appetites and ultimately joins the graveyard of underutilized enterprise tools.
Effective resource allocation involves designating dedicated full-time equivalents to manage platform administration, vendor dispute resolution, and executive reporting dashboards, rather than treating risk management as a fragmented, side-of-the-desk duty for already overburdened procurement professionals. Grounding these financial forecasts in realistic labor market data ensures that the organization retains the necessary talent to drive the platform forward. The underlying mathematical reality of maintaining a sustainable risk program is anchored by a strict budgetary formula:
Total Sustainable Ownership Cost equals Baseline Licensing multiplied by the sum of Integration Overhead, Scaling Multipliers, and Dedicated Full-Time Internal Human Capital Investment.
Enterprise buyers require clear visibility into how modular add-ons influence the overarching financial commitment for supply chain governance tools
Navigating the complex digital ecosystem of third-party risk management requires a keen eye on the financial mechanics that dictate modern software investments. Procurement architects stepping into this arena often find that the initial software license is merely the baseline of a much larger budgetary journey, where strategic expansion directly shapes long-term fiscal forecasting.
Organizations must look beyond the sticker price to understand how incremental capability upgrades scale in tandem with corporate growth, regulatory demands, and the sheer volume of entities flowing through digital supply chains. Transparency in software architecture allows leaders to architect predictable budgets without sacrificing the agility needed to protect modern enterprises from emerging operational threats.
Impact of optional regulatory compliance modules on baseline software expenditures
Deploying specialized regulatory frameworks transforms a standard operational risk platform into an exhaustive compliance command center. When enterprises integrate optional compliance modules—such as targeted frameworks for GDPR, HIPAA, or industry-specific cybersecurity mandates—the baseline software expenditure naturally shifts upward to reflect the deeper data ingestion and automated reporting capabilities required.
These supplementary compliance engines demand sophisticated underlying architecture to continuously monitor, parse, and report on sprawling vendor ecosystems. Organizations typically witness an expansion in their core software investment because these modules automate intricate audit trails and drastically reduce the manual labor hours traditionally spent compiling regulatory disclosures. While the upfront software costs elevate, the mitigation of potential non-compliance penalties provides a compelling counterbalance for executive leadership.
Strategic deployment of these compliance features ensures that security teams are not just reacting to audits, but maintaining a continuous posture of readiness. The financial commitment acts as an insurance policy, where every dollar spent on modular compliance directly translates to minimized legal exposure and accelerated deal velocity during enterprise procurement reviews.
Financial mechanics behind purchasing supplementary vendor assessment capacity
Scaling a vendor portfolio invariably triggers the need for expanded assessment capacity, a metric fundamentally tied to the volume of active third-party profiles evaluated within the platform. Software tiering structures usually penalize sudden capacity bottlenecks, making it essential for financial planners to map out anticipated vendor onboarding velocities well in advance.
Acquiring additional assessment slots operates on tiered consumption models, where bulk purchasing often yields marginal unit cost reductions. However, underestimating these capacity thresholds can result in overage fees or sluggish workflow progression, frustrating procurement teams and delaying critical onboarding cycles.
Enterprise buyers must calculate the total cost of ownership by factoring in historical onboarding data. Organizations experiencing aggressive supply chain expansion can secure predictable expenditure patterns by negotiating flexible capacity blocks that scale dynamically with seasonal onboarding surges rather than committing to rigid, peak-capacity annual licenses from day one.
Supplementary capacity tiers reward proactive forecasting, turning unpredictable overage penalties into manageable, volume-discounted operational line items.
Monetary trade-offs between choosing bundled feature sets versus standalone functional packages
Decision-makers frequently debate whether to acquire an all-encompassing suite of governance tools or selectively assemble a mosaic of standalone functional packages. Bundled offerings present an illusion of comprehensive value, yet they often bundle features that specific enterprise units may never actively utilize, leading to capital inefficiency.
Analyzing the processunity pricing model reveals critical operational costs, much like how modern organizations optimize resource allocation through intuitive facility scheduling software that paints a vivid picture of seamless daily coordination. Embracing these smart financial frameworks empowers teams to overcome budget hurdles brilliantly, ensuring that mastering the processunity pricing model becomes your ultimate catalyst for extraordinary growth.
Standalone packages, conversely, offer pinpoint accuracy for distinct operational challenges but can introduce integration friction and fragmented data silos across different departments. Evaluating these monetary trade-offs demands a rigorous internal audit of current technological maturity and genuine departmental needs.
- Comprehensive software bundles reduce administrative vendor management overhead by consolidating billing and support contracts under a single enterprise agreement.
- Standalone functional packages allow emerging organizations to minimize initial capital outlay by purchasing strictly what is necessary for immediate operational survival.
- Custom modular assemblies often incur higher configuration and API maintenance costs over time, offsetting the initial savings achieved by bypassing full enterprise suites.
- Unified feature sets generally provide smoother cross-departmental visibility, eliminating the hidden labor costs associated with manually bridging disparate software applications.
Descriptive illustration scenario depicting how an expanding vendor ecosystem alters monthly software expenditures
Imagine a mid-sized financial technology firm that starts its third-party risk management journey overseeing a modest roster of fifty critical cloud vendors. Initially, the organization operates comfortably on a standard baseline subscription, utilizing basic assessment questionnaires and automated scoring matrices with minimal monthly variance.
As the firm aggressively expands its product offerings, the vendor ecosystem balloons to over five hundred active third-party partners spanning global jurisdictions. This rapid scaling forces the organization to unlock supplementary assessment capacity blocks to handle the sheer influx of incoming security reviews.
Simultaneously, entering new international markets mandates the activation of specialized data privacy compliance modules to satisfy regional regulatory oversight. Consequently, the monthly software expenditure evolves from a modest, static subscription fee into a dynamic, multi-tiered financial commitment. The visual depiction of this operational growth reflects a staircase financial model, where every major business expansion step upward triggers a corresponding, calculated shift in recurring platform investments.
Mapping optional modules to their estimated financial weight, Processunity pricing model
Evaluating the financial impact of modular software additions requires a structured comparative analysis of how individual components contribute to the total cost of ownership. The following data breakdown maps essential expansion modules against their relative budgetary influence within a standard enterprise software deployment.
| Optional Module Category | Primary Functional Scope | Estimated Financial Weight | Budgetary Impact Profile |
|---|---|---|---|
| Advanced Regulatory Frameworks | Automated compliance mapping for GDPR, HIPAA, and ISO standards | High | Significant baseline expansion, offset by reduced audit labor |
| Supplementary Assessment Packs | Expanded tier-one and tier-two vendor evaluation capacity | Medium-High | Scales dynamically with organizational vendor onboarding velocity |
| Continuous Monitoring Feeds | Real-time dark web, financial health, and cyber threat intelligence | Medium | Recurring subscription uplift with high operational utility |
| Custom API Integration Tools | Seamless data synchronization with existing enterprise ERP and CRM systems | Low-Medium | One-time configuration investment with minimal ongoing maintenance |
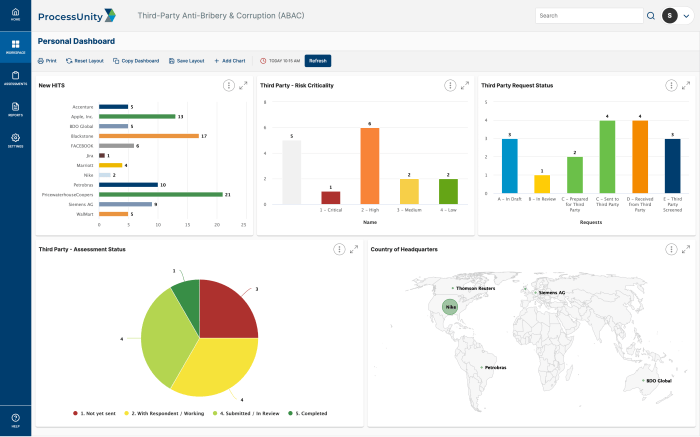
Financial decision makers benefit Greatest from Contrasting Software Expenditures against the Tangible Reduction of Third-Party Security Incidents: Processunity Pricing Model
Source: cloudfront.net
Looking past the initial invoice of any enterprise compliance platform reveals a deeper narrative about financial preservation and operational resilience. Forward-thinking executive teams increasingly evaluate their governance budgets not merely as sunk administrative costs, but as dynamic shields actively deflecting catastrophic enterprise losses. When capital allocation aligns directly with advanced risk mitigation, the conversation shifts from minimizing software outlays to maximizing organizational security postures.
Deploying automated vendor risk management tools fundamentally transforms how organizations protect their digital perimeters and financial health. Manual vendor vetting processes, traditionally weighed down by fragmented spreadsheets and endless email chains, drain valuable human capital while leaving blind spots wide open for sophisticated threat actors. Transitioning to a streamlined, automated ecosystem replaces costly human error with relentless digital vigilance, ensuring every external partner continuously meets rigorous compliance standards without burning out internal compliance teams.
Financial Returns Realized Through Automated Vendor Vetting Procedures
Calculating the true economic yield of automated oversight platforms requires examining both direct labor savings and avoided breach penalties. Organizations often discover that manual assessment cycles consume hundreds of hours per vendor, translating into exorbitant internal labor expenses that scale inefficiently as supply chains expand. Automated platforms cut review times dramatically, allowing lean compliance teams to manage triple the vendor volume without requiring proportional headcount growth.
This massive compression of administrative hours directly converts into recaptured payroll value, which can then be reinvested into core business innovations rather than routine paperwork.
Furthermore, early detection of compliance anomalies prevents minor vendor misconfigurations from cascading into enterprise-crushing security crises. Historical data from major cybersecurity research firms consistently demonstrates that the average cost of a third-party data breach easily reaches into the millions when factoring in regulatory fines, litigation, and brand erosion. By catching vulnerabilities during the initial automated onboarding phase, platforms neutralize financial liabilities before they ever materialize on the balance sheet.
Investing in automated vendor risk management is not an operational expense; it is a vital financial hedge against catastrophic supply chain disruption and enterprise-wide reputational damage.
Comparative Analysis of Manual Oversight Labor Versus Automated Platform Subscriptions
Evaluating the ledger between traditional manual reviews and automated subscription models illuminates a stark contrast in long-term fiscal predictability. Manual oversight relies heavily on tribal knowledge, disparate document storage, and tedious manual follow-ups, creating a hidden overhead that swells silently over time. Conversely, an enterprise software subscription establishes a predictable, fixed annual cost structure that scales predictably alongside corporate growth.
Consider a mid-market enterprise evaluating these two distinct operational pathways through financial modeling:
| Operational Metric | Manual Oversight Approach | Automated Platform Subscription |
|---|---|---|
| Average Time Per Vendor Assessment | 15 to 25 Business Days | 2 to 4 Business Days |
| Full-Time Equivalent Staff Requirement | 4 to 6 Compliance Specialists | 1 to 2 Oversight Managers |
| Cost Predictability and Variance | High (Subject to overtime and turnover) | Low (Fixed annual licensing fee) |
| Audit Trail Reliability and Speed | Fragmented and Labor-Intensive | Instantaneous, Centralized Reporting |
This structural shift eliminates the financial volatility associated with staff turnover and training cycles, insulating procurement budgets from unexpected operational shocks. Leaders gain clear sightlines into their recurring compliance expenditures, enabling precise financial forecasting without sacrificing depth of analysis.
Qualitative and Quantitative Methodologies for Measuring Risk Mitigation Value
Translating abstract security improvements into concrete financial metrics demands a balanced approach combining hard data analytics with qualitative risk scoring. Organizations frequently deploy multi-dimensional scoring frameworks that assign monetary values to averted operational disruptions and preserved customer trust. By tracking metrics such as mean time to remediate vendor vulnerabilities, leadership teams can directly correlate software utilization with a measurable drop in high-risk vendor relationships.
Qualitative assessments complement these numeric models by evaluating improvements in stakeholder confidence, regulatory readiness, and cultural alignment across the supply chain. Visual inspection of executive dashboards reveals real-time risk heat maps that empower board members to make swift, defensible capital allocation decisions. These comprehensive evaluation strategies ensure that every dollar spent on governance tooling delivers verifiable protection for the enterprise brand.
Justification of Multi-Year Platform Expenditures Through Breach Prevention
The argument for multi-year software commitments becomes overwhelmingly clear when weighed against the devastating financial fallout of a single successful cyber attack originating from a compromised vendor. Real-world market events, such as the massive third-party breaches experienced by retail giants and software supply chain providers, illustrate that recovery costs routinely exceed tens of millions of dollars in direct damages alone.
Multi-year platform subscriptions cost a fraction of that exposure, functioning essentially as an enterprise-grade insurance policy that actively works to prevent the disaster rather than just paying out after the fact.
When procurement committees review long-term software contracts, anchoring the investment to the concept of breach avoidance alters the entire financial narrative. Preventing just one major security incident over a three-year licensing period instantly yields a positive return on investment that dwarfs the cumulative subscription fees. This undeniable economic reality transforms the software purchase from a discretionary departmental budget item into an essential pillar of corporate financial defense.
Operational Efficiencies Gained Through Streamlined Risk Assessments
Unlocking maximum value from compliance technology requires a systematic focus on workflow optimization and administrative reduction. Organizations that successfully implement modern vendor governance tools consistently report transformative improvements in daily operational execution.
- Drastic reduction in vendor onboarding bottlenecks through standardized, self-service security questionnaires.
- Centralization of all third-party documentation, eliminating redundant data entry and version control errors.
- Real-time continuous monitoring alerts that replace reactive annual reviews with proactive threat intelligence.
- Automated generation of audit-ready compliance reports tailored for regulatory bodies and executive stakeholders.
These targeted operational enhancements collectively empower organizations to navigate complex regulatory landscapes with unprecedented speed and confidence. By removing friction from the third-party oversight lifecycle, enterprise teams can dedicate their focus entirely to driving strategic business growth.
Negotiating favorable software acquisition terms demands a deep understanding of enterprise vendor sales cycles and contract structuring.

Source: wixstatic.com
Securing an advantageous enterprise software agreement resembles a high-stakes chess match where timing, leverage, and strategic positioning dictate the ultimate financial outcome. When procurement specialists sit across the table from vendor account executives, the objective extends beyond merely trimming the initial quote; it requires crafting a resilient commercial foundation that protects organizational capital as the digital ecosystem expands. Navigating the complexities of enterprise sales requires recognizing that software pricing is rarely static, offering a dynamic landscape where informed buyers can substantially optimize their expenditures through deliberate tactical planning.
Entering the negotiation arena equipped with a comprehensive blueprint transforms the entire procurement experience from a reactive expense management exercise into a proactive value-creation initiative. Enterprises that master the art of contract structuring consistently outmaneuver rigid standard pricing sheets, turning vendor sales incentives and quarter-end quotas into powerful leverage points. Every clause, from the initial billing frequency to the final renewal cap, presents an opportunity to safeguard operational budgets while ensuring seamless access to mission-critical governance capabilities.
Strategic framework for approaching software vendor pricing negotiations
Building a robust negotiating posture begins long before the first exploratory call with a software representative, grounding every move in meticulous market research and internal alignment. Procurement teams must map their organization’s growth trajectory against the vendor’s fiscal calendar, aligning purchase timelines with periods when sales teams experience heightened pressure to close deals. By mapping out alternative risk management solutions and demonstrating a credible competitive threat, buyers strip away the vendor’s presumption of exclusivity, instantly shifting the balance of power toward the negotiating table.
Visualizing the negotiation floor reveals a high-stakes boardroom where detailed deployment roadmaps and utilization forecasts serve as the primary currency for unlocking hidden concessions. Account executives respond best to organized buyers who present clearly defined user tiers and documented budgetary boundaries rather than vague expressions of interest. This disciplined approach eliminates unnecessary administrative delays and signals to the vendor’s executive leadership that the enterprise is a sophisticated buyer capable of executing a swift, mutually beneficial transaction.
Impact of multi-year agreement commitments on annual per-user licensing fees
Committing to a multi-year software subscription acts as one of the most reliable levers for compressing the annualized cost per user within enterprise vendor agreements. Software providers heavily prioritize predictable, recurring revenue streams to satisfy their investors, and they are mathematically programmed to trade short-term margin for long-term customer retention. By locking into a three-to-five-year horizon, procurement leaders can routinely secure double-digit percentage reductions on baseline per-seat pricing compared to standard twelve-month renewals.
Organizations leveraging multi-year structures must carefully balance the pursuit of immediate savings against the risk of over-committing to license volumes that may fluctuate as corporate headcount shifts. To mitigate this exposure, sophisticated buyers integrate contractual mechanisms that allow for controlled downward adjustments or phased license activation schedules across the lifespan of the agreement. This ensures the organization captures the aggressive discounting associated with long-term commitments without getting trapped paying for idle digital seats.
Tactics for securing volume discounts during initial contract formulation phases
Initial contract formulations represent the golden window for capturing maximum volume-based economies of scale before the vendor considers the account a secured asset. Procurement professionals should avoid purchasing software licenses in isolated, piecemeal increments, instead consolidating cross-departmental demand into a single, highly attractive enterprise-wide initial deployment order. Vendors frequently maintain hidden discounting tiers that only activate when projected seat counts cross specific numerical thresholds, making comprehensive internal needs assessments an absolute prerequisite for maximum financial efficiency.
The following structured tactics provide procurement teams with actionable pathways to successfully unlock aggressive volume pricing tiers during the foundational contracting phase:
- Consolidate decentralized departmental software requests into a unified enterprise-wide purchasing pool to immediately trigger tier-one volume pricing brackets.
- Demand tiered discounting schedules that automatically retroactively apply superior price breaks as the organization expands its user base within the initial contract year.
- Leverage brand influence by offering the software vendor a high-profile customer case study or public reference in exchange for waive-down fees and accelerated volume discounts.
- Tie initial volume commitments to guaranteed professional services hours or customized onboarding support rather than accepting flat-rate software-only discounts.
Importance of locking in price protection clauses for future user expansion
Securing the initial software purchase price represents only half the battle; defending the organization against aggressive inflationary hikes during mid-term expansions requires deliberate contract architecture. Without legally binding price protection clauses, enterprises frequently find themselves held captive by exorbitant add-on seat costs when their initial user allocations inevitably run dry. Vendors naturally capitalize on high switching costs once an organization embeds a platform into its daily operations, making proactive anti-inflationary caps a non-negotiable safeguard for long-term budget predictability.
Enterprise buyers utilize specific contractual language to freeze or cap future price escalations, ensuring that scaling the user base remains economically viable as operations grow. The table below Artikels standard market protections versus high-risk procurement positions regarding future user expansion costs.
| Contractual Element | High-Risk Procurement Position | Optimized Enterprise Safeguard |
|---|---|---|
| Expansion Price Cap | Subject to vendor’s standard annual list price increases (often 5% to 10%). | Capped at a maximum of 2% annually or tied directly to the Consumer Price Index. |
| Add-On Seat Tiering | Additional seats priced independently based on current retail rates. | Additional seats locked into the original baseline volume discount tier. |
| Renewal Rate Security | Renewal pricing negotiated at the end of the term with zero guarantees. | Guaranteed maximum renewal rate increase not exceeding 5% of the expiring baseline. |
“The vendor shall not increase the recurring annual subscription fees, per-user licensing rates, or modular add-on costs by more than two percent (2%) upon any contract anniversary or renewal date, regardless of changes to standard commercial pricing lists or corporate restructuring on the part of the software provider.”
Assessing the financial viability of migrating from legacy risk management systems to modern platforms involves complex depreciation calculations.
Stepping away from aging risk infrastructure requires a hard-nosed financial reckoning. Organizations often cling to homegrown compliance tools out of comfort, but the hidden costs of maintaining obsolete servers and brittle custom code quietly drain enterprise budgets year after year.
Retiring legacy infrastructure in favor of agile, cloud-based compliance tools fundamentally alters an organization’s balance sheet. Traditional on-premise governance software demands hefty capital expenditures, requiring long-term depreciation schedules that tie up valuable liquidity. Shifting to a SaaS model transforms these rigid capital costs into predictable operating expenditures. When an enterprise finally pulls the plug on its aging hardware racks, the immediate cessation of pricey third-party maintenance contracts, specialized server upkeep, and emergency patching patches creates a palpable sense of financial relief.
Picture a dusty, blinking server room finally falling silent, its deafening cooling fans powering down for the last time, while finance teams watch server room power consumption drop to zero and IT headcount is successfully reallocated toward high-value strategic innovation rather than endless firefighting.
Amortization schedules and dual-running budget inflation
Evaluating the financial mechanics of software transitions requires a close look at how expenses are recognized over time. Custom-built internal assessment systems are traditionally capitalized as internal-use software, meaning their development costs are amortized over several years, creating a lagging indicator of expense on the income statement. Commercial software subscriptions, conversely, bypass complex multi-year asset capitalization. They land cleanly as straightforward, recurring operational expenses that align directly with current-period consumption and immediate tax efficiencies.
Compounding this transition is the unavoidable reality of the parallel run phase. Organizations rarely flip a switch and abandon legacy tools overnight. Instead, dual-running systems during transition periods temporarily inflate operational budgets. Enterprises find themselves paying double: maintaining the old infrastructure while concurrently funding cloud subscription fees, data synchronization middleware, and extensive dual-staff training. This temporary financial strain demands careful forecasting to ensure cash flow remains stable before the ultimate cost-saving benefits of the modern platform materialize.
Calculating comprehensive data migration expenses
Accurately forecasting the financial footprint of moving historical risk data to a modern cloud environment prevents costly budget overruns. Financial planners must systematically account for every variable involved in the extraction, cleansing, and secure transfer of sensitive vendor records.
- Audit existing data repositories to identify redundant, obsolete, and trivial records that do not warrant migration.
- Estimate the labor hours required from database administrators and compliance specialists to map legacy data fields to the new schema.
- Factor in third-party API integration costs and specialized middleware licensing fees necessary to bridge the old and new systems securely.
- Allocate funds for rigorous post-migration data integrity testing and compliance validation to prevent costly reporting errors.
The true cost of a legacy system is never what it took to build, but what it prevents the enterprise from becoming.
Concluding Remarks
Ultimately, mastering the financial mechanics of third-party governance platforms transforms a routine budgetary expense into a powerful catalyst for organizational growth and unwavering security resilience. When leaders align strategic contract negotiations with a clear vision of risk mitigation, every dollar invested becomes a vital building block for a safer, more prosperous corporate horizon.
