sprinto b2b business model redefines how modern enterprises conquer the chaotic mountains of regulatory compliance, transforming a historically grueling burden into a streamlined engine of operational excellence. Across sprawling cloud ecosystems, automated governance frameworks are quietly dismantling old barriers, replacing endless human friction with precise, real-time vigilance that empowers security teams to breathe easier.
Behind this technological leap lies a robust financial and operational architecture engineered to capture market share, build unshakeable customer trust, and protect growing corporations against unforeseen risks. As we examine the intricate blueprint powering this movement, we uncover a fascinating narrative of innovation, strategic partnerships, and enduring enterprise resilience that points toward a profoundly secure digital future.
Unraveling the architectural blueprint behind how Sprinto delivers continuous compliance infrastructure to enterprise organizations

Source: googleusercontent.com
Modern enterprise operations demand a paradigm shift away from traditional, fragmented governance methods toward resilient, always-on compliance engines. As digital perimeters expand across sprawling multi-cloud architectures, the traditional manual checklist approach to information security has buckled under the sheer velocity of code deployment and infrastructure changes. Sprinto intercepts this operational friction by weaving compliance directly into the runtime fabric of the enterprise, transforming regulatory frameworks from static paperwork exercises into dynamic, programmatic guarantees.
This architectural blueprint redefines how security leaders protect their assets, replacing anxious audit seasons with an enduring state of operational readiness.
Automated governance frameworks fundamentally alter the daily reality of enterprise security teams by lifting the crushing weight of manual evidence collection and policy enforcement. When organizations rely on legacy methods, security engineers spend countless hours chasing down screenshots, validating access logs, and manually correlating policies with operational realities, which drains vital resources away from core product innovation and threat mitigation.
By translating complex regulatory mandates such as SOC 2, ISO 27001, and HIPAA into machine-readable control checks, automated platforms systematically eliminate the bureaucratic friction that traditionally paralyzes engineering momentum. The software acts as an invisible, tireless sentinel that synchronizes system states with control requirements in real time, ensuring that security postures remain robust without requiring constant human vigilance or inducing employee burnout.
Consequently, security professionals regain their strategic focus, shifting from reactive firefighters to proactive architects of trust.
Compliance is no longer a seasonal distraction of frantic spreadsheets and retroactive documentation; it is an intrinsic, automated heartbeat running silently in the background of enterprise engineering.
Continuous cloud environment monitoring mechanisms
The operational resilience of the platform rests on a sophisticated matrix of event-driven watchers and API-level integration layers that interface directly with enterprise infrastructure. Instead of relying on periodic snapshots, the system deploys read-only agents and native cloud connectors that continuously observe configuration drifts, IAM permission changes, and resource provisioning activities across the entire technology stack. This deep-seated instrumentation listens for webhook events and utilizes polling routines to capture state changes the exact millisecond they occur, cross-referencing them against established security baselines.
When a deviation or potential vulnerability is detected, the engine instantly flags the anomaly, contextualizes the risk, and initiates automated remediation workflows or alerts the responsible engineer before a minor misconfiguration escalates into a compliance failure.
The journey from manual, error-prone audits to a frictionless, automated evidence collection model follows a deliberate operational evolution within the enterprise. Organizations typically navigate a structured multi-stage transformation that systematically replaces human dependency with programmatic precision.
- Scoping and Framework Mapping: The enterprise defines its regulatory targets and imports custom or standard control frameworks into the platform to establish the baseline criteria for automated evaluation.
- Infrastructure Integration: Security and DevOps teams authorize read-only API access across cloud providers, identity providers, and endpoint management systems to establish comprehensive data pipelines.
- Baseline Discovery and Gap Analysis: The system automatically scans connected environments, maps existing configurations against required controls, and highlights immediate vulnerabilities requiring remediation.
- Automated Control Activation: Custom monitoring rules are deployed across the tech stack to continuously check for compliance drift and gather immutable audit logs without manual intervention.
- Continuous Auditor Readiness: Evidence is systematically tagged, structured, and stored in a centralized compliance vault, ready for instant export or direct auditor review whenever assessments commence.
Technological synergies across multi-cloud ecosystems and third-party software
Achieving universal compliance coverage requires bridging disparate technologies into a cohesive, unified data model capable of ingesting signals from virtually any software-as-a-service application or cloud hosting provider. Sprinto achieves this architectural harmony through a modular integration layer built on standardized API adapters, webhook receivers, and secure authentication protocols like OAuth. This design allows the platform to converse fluently with hyperscale cloud environments such as Amazon Web Services, Microsoft Azure, and Google Cloud Platform, while simultaneously pulling telemetry from version control systems, HR software, and ticket-tracking tools.
By normalizing these diverse data streams into a singular schema, the platform constructs an unbroken chain of custody and accountability, proving beyond a shadow of a doubt that administrative controls, encryption standards, and access policies are strictly enforced across the entire organizational ecosystem.
Investigating the financial engineering and revenue pathways powering modern compliance automation platforms

Source: sopro.io
Modern compliance automation is undergoing a massive economic evolution, transitioning from traditional, labor-intensive consulting models into high-velocity software ecosystems. Behind the sleek dashboards and automated evidence collection lies a sophisticated financial architecture designed to maximize enterprise lifetime value while neutralizing market volatility. This intricate monetary machinery fuels the engine room of continuous security operations.
The transition toward automated compliance has rewritten the balance sheets of modern B2B SaaS companies, replacing unpredictable professional services revenue with high-margin, software-driven yields. Understanding this fiscal landscape requires an unvarnished look at the numbers, margins, and structural engineering that keep automated trust centers profitable, scalable, and resilient against economic headwinds.
Structural advantages of tiered software subscription models within the security automation sector
Deploying a tiered software subscription model creates a natural economic self-selection mechanism that aligns platform capabilities directly with the expanding risk profiles of modern enterprises. As organizations scale from seed-stage startups tackling their first SOC 2 audit to multinational conglomerates managing global frameworks like ISO 27001, HIPAA, and GDPR simultaneously, their consumption of automated checks, cloud integrations, and policy templates grows exponentially.
Software subscription tiers capture this evolving value by structuring pricing around organizational maturity rather than arbitrary user counts, preventing revenue leakage while ensuring smaller entities are not priced out of vital security infrastructure.
This graduated packaging unlocks compounding growth vectors through strategic feature gating and automated expansion loops. When a mid-market enterprise outgrows basic automated evidence gathering and suddenly requires advanced vendor risk management or custom policy mapping, the friction to upgrade is remarkably low because the platform is already embedded into their daily engineering workflows. Furthermore, tiered models protect gross margins by ensuring that heavy resource consumers—such as enterprises running thousands of daily cloud asset scans—subsidize the compute capacity they utilize.
According to industry financial benchmarks from top-tier SaaS indices, companies utilizing robust tiered pricing structures routinely achieve Net Revenue Retention (NRR) rates exceeding 115%, proving that product-led expansion is the ultimate catalyst for compounding enterprise valuation.
Tiered subscription architecture converts complex regulatory requirements into predictable, scalable revenue engines that expand automatically alongside a client’s security footprint.
Recurring enterprise contracts and predictable cash flow generation
Securing long-term contractual commitments fundamentally alters the financial stability of B2B compliance platforms, replacing the erratic feast-or-famine cycles of legacy IT consulting with predictable, recurring cash inflows. Annual and multi-year subscriptions provide executive leadership with the financial visibility necessary to aggressively reinvest into research, development, and top-tier engineering talent without risking operational runway. This structural predictability acts as a robust financial shield against broader macroeconomic downturns, ensuring that compliance budgets—which are legally and operationally non-negotiable for enterprise vendors—remain insulated from discretionary IT spending cuts.
Mitigating customer acquisition volatility relies heavily on this recurring revenue foundation, transforming upfront sales investments into reliable, long-term yield generators. When compliance automation platforms lock in multi-year enterprise agreements, the Customer Acquisition Cost (CAC) payback period shortens dramatically, freeing up capital for targeted Account-Based Marketing (ABM) campaigns. Real-world financial modeling from high-growth security automation leaders demonstrates that maintaining an LTV-to-CAC ratio greater than 4:1 is entirely achievable when churn is suppressed below one percent monthly through automated, mission-critical workflows.
Enterprise buyers increasingly demand financial predictability on their own end, favoring fixed annual SaaS expenditures over unpredictable hourly consulting fees charged by traditional audit firms. This mutual alignment fosters deeply entrenched vendor relationships, where the compliance platform transitions from a vendor tool into an indispensable core operating system. The resulting cash flow consistency allows executive teams to forecast quarterly revenue with surgical precision, satisfying institutional investors and positioning the organization for sustained market leadership.
Sprinto B2B business model accelerates modern compliance journeys with precision, much like accessing reliable support via the deskgo.com customer service number to resolve operational hurdles instantly. This dynamic framework empowers enterprises to navigate complex security landscapes brilliantly, unlocking unprecedented growth through automated trust.
Enterprise pricing tiers and platform capabilities
Navigating the financial tiers of modern compliance automation requires a granular understanding of how features, capacity, and support structures scale to meet rigorous enterprise demands. The following matrix Artikels the operational parameters defining these distinct market segments.
| Pricing Tier | Feature Limitations | User Seat Capacities | Dedicated Support Levels |
|---|---|---|---|
| Growth | Single framework support (SOC 2 or ISO 27001), standard cloud integrations, basic automated evidence collection. | Up to 50 active user seats with standard permission controls. | Email and ticket-based support with a 24-hour response SLA. |
| Scale | Multi-framework mapping, advanced vendor risk management, custom policy builder, automated remediation workflows. | Up to 250 active user seats with role-based access control (RBAC). | Priority ticketing and scheduled quarterly strategic check-ins. |
| Enterprise | Unlimited frameworks, cross-mapping engines, custom API integrations, advanced threat intelligence feeds, dedicated tenant isolation. | Unlimited user seats with enterprise single sign-on (SSO) and SCIM provisioning. | Dedicated Customer Success Manager and 24/7 priority incident response. |
| Custom Global | Tailored multi-cloud governance, bespoke compliance frameworks, advanced data residency options, custom audit trails. | Unlimited enterprise-wide seats with granular multi-departmental partitioning. | Named Technical Account Manager with round-the-clock white-glove engineering support. |
A panoramic visual snapshot of this pricing infrastructure reveals a deliberate gradient of operational empowerment, where entry-level tiers provide foundational automated scaffolding, while upper-echelon plans deliver fortress-grade customization and dedicated human oversight. This tiered ecosystem ensures that organizations of every scale purchase precisely the computational and human resources required to maintain continuous trust posture.
Marginal cost dynamics of scaling compliance verification nodes
Engineering a continuous compliance platform demands a relentless focus on unit economics, particularly concerning the marginal cost of executing automated verification checks across rapidly expanding client infrastructures. As enterprise clients spin up thousands of new cloud instances, deploy microservices across multi-region Kubernetes clusters, and onboard hundreds of third-party SaaS vendors, the volume of API calls and configuration checks surges exponentially.
Maintaining healthy gross margins under this crushing data deluge requires highly optimized serverless architectures and intelligent caching layers that process compliance evidence asynchronously without triggering runaway cloud infrastructure bills.
The underlying infrastructure utilizes distributed serverless functions to execute lightweight compliance checks at the edge, ensuring that compute resources are consumed only when configuration drift or evidence collection events occur. This event-driven architecture prevents the capital inefficiency of perpetually running idle servers, driving the marginal cost per verification node down to fractions of a cent even as enterprise client nodes scale into the millions.
By decoupling the frequency of automated checks from linear infrastructure costs, compliance automation platforms achieve classic software economies of scale, converting massive data throughput into exceptional net profit margins.
Case studies from high-scale security automation deployments show that transitioning from monolithic cron-job verification scripts to event-driven serverless architectures reduces cloud compute expenditures by over forty percent while simultaneously boosting verification speed and accuracy. This engineering discipline ensures that as an enterprise client grows from a hundred cloud assets to half a million, the platform’s cost to serve remains exceptionally low, preserving the robust profit margins that fuel ongoing innovation and market expansion.
Decoding the psychological and operational triggers driving modern enterprises toward automated compliance solutions
Modern boardrooms and engineering floors share a silent, pervasive tension as the velocity of global business collides with the labyrinth of regulatory mandates. Enterprises no longer view compliance as a periodic, check-the-box exercise handled by a lone auditor in a back room, but rather as a high-stakes, existential operational pillar. Behind this shift lies a complex web of psychological pressures and administrative friction points that are fundamentally reshaping how organizations approach trust and security infrastructure.
The traditional approach to audit preparation resembles a slow-moving administrative disaster, accumulating massive unseen costs that drain both corporate treasuries and human capital. Organizations attempting to navigate frameworks like SOC 2, ISO 27001, or HIPAA through manual collection methods routinely underestimate the true toll of their operations. Engineering hours that should be dedicated to core product innovation and revenue-generating features are routinely hijacked by the mundane extraction of access logs, screenshot captures, and endless spreadsheet cross-referencing.
When dozens of high-salaried developers spend upwards of twenty percent of their sprint cycles hunting down policy documents and manually verifying cloud configurations, the invisible payroll leakage quickly scales into millions of dollars annually. Furthermore, this heavy reliance on human memory and manual artifact gathering introduces inevitable human error. A single missed configuration or outdated policy discovered on the eve of an audit can instantly derail a multi-million-dollar enterprise deal, forcing emergency remediation efforts that command premium consultancy fees and incur severe opportunity costs.
These compounding hidden expenses transform routine compliance preparation into a perpetual financial drain that quietly erodes competitive advantage.
Financial and operational consequences of manual compliance workflows
Executives navigating cross-border markets face a mounting tide of anxiety driven by the dual specter of catastrophic data breaches and aggressive regulatory penalties. Global privacy frameworks, ranging from the European Union’s GDPR to stringent state-level American legislation, carry financial penalties that can cripple enterprise balance sheets and irrevocably shatter brand equity. In this climate of heightened accountability, CISOs and executive boards recognize that regulatory oversight operates on a continuous, zero-tolerance basis.
The psychological burden on leadership is palpable, as a single credential compromise or unpatched vulnerability can trigger public scrutiny, shareholder lawsuits, and immediate loss of customer trust. Compliance automation has consequently emerged not merely as a technical upgrade, but as an indispensable executive shield that offers real-time visibility and proactive risk mitigation across the entire enterprise ecosystem.
Scaling security compliance across distributed, remote engineering teams introduces severe operational friction points that traditional management frameworks simply cannot accommodate. Chief Technology Officers frequently find themselves battling fragmentation, visibility gaps, and cultural resistance as they attempt to enforce uniform security standards across globally dispersed personnel.
- Decentralized asset inventories create massive blind spots, as remote developers spin up cloud resources outside of centralized IT visibility and change management policies.
- Version control inconsistencies across disparate developer workstations lead to conflicting security baselines and unpredictable vulnerability management cycles.
- Asynchronous communication channels make it notoriously difficult to enforce mandatory security awareness training and collect acknowledgment signatures in a timely manner.
- Manual evidence collection across multiple time zones introduces severe latency into audit preparation workflows, delaying critical product releases and enterprise sales cycles.
Continuous compliance automation transforms security from a reactive bottleneck into a proactive engine of enterprise growth and operational resilience.
In the dimly lit corner of a makeshift home office, a beleaguered security officer stares blankly into the glaring light of a massive, multi-tabbed spreadsheet. Hundreds of rows of fragmented server logs and disjointed access control lists swim before tired eyes, while sticky notes bearing frantic reminders crowd the laptop bezel. Every manual cross-reference feels like an exhausting exercise in archaeological excavation, unearthing outdated policies and broken links that threaten to unravel months of preparation.
Just a heartbeat away, on a sleek secondary monitor, a pristine, serene compliance dashboard glows with a calming palette of emerald green. Real-time widgets pulse gently with life, displaying automated checkmarks confirming 100 percent cloud asset coverage, flawless encryption standards, and continuously verified access protocols. The stark visual contrast captures the exact psychological transformation modern enterprises experience when transitioning from chaotic administrative panic to effortless, automated digital assurance.
Mapping out the strategic distribution channels and partnership ecosystems utilized to capture enterprise market share.

Source: collidu.com
Conquering the modern enterprise compliance market requires more than just an exceptional software architecture; it demands a relentless, multi-tiered distribution machinery. In a landscape where trust is currency and security is non-negotiable, the journey to market dominance is paved through sophisticated alliances and deeply embedded channel partnerships that turn third-party gatekeepers into active growth catalysts.
Scaling a continuous compliance infrastructure across Fortune 500 boardrooms and hyper-growth technology enterprises necessitates a strategic pivot away from traditional, solo go-to-market motions. By integrating deeply into the operational DNA of trusted industry intermediaries, compliance automation platforms can bypass legacy procurement friction and establish immediate credibility with risk-averse enterprise buyers who prioritize proven ecosystem validation above all else.
Modern compliance automation thrives on the agile Sprinto B2B business model, transforming security frameworks into structured growth engines. By illuminating complex metrics through vibrant hakio.com platform dashboards , teams visualize operational health with crystal clarity. This powerful visibility ultimately elevates the resilient Sprinto B2B business model, steering ambitious enterprises toward secure, unstoppable market success.
The catalytic impact of managed service providers and independent auditors on market expansion
Managed service providers and independent audit firms occupy a position of ultimate trust within the enterprise governance hierarchy, acting as the primary arbiters of security posture and regulatory adherence. When these entities embed compliance automation software into their core service delivery models, they fundamentally transform the adoption curve. Instead of selling directly to isolated security teams, the platform leverages an army of external advisors who routinely prescribe technological remedies to their enterprise clientele.
Independent auditors, facing massive capacity constraints amidst expanding regulatory frameworks like SOC 2, ISO 27001, and HIPAA, increasingly mandate automated evidence collection to streamline their own audit engagements. This symbiotic relationship turns traditional compliance bottlenecks into high-velocity acquisition channels, allowing the platform to scale its footprint organically through the existing client rosters of accounting powerhouses and specialized cybersecurity consultancies.
Visualizing this dynamic reveals a vast, interconnected web where the platform acts as the central nervous system for compliance data, while managed service providers and auditors serve as the vital sensory nodes reaching deep into isolated enterprise environments. Picture a bustling digital ecosystem where regional advisory firms no longer rely on manual spreadsheets and fragmented documentation, but instead log into a unified multi-tenant dashboard.
Sprinto accelerates compliance automation for modern enterprises by streamlining security workflows. As global data regulations tighten, organizations increasingly rely on syrenis cassie platform consent management solutions to handle user privacy preferences with precision and clarity. By integrating these robust governance tools, businesses protect consumer trust while empowering the core infrastructure of the Sprinto compliance framework to scale securely.
They seamlessly monitor dozens of enterprise clients simultaneously, drastically reducing their own operational overhead while automatically channeling new software licenses back to the foundational platform provider. This architectural leverage turns every participating auditor into an evangelist, creating a compounding growth loop that traditional direct sales teams could never replicate on their own accord.
Co-selling mechanics with major cloud hosting providers
Enterprise sales cycles are notoriously arduous, frequently mired in bureaucratic red tape, protracted security reviews, and endless procurement negotiations. Aligning with hyperscale cloud hosting giants fundamentally shortens this timeline by co-mingling sales incentives and embedding the compliance solution directly into the cloud infrastructure purchasing journey. Major cloud marketplaces serve as lucrative digital storefronts where enterprise clients utilize pre-committed cloud spend budgets—often secured through multi-million dollar enterprise agreements—to acquire third-party software like compliance automation platforms.
This financial engineering allows Chief Information Security Officers to bypass traditional capital expenditure approvals, routing the software acquisition through existing cloud consumption commitments.
Furthermore, joint go-to-market motions with cloud architects and account executives ensure that compliance automation is introduced at the exact moment an enterprise migrates critical workloads to the cloud. When a financial institution or healthcare provider spins up a new environment within a major hyperscaler, cloud sales representatives actively recommend integrated security and compliance tooling to mitigate migration risks.
As Sprinto scales its automated compliance framework for modern enterprises, operational visibility becomes critical for sustainable growth. By leveraging brilliant flyx.cloud product features insights , teams illuminate hidden digital workflows with striking clarity and precision. This seamless integration ultimately empowers the robust Sprinto architecture to deliver unprecedented security assurance and unwavering market trust.
Co-selling with cloud infrastructure titans transforms a standalone software vendor into an essential native extension of the cloud computing stack, collapsing months of vendor vetting into a matter of days.
By tapping into the co-op funds, joint engineering resources, and field-level alignment of these tech monoliths, compliance platforms achieve unprecedented enterprise velocity and market penetration.
Strategic alliance criteria for channel partner recruitment
Establishing a robust and productive channel ecosystem in the cybersecurity domain requires rigorous filtering and deliberate partner selection to ensure long-term value creation and brand protection. Organizations must evaluate prospective channel allies against stringent operational benchmarks to avoid dilution of market positioning and to guarantee technical competence.
- Demonstrated technical proficiency and active certifications in relevant regulatory frameworks such as SOC 2, ISO 27001, GDPR, and HIPAA.
- Established client base consisting of mid-market to Fortune 1000 enterprises with a high propensity for digital transformation and cloud migration.
- Cultural alignment regarding data privacy, zero-trust security postures, and a commitment to continuous compliance methodologies over point-in-time audits.
- Dedicated practice units or specialized personnel capable of providing first-tier technical support and advisory services to end customers.
- Proven willingness to invest in joint marketing initiatives, sales enablement training, and co-selling key performance indicators.
Referral dynamics and enterprise advocacy networks
Harnessing the advocacy of existing enterprise clients remains one of the most cost-effective and high-converting distribution strategies available in the B2B SaaS playbook. When a multinational corporation successfully automates its compliance posture, reducing audit preparation times by seventy percent and eliminating millions in potential risk, the executives driving that transformation naturally share their success within industry peer groups. Modern compliance automation platforms institutionalize these organic conversations by engineering structured referral and advocacy programs that reward enterprise champions for publicly or privately endorsing the technology.
These referral dynamics operate on a foundation of professional reputation and peer-to-peer trust within specialized industry networks, ranging from FinTech associations to healthcare compliance roundtables. When a Chief Information Security Officer at a prominent digital bank speaks on a panel detailing how automated continuous monitoring saved their team from compliance burnout, the resulting inbound interest carries vastly more weight than any traditional marketing campaign.
To accelerate this advocacy, platforms frequently deploy executive advisory boards, customer-led user conferences, and reciprocal referral incentives that grant tier-one clients early access to advanced AI-driven remediation features. This turns satisfied enterprise users into vocal stakeholders who actively pull new logos into the ecosystem, ensuring durable, compounding market capture.
Dissecting the customer success frameworks designed to maximize long term retention and platform expansion
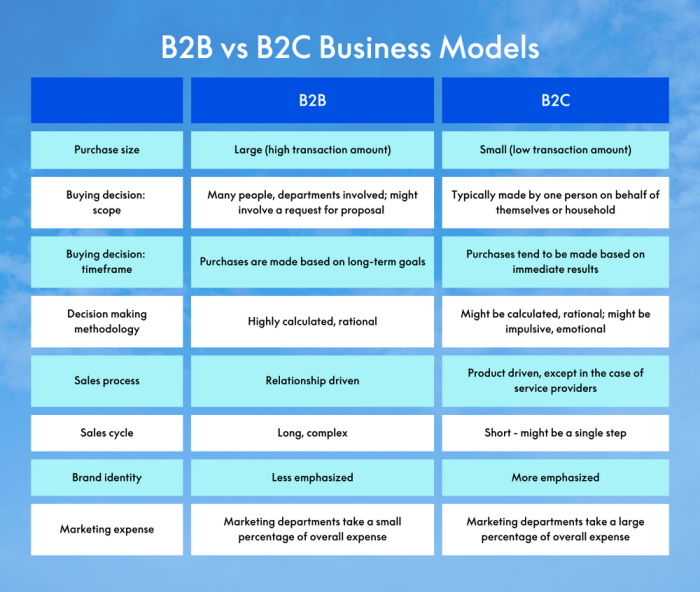
Source: openeye.partners
In the high-stakes arena of enterprise compliance automation, securing the initial signature is merely the opening gambit in a much larger chess match. The true battleground for sustainable profitability lies within the customer success engine, where long-term retention and account expansion are systematically engineered. As modern enterprises grapple with increasingly complex regulatory landscapes, the organizations providing the underlying infrastructure must transition from reactive software vendors to indispensable strategic partners.
This operational metamorphosis requires a meticulous blend of velocity, predictive analytics, and structural alignment to ensure that compliance transforms from a corporate headache into an enduring competitive advantage.
When an enterprise organization commits to a continuous compliance platform, the clock immediately starts ticking on their perception of value. The earliest interactions with the platform set the psychological anchor for the entire commercial relationship, directly influencing whether the account becomes a stagnant contract or a hyper-expanding powerhouse.
The velocity of initial onboarding and its impact on account lifetime value
The speed at which a newly onboarded enterprise account integrates its cloud infrastructure and achieves its first successful audit control mapping directly dictates its ultimate lifetime value. In the world of automated compliance, time-to-value is the absolute north star metric; every single day a security team spends wrestling with credential integration or policy mapping is a day closer to buyer remorse and eventual churn.
Rapid onboarding bypasses the hazardous valley of despair where implementation projects typically stall and lose executive sponsorship. When a company can ingest hundreds of cloud resources, map them against frameworks like SOC 2 or ISO 27001, and generate pristine evidence within days rather than months, a profound psychological shift occurs across the client organization. Trust solidifies, internal champions are validated in front of their boardrooms, and the platform becomes deeply embedded in the daily operational muscle memory of engineering and security teams.
Furthermore, compressed time-to-value dramatically accelerates the amortization of customer acquisition costs, immediately steering the account into net-positive territory. This velocity is achieved not by cutting corners, but through highly structured, automated discovery playbooks that remove cognitive friction and manual data entry. By orchestrating a seamless first mile, platforms establish an unshakeable foundation of reliance, turning standard software users into vocal advocates who champion broader enterprise deployment and multi-year contract renewals without hesitation.
Rapid time-to-value acts as the single greatest compounding interest mechanism for net revenue retention in enterprise software ecosystems.
Predictive health scoring methodologies for proactive churn mitigation
Waiting for a customer to formally express dissatisfaction or submit a cancellation request is a catastrophic failure of modern account management. Sophisticated compliance platforms deploy dynamic, multi-variable health scoring algorithms that ingest telemetry data to identify the faint heartbeat anomalies signaling potential churn long before it actually materializes. These predictive models synthesize quantitative usage metrics—such as daily active logins, API error frequencies, evidence collection velocity, and framework coverage expansion—with qualitative signals like support ticket sentiment and executive sponsor engagement.
For instance, if an enterprise client suddenly experiences a sharp decline in evidence collection frequency or a spike in unresolved integration warnings, the algorithm automatically flags the account as high-risk. This triggers an immediate, cross-functional intervention playbook that deploys technical account managers to audit cloud connector integrity and re-engage dormant stakeholders. By shifting from a lagging indicator framework to a real-time predictive posture, customer success teams can surgically address friction points, restore platform confidence, and protect high-value revenue streams before financial stakeholders ever initiate renewal reviews.
The operational rhythm of mitigating churn and driving expansion relies heavily on a structured matrix of interventions, cross-departmental accountability, and rigorous metric tracking. The following overview maps out the strategic milestones required to safeguard enterprise accounts throughout their lifecycle.
| Customer Success Milestone | Intervention Strategy | Responsible Internal Teams | Targeted Retention Metrics |
|---|---|---|---|
| Initial Cloud Integration | Automated white-glove setup sessions and real-time connector diagnostics to eliminate friction. | Implementation Engineering & Support | Time-to-first-evidence under 7 business days |
| Mid-Cycle Utilization Dip | Proactive technical health check and customized refresher training for core security leads. | Customer Success & Technical Account Management | 95% daily active user stability week-over-week |
| Secondary Framework Adoption | Strategic compliance roadmap workshop highlighting automated cross-mapping efficiencies. | Account Management & Product Specialists | Minimum 30% expansion in annual contract value |
| Renewal Window Preparation | Executive business review showcasing risk reduction ROI and audit cost savings metrics. | Executive Leadership & Customer Success | 120% net revenue retention and zero churn rate |
Expansion protocols for growing cloud footprints and secondary regulatory frameworks
As enterprise clients naturally scale their digital operations, their compliance surface area expands in tandem, creating organic pathways for platform revenue growth. Modern compliance infrastructure is architected to detect these expansion triggers automatically, transforming routine technical milestones into lucrative commercial opportunities. When an engineering division spins up new multi-cloud environments or deploys containerized microservices across international regions, the platform immediately identifies the unmonitored assets and prompts the account team with a contextual expansion proposal.
Similarly, when a company decides to scale its market reach by pursuing secondary regulatory certifications like HIPAA, GDPR, or FedRAMP, the existing compliance repository serves as a powerful operational springboard. Because the foundational infrastructure and core evidence are already continuously monitored, adding a new standard requires only fractional effort compared to initial deployment. Account expansion procedures leverage this structural efficiency, utilizing automated gap analyses to demonstrate how existing controls satisfy up to sixty percent of the requirements for new secondary frameworks.
This compelling value proposition is presented through automated executive dashboards that quantify the immense cost savings of leveraging a single pane of glass versus adopting disparate point solutions. Consequently, the commercial expansion process feels less like a traditional sales pitch and more like a natural, highly efficient evolution of the client’s own risk management strategy, locking in long-term enterprise commitment.
Evaluating the defensibility moats and technological barriers protecting market positioning against emerging competitors: Sprinto B2b Business Model
The modern landscape of automated compliance is unforgiving, where staying ahead requires more than just functional software—it demands impenetrable barriers to entry. As the market matures, the battleground shifts from basic feature sets to deep structural advantages that protect market share from agile newcomers and entrenched legacy players alike. Building a lasting enterprise fortress involves a calculated orchestration of proprietary intelligence, deep technical integration, and relentless internal validation.
In the high-stakes arena of continuous security operations, survival depends on the ability to transform daily operational friction into an unassailable strategic advantage. Enterprises do not merely purchase a tool; they entrust their entire regulatory posture to an underlying engine. Consequently, the durability of a compliance automation platform is measured by how deeply its roots penetrate the client’s infrastructure and how effectively its proprietary mechanisms block copycat infiltration.
Proprietary data moats formed by aggregating continuous audit telemetry across diverse industries
At the bleeding edge of compliance automation, the true currency is not just software code, but the vast oceans of telemetry continuously harvested from thousands of heterogeneous cloud environments, SaaS applications, and developer pipelines. Every automated check, every remediated misconfiguration, and every successfully neutralized cloud drift across fintech, healthcare, and enterprise software feeds a colossal, centralized machine learning flywheel. This constant ingestion of real-time audit telemetry creates a proprietary data moat that newly minted competitors simply cannot replicate overnight, no matter how much venture capital they deploy.
Consider the sheer volume of telemetry generated when monitoring identity and access management policies, Kubernetes clusters, and multi-cloud storage buckets simultaneously for thousands of global organizations. A new entrant starting from scratch lacks this historical, cross-industry dataset, meaning their automated recommendations operate with a fraction of the contextual accuracy. As the platform processes millions of daily evidence-gathering events, its anomaly detection algorithms become increasingly razor-sharp, predicting audit failures before they manifest as critical vulnerabilities.
This creates a compounding intelligence loop: more enterprise customers yield richer telemetry, which in turn delivers superior automated mapping, leaving competitors perpetually chasing a moving target.
Intellectual property surrounding automated policy mapping creating high switching costs, Sprinto b2b business model
The architecture of modern regulatory frameworks requires translating thousands of dense, often ambiguous regulatory clauses—such as SOC 2, ISO 27001, HIPAA, and GDPR—into granular, machine-readable technical controls. The intellectual property concentrated within automated policy mapping engines acts as a formidable anchor, binding enterprise clients to the platform through insurmountable switching costs. When a company spends months refining custom control mappings, automated asset tagging, and proprietary remediation workflows tailored to its specific organizational hierarchy, migrating to an alternative vendor introduces catastrophic operational downtime and unacceptable compliance gaps.
The transition friction is intentionally magnified by the intricate web of dependencies woven between raw cloud infrastructure and specific compliance frameworks. For instance, mapping a single AWS IAM policy requirement across four different regulatory standards simultaneously involves complex algorithmic logic that takes years of engineering refinement to perfect. Once an enterprise integrates this mapping layer deeply into its daily software development life cycle, pulling out that infrastructure is akin to performing open-heart surgery while running a marathon.
The sheer risk of audit failure during a migration cycle forces risk-averse enterprise procurement committees to renew existing contracts rather than gamble on unproven alternatives.
Rigorous compliance accreditations maintained internally to prove trustworthiness
Selling automated trust means living in a perpetual glass house where internal security postures are subjected to the exact same merciless scrutiny demanded of enterprise clients. To convince Fortune 500 CISOs and rigorous procurement teams that the platform is worthy of deep system-level integration, the vendor must maintain a flawless and expanding portfolio of elite internal security accreditations. These credentials serve as the ultimate baseline proof of operational integrity, demonstrating that the guardian of the compliance infrastructure is itself fortified against sophisticated cyber threats.
To maintain market leadership, the organization continuously undergoes rigorous third-party audits, securing and maintaining a robust suite of elite security verifications. The verification framework requires a multi-layered validation strategy to eliminate any shadow of doubt among enterprise buyers:
- SOC 2 Type II attestation covering security, availability, and confidentiality trust services criteria evaluated over continuous observation windows.
- ISO/IEC 27001, 27701, and 27017 certifications ensuring international standards for information security management and cloud privacy.
- FedRAMP or StateRAMP authorizations, enabling secure deployment within highly regulated government and public sector ecosystems.
- Regular, unannounced red-team penetrative testing conducted by elite external cybersecurity firms, with executive summaries published transparently for prospective enterprise buyers.
Defensive strategies deployed to counter copycat features introduced by legacy governance software vendors
Legacy governance, risk, and compliance vendors often attempt to mask their architectural obsolescence by hastily bolting on surface-level automation features to match modern market demands. To neutralize these superficial mimicry attempts, market leaders execute a series of multi-layered defensive strategies designed to emphasize the vast gap between superficial wrappers and native, API-driven continuous compliance engines.
The strategic blueprint focuses on out-executing imitators by entrenching the platform deeper into the enterprise ecosystem, utilizing specific operational countermeasures:
- Accelerating the velocity of native API integrations with emerging developer tools and niche enterprise software, rendering static legacy connectors instantly outdated.
- Deepening the granularity of automated evidence collection down to the individual line-of-code and container level, far beyond the manual document uploads typical of legacy platforms.
- Fostering an expansive, developer-first ecosystem with open SDKs that allow enterprise engineering teams to build custom compliance checks directly into the platform’s core engine.
- Deploying predictive, AI-driven compliance forecasting models that shift enterprise risk management from a reactive audit-prep exercise to a proactive, real-time operational posture.
True enterprise defensibility is not achieved by locking doors, but by building an intelligent ecosystem so deeply integrated into daily operations that leaving becomes an operational impossibility.
Last Recap
The journey through the mechanics of continuous compliance reveals a powerful truth about modern enterprise growth, where automated precision meets unyielding strategic vision. By neutralizing operational friction and championing proactive customer success, platforms like this do not merely protect data—they liberate organizational potential and pave the way for a remarkably secure, prosperous digital horizon.
