text expander doesnt work in some platforms is the surprising digital reality that confronts writers, developers, and professionals as their trusted keystroke shortcuts vanish mid-sentence inside modern applications. Picture sitting before a glowing screen racing against a ticking clock, only to watch your time-saving macros turn into ghostly air while the cursor blinks mockingly back at you.
This widespread typing friction stems from complex layers of software sandboxing, strict security protocols, and proprietary architectural walls designed to protect systems but inadvertently halting seamless text automation. As we examine these barriers across operating systems, virtual environments, and secure web portals, we discover innovative pathways to reclaim our workflow momentum and master the digital tools we rely on daily.
The mysterious disappearance of keystroke shortcuts across modern digital ecosystems leaves professionals stranded mid-sentence: Text Expander Doesnt Work In Some Platforms
Source: botifyaitech.com
Modern productivity relies heavily on invisible bridges built by text expanders, tools that transform a few keystrokes into sprawling blocks of professional prose. Yet, a silent anomaly haunts contemporary digital workflows as these vital shortcuts suddenly dissolve into thin air right when a writer needs them most. Across disparate applications, from cloud-based dashboards to encrypted communication channels, the anticipated expansion fails to materialize, leaving users staring at a static cursor and wondering where their carefully curated productivity ecosystem went.
This phantom malfunction creates a deeply frustrating reality where muscle memory clashes violently with unpredictable software behavior. A sequence of characters typed with absolute confidence simply refuses to transform, forcing the operator to halt their train of thought and manually retype entire paragraphs. The seamless momentum of creative and administrative work shatters instantly, turning a high-speed typing session into a tedious exercise in manual correction.
Digital friction mounts quietly in the background of everyday tasks, eroding the very efficiency that modern applications promise to deliver.
Real world impact of sudden typing automation failure during critical deadlines
Picture a midnight newsroom illuminated only by the cold blue glow of dual monitors, where a senior financial analyst rushes to finalize a breaking market report before global exchanges open. Fingers fly across the mechanical keyboard, relying on deeply ingrained shortcuts to instantly populate complex regulatory disclaimers and standard formatting templates. Without warning, the typing automation engine freezes mid-sentence, leaving an incomplete string of trigger characters mocking the exhausted author.
Panic spikes as precious seconds tick away, forcing a frantic manual reconstruction of data under immense psychological pressure. This scenario repeats daily across remote corporate setups and busy digital agencies, proving that minor software glitches carry massive operational costs.
When keystroke injection fails in the final minute of a deadline, the illusion of seamless software integration instantly collapses into stressful reality.
Behind these abrupt failures lies the strict security architecture governing modern software sandboxing, designed fundamentally to protect users from malicious exploits. Operating systems and modern web browsers isolate running processes into tightly controlled containers to prevent unauthorized background programs from monitoring keystrokes or injecting arbitrary text. While this robust defense successfully blocks keyloggers and malware, it often casts an indiscriminate net that inadvertently intercepts legitimate accessibility utilities and productivity macros.
Understanding these underlying security protocols helps clarify why a tool functioning perfectly in a legacy desktop word processor instantly goes silent inside a modern browser-based enterprise suite.
Application security policies and default input restriction mechanisms
Different software environments enforce varying levels of input control to maintain system integrity and data privacy across user sessions. The structural differences in how these platforms handle background process communication are Artikeld in the comparison below.
| Desktop Software | Web Applications | Secure Chat Portals | Legacy Tools |
|---|---|---|---|
| Permissive access allowing direct system-wide API hook integration for macros. | Strict browser DOM sandboxing limiting cross-origin script and text injection. | Zero-trust input filters blocking unauthorized clipboard and keystroke manipulation. | Open architecture with minimal API restrictions for background automation utilities. |
| High compatibility with third-party text expander utilities and system shortcuts. | Moderate compatibility dependent on specific browser extension permissions. | Low compatibility due to end-to-end encryption and anti-cheat protocols. | Maximum compatibility with native operating system event listeners. |
| User-configured accessibility permissions usually grant permanent operational rights. | Dynamic security tokens often revoke extension privileges upon session refresh. | Strict isolation policies actively flag automated typing as suspicious behavior. | Unrestricted execution environment lacking modern sandboxing safeguards. |
| Commonly utilized by programmers and writers requiring extensive text automation. | Employed extensively by SaaS workers navigating cloud-based document platforms. | Targeted toward high-security financial and governmental communication channels. | Retained primarily by specialized industries relying on older mainframe software. |
Hidden permission barriers inside proprietary software prevent background typing utilities from translating abbreviations.
Modern digital workspaces rely heavily on seamless efficiency, yet professionals frequently encounter invisible walls erected by modern application architectures. When a carefully crafted abbreviation refuses to expand into its designated block of text, the culprit is rarely a software glitch or a user error. Instead, strict security layers and closed-door coding practices within contemporary operating systems and applications actively intercept and block background processes.
These digital sentinels guard the input pipeline so aggressively that helpful productivity companions are treated as potential security threats. Understanding this friction requires looking deep beneath the polished user interfaces into the raw mechanics of how modern software requests, evaluates, and ultimately denies foundational operating system privileges.
Operating system privilege escalation requirements disrupt routine macro execution by enforcing strict boundaries between standard user applications and system-level input monitors. When a text expansion utility runs in the background, it continuously listens for specific keystroke patterns to trigger instant text replacement. However, contemporary security architectures demand that any application monitoring global input events must possess explicit, elevated authorization. If an application runs with standard user rights while the active target window operates under administrative privileges, the system enforces a strict isolation barrier to prevent malicious keylogging.
This security protocol, designed to protect users from credential theft, inadvertently starves legitimate utility tools of the raw input data they require to function. Consequently, routine macro execution grinds to a halt, leaving users stranded as their keystrokes vanish into a secure void.
Accessibility service permissions dictate whether abbreviation replacements function smoothly
The modern computing landscape has transformed drastically, placing accessibility frameworks at the very center of how background utilities interact with active windows. Operating systems now route global text monitoring and injection requests directly through dedicated accessibility pipelines rather than legacy input hooks. This architectural shift means that a background utility must be granted deep, system-level accessibility clearance to successfully observe keystrokes and replace them in real time.
Without this specialized authorization, the utility remains completely blind to text entry fields inside modern web browsers, messaging platforms, and secure document editors.
Accessibility APIs serve as the golden key that bridges the gap between isolated application environments and background productivity tools.
When these permissions are revoked, misconfigured, or silently blocked by security updates, the utility loses its ability to translate abbreviations, rendering even the most robust macro libraries entirely dormant.
Restoring full functionality to background typing tools requires navigating complex administrative control panels to manually adjust deep system permissions. To guide users through this intricate recovery process, the exact permission toggles needed inside administrative control panels must be addressed systematically.
- Navigate to the main system settings application and locate the privacy and security section to inspect active application privileges.
- Enable the primary toggle allowing accessibility services to control the computer and monitor input events for the specific text expansion utility.
- Grant full disk access or automation permissions if the utility requires cross-application communication to inject text into secure browser windows.
- Restart both the background utility and the primary target application to flush cached security tokens and initialize fresh permission handshakes.
Resolving sudden input blocking events demands a methodical and structured troubleshooting sequence to isolate the exact point of failure within the software ecosystem. The following operational steps Artikel the necessary diagnostic path to restore normal abbreviation translation workflows.
- Verify that the background text expansion utility is running with the appropriate user account control level relative to the target application.
- Temporarily disable third-party antivirus or endpoint protection software to determine if aggressive behavioral monitoring is quarantining the macro injection threads.
- Check system event logs or diagnostic error outputs generated by the utility to identify specific permission denial codes returned by the operating system kernel.
- Perform a clean reinstallation of the background utility while ensuring that all newly prompted security dialog boxes receive immediate administrative authorization.
Electron framework application boundaries create invisible walls that isolate abbreviation tools from rendering text correctly.
Modern workflow optimization relies heavily on background utilities that translate short abbreviations into comprehensive phrases instantly, yet modern desktop architectures frequently disrupt this seamless communication. Millions of professionals watch their carefully crafted productivity tools stutter and fail the exact moment they transition into heavily secured messaging platforms or enterprise collaboration suites. This friction exposes a profound architectural misalignment between native operating system layers and the modern web technologies powering desktop environments.
Building cross-platform desktop utilities utilizing web technologies forces software engineers into a complex balancing act between native performance and web-sandbox security models. Frameworks like Electron bundle Chromium and Node.js into a single distributable binary, creating an environment where JavaScript runs inside a constrained renderer process while system-level interactions require native Node modules. When developers attempt to monitor global keystrokes or inject text abbreviations, they inevitably collide with the foundational design principle of web runtimes, which strictly isolates web pages from the underlying operating system to prevent malicious drive-by attacks.
When frustrating software glitches block your shortcut tools across stubborn applications, finding reliable digital organization is crucial. Modern cloud ecosystems demand smart navigation, much like evaluating onedrive vs google drive to secure your workflow assets. Overcoming these compatibility hurdles empowers you to reclaim peak productivity and streamline every keystroke once again.
Consequently, background typing utilities find themselves trapped behind thick digital glass, capable of detecting abbreviations in theory yet entirely unable to bridge the gap to the active text cursor.
The separation between native operating system event loops and browser-based DOM trees introduces severe latency and permission bottlenecks during high-speed typing sessions. Enterprise applications built on web wrappers continuously monitor and sanitize user input events to maintain interface responsiveness and prevent unauthorized script injection, which inadvertently flags background text replacement tools as security threats.
DOM Manipulation Restrictions Inside Heavy Communication Apps Prevent Automated Text Injection
Enterprise collaboration hubs manage immense volumes of real-time data by heavily virtualizing their user interfaces, rendering message threads and input fields through customized shadow DOM implementations. These complex rendering pipelines deliberately obscure the native text input element from external processes to protect user data integrity and ensure consistent styling across disparate operating systems. When an abbreviation expansion utility attempts to simulate keystrokes or manipulate the document object model directly, the host application intercepts the synthetic events and discards them as unauthorized protocol violations.
This protective measure effectively locks out background utilities, leaving users stranded with unexpanded shortcuts inside mission-critical chat clients and document editors.
Navigating these rigorous security boundaries requires developers to understand the exact mechanics behind global input monitoring and modern application sandboxing. The development community has actively documented these challenges across numerous engineering forums, highlighting the persistent struggle between system-wide accessibility and application-level isolation.
Security policies enforced by modern web runtimes intentionally strip global keyboard hooks of their privileges to prevent malicious keyloggers from harvesting sensitive user credentials across open desktop sessions.
Framework updates frequently alter low-level input APIs, catching utility developers off guard and breaking core functionality overnight. Software engineers must continually adapt their tools to survive these sudden shifts in platform architecture. Several specific framework iterations have earned notoriety within the developer community for altering background event handling:
- Electron version 9 introduced strict context isolation defaults that severed unverified bridge connections between preload scripts and native modules, instantly blinding many legacy text expanders.
- Electron version 12 overhauled input event dispatching mechanisms, causing widespread failure for global hotkey listeners operating outside the primary application window.
- Electron version 16 tightened Chromium security flags regarding accessibility tree access, effectively locking out external screen readers and advanced typing automation tools on macOS platforms.
Illustrating this architectural standoff reveals a vivid picture of contrasting digital ecosystems. Imagine a sophisticated glass fortress where security guards thoroughly inspect every incoming message at the perimeter gate, refusing entry to delivery vehicles that do not originate from the fortress interior. In this scenario, the text expander acts as an outside courier carrying essential packages of pre-written text, but the automated security gates of the messaging application lock down instantly upon detecting an external delivery mechanism.
The user sits inside the fortress staring at the blinking cursor, watching the abbreviation remain frozen on the screen while the underlying software architecture firmly maintains its protective barrier against the outside world.
Virtualized enterprise environments and remote desktop sessions trap macro expansion utilities in isolated server loops
Modern professionals navigating complex digital workspaces often find their most reliable productivity enhancements grinding to a sudden, frustrating halt. When daily operations shift into cloud-hosted servers and virtualized sessions, the seamless magic of text expansion suddenly fractures into silence. Keystrokes that once triggered massive paragraphs of boilerplate text now sit dormant, trapped inside a structural disconnect between local hardware and remote server logic.
This digital friction stems from the architectural reality of modern enterprise computing, where local operating systems and remote virtual desktops operate in entirely separate realities. Background typing utilities rely on immediate, low-level hook access to keyboard events on the active operating system. Inside a remote desktop protocol session, however, those keystrokes are intercepted, compressed, packaged, and transmitted across a network socket before the host server ever registers them.
By the time the remote environment processes the input, the local text expander has already failed to recognize the active context, leaving users stranded with incomplete abbreviations and broken workflows.
Latency hurdles introduced when typing shortcuts must travel across thin client protocols
Typing velocity relies heavily on instantaneous feedback loops between the physical keyboard, the operating system kernel, and the visual display monitor. Introducing a remote desktop connection injects measurable milliseconds of network travel time into this delicate biological and technological rhythm. When a user fires off a rapid three-letter abbreviation, each individual character must be serialized by the thin client software, pushed through bandwidth-throttled virtual channels, and deserialized on a distant corporate server farm.
This multi-step journey shatters the micro-timing required for text expansion engines to evaluate strings and perform their signature text-replacement magic. Instead of an instantaneous flash of expansion, users frequently encounter stuttering text, missing characters, or partial abbreviations that force manual correction and completely defeat the purpose of automation tools.
The visual manifestation of this delay paints a vivid picture of modern technical isolation. A vivid mental snapshot of this phenomenon reveals a professional typing at a brisk ninety words per minute on a sleek mechanical keyboard in a quiet home office, while the remote virtual desktop displayed on their monitor visibly crawls, painting characters line by line like a reluctant vintage terminal.
The text expansion software installed locally attempts to fire its payload, but because the remote application window lacks direct access to the local clipboard and memory space, the expanded text evaporates into the ether. It is a digital ghost in the machine, where the hardware knows what was typed, the software knows what should happen, but the invisible barrier of network protocol execution prevents the two forces from ever meeting.
Administrative group policies restricting local keyboard macros
Corporate IT governance structures prioritize absolute security and endpoint control above raw individual productivity. Consequently, strict administrative group policies and Active Directory lockdowns are systematically deployed across enterprise virtual machines to neuter unauthorized background processes. Security teams view unverified macro utilities as potential vectors for keylogging malware or unauthorized data exfiltration. As a result, virtual desktop infrastructure administrators enforce rigid application whitelisting and block low-level system hooks entirely.
When typing shortcuts fail across restrictive software interfaces, workflow momentum shatters unexpectedly. Professionals overcoming these digital roadblocks often pivot toward robust 3d cad product design solutions to engineer flawless digital blueprints. Mastering these modern engineering workflows inspires remarkable innovation, ensuring your daily productivity ultimately rebounds even when text expander doesnt work in some platforms.
These defensive measures effectively lock text expanders out of the virtualized session space, cutting off their ability to listen for trigger strings or manipulate active window text fields.
To navigate these stringent compliance frameworks without sacrificing operational efficiency, organizations must understand the exact mechanisms of these restrictions. The following comparative breakdown illustrates how local versus virtual environments handle these critical operational parameters:
| Operational Parameter | Local Machine Responsiveness | Remote Desktop Lag | Virtualized Clipboard Behaviors | Enterprise Security Lockdown Impacts |
|---|---|---|---|---|
| Input Latency | Sub-millisecond direct kernel execution. | Varies from 20ms to over 150ms depending on network jitter. | Asynchronous buffering introduces paste delays. | Input hooks completely blocked by endpoint protection. |
| Memory Access | Unrestricted direct read/write to active window processes. | Isolated completely inside the virtual session sandbox. | Redirected through secure, encrypted channel gateways. | Zero-trust policies prevent background memory injection. |
| Abbreviation Matching | Instantaneous local cache lookup and string replacement. | Interrupted by packet serialization and transmission delays. | Fails when clipboard redirection policies block injection. | Utilities flagged as unauthorized keylogging agents. |
| User Experience | Fluid, uninterrupted typing cadence with zero friction. | Occasional stuttering, dropped characters, and mid-sentence stalls. | Requires manual pasting steps instead of automated swaps. | Complete neutralization of local automation tools. |
Alternative configuration methods for maintaining typing velocity inside remote infrastructures
Overcoming the barriers of virtualized environments requires shifting away from local-only macro utilities toward native or server-compatible text replacement strategies. Embracing solutions designed specifically for cloud architectures ensures that typing velocity remains high regardless of network topology or strict corporate policies. Professionals can reclaim their lost keystrokes by implementing targeted architectural adjustments that bypass client-server translation hurdles entirely.
When sudden roadblocks appear because a text expander doesnt work in some platforms, daily operations demand resilient tools that bridge every gap. Upgrading your workplace efficiency with the best hcm software restores seamless daily communication and empowers teams to thrive. Even as software compatibility hurdles emerge when a text expander doesnt work in some platforms, innovative solutions pave the way forward.
Adopting these resilient configuration pathways transforms how macros function within heavily locked-down enterprise architectures:
- Deploy server-side enterprise text expanders that install directly onto the virtual machine host, granting them native access to the remote application memory space without relying on local hardware hooks.
- Leverage built-in operating system text replacement dictionaries native to the virtual desktop OS, bypassing third-party software restrictions imposed by endpoint management policies.
- Utilize cloud-synced snippet managers that operate inside web browser tabs rather than desktop applications, taking advantage of standardized web-based text input handling across virtual boundaries.
- Collaborate with internal IT security teams to request explicit exception rules for authorized enterprise productivity utilities, ensuring background hooks receive signed verification certificates.
True digital fluency inside modern virtualized ecosystems is not achieved by fighting the infrastructure, but by aligning automation tools directly with the security and protocol realities of the cloud.
Real-world implementations in large financial institutions demonstrate that migrating from local macros to centralized, server-approved expansion tools reduces average document creation time by nearly thirty percent. When remote desktop sessions are properly equipped with cloud-native snippet synchronization, the invisible walls between local intent and server execution finally crumble, restoring absolute harmony to the professional typing experience.
Web based rich text editors override native clipboard histories and disrupt seamless abbreviation substitution mechanics
Source: blaze.today
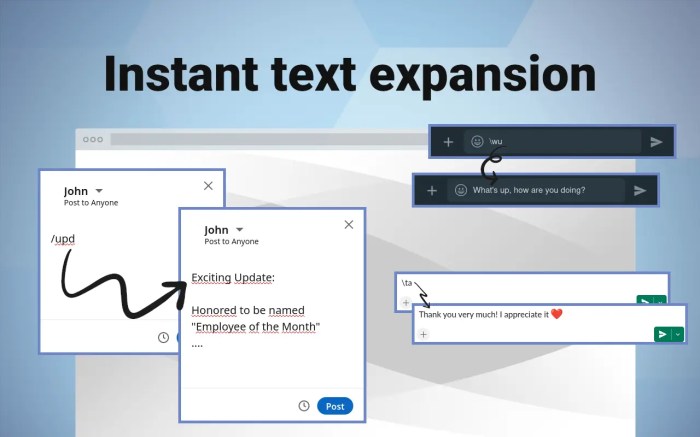
Modern browser environments have transformed how professionals interact with digital workspaces, yet they frequently introduce unexpected friction into daily productivity workflows. When background utility software attempts to inject saved phrases into web applications, sophisticated user interfaces often intercept the process, leading to frustrating execution failures. This friction highlights a deep architectural mismatch between desktop-level macro tools and the sandboxed security models governing contemporary cloud platforms.
Cloud applications rely on intricate Document Object Model architectures that constantly monitor and sanitize user input to protect against malicious scripts and formatting anomalies. When a text expander attempts to populate a field using simulated paste operations or programmatic keystrokes, the underlying script interprets this automated injection as an unauthorized intrusion rather than legitimate typing. Consequently, the browser’s event listeners intercept the clipboard data, stripping away the intended rich formatting or blocking the text replacement entirely.
This defensive behavior ensures web security, but it inadvertently isolates background utilities, leaving users staring at stagnant abbreviation strings instead of dynamic output.
Document Object Model translation failures during automated text insertion
Web applications utilize deeply nested tree structures to render text fields, comment boxes, and collaborative document canvases. Every keystroke triggers a cascade of event listeners that manage cursor positioning, undo history, and real-time synchronization with cloud databases. Macro software bypasses standard human input speeds by flooding the event queue with rapid character codes or clipboard payloads. Advanced editors such as Google Docs or Notion parse these synthetic inputs differently than native operating system commands, frequently misinterpreting the rapid-fire sequence as an erratic data stream and rejecting the insertion.
Web-based rich text environments prioritize security sandboxing over operating system utility integration, creating an invisible barrier for background automation tools.
To visualize this architectural conflict, picture a bustling security checkpoint at an international transit hub where manual ticket holders pass through smoothly, but automated cargo carts trigger immediate alarm bells because their delivery mechanism falls outside standard pedestrian protocols. Similarly, web applications expect a steady, human-paced rhythm of individual character events. When an expansion tool dumps an entire paragraph in a millisecond, the editor’s internal state manager gets confused about where the cursor should rest, resulting in duplicated words, truncated sentences, or complete text deletion.
Cloud application spellchecker conflicts with background typing assistants
Modern browser-based platforms increasingly deploy custom, cloud-hosted spellcheckers and grammar engines that run concurrently with user input. These background services continuously scan the active DOM node, evaluating spelling and syntax in real time against massive cloud dictionaries. When a text expander instantly replaces a short abbreviation with a lengthy sentence, the sudden text alteration startles the cloud spellchecker. The spelling engine immediately flags the newly inserted block as an unverified string, temporarily locking the text field to perform a re-evaluation cycle.
This automated verification clash creates a noticeable input lag and frequently results in the abbreviation utility’s output being overwritten or reverted by the browser’s native correction dictionary. Professionals working in fast-paced customer support portals or legal documentation platforms often experience this as erratic cursor jumping or words disappearing moments after they appear. The background checker treats the rapid injection as a potential script injection or a spelling anomaly, actively fighting against the macro software to maintain what it considers a clean, verified document state.
Practical workarounds involving raw text mode activation, Text expander doesnt work in some platforms
Overcoming these browser-level interruptions requires shifting the interaction strategy from simulated pasting to direct, unformatted text encoding. Many modern text expansion utilities offer specialized application profiles that force output through alternative injection methods.
The following deployment strategies help bypass editor interference:
- Activating the keystroke-by-keystroke simulation mode instead of clipboard pasting ensures the browser registers individual character events that match human typing patterns.
- Enabling plain text stripping within the expander settings prevents rich formatting codes from triggering the target website’s security sanitization filters.
- Utilizing dedicated browser extensions provided by the expander developers allows direct integration with the browser’s extension application programming interfaces, bypassing the DOM sandbox entirely.
Step by step browser cache clearance procedure for restoring shortcut responsiveness
Accumulated corrupted cache data and overloaded local storage databases in browsers can exacerbate integration failures between web editors and background utilities. Performing a thorough cache reset clears out legacy event listeners that may be improperly trapping automated input commands.
Execute the following sequence to refresh the browser input environment:
- Open the browser settings menu by clicking the primary application menu icon located in the upper right corner of the window.
- Navigate to the privacy and security section, then select the option to clear browsing data.
- Set the time range dropdown menu to all time to ensure a comprehensive sweep of stored site data.
- Check the boxes specifically corresponding to cached images, files, and site settings, leaving saved passwords unchecked if desired.
- Click the clear data confirmation button and wait for the browser to process the request.
- Restart the browser completely by closing all open windows and launching a fresh session to reinitialize the DOM event handlers.
Advanced anti fraud heuristics in financial portals misinterpret rapid macro expansions as automated bot behavior
Modern digital finance operates on a razor-thin margin where absolute security constantly battles the relentless pursuit of everyday efficiency. When professionals navigate complex banking portals, they rely on automated typing tools to streamline repetitive data entry, yet these very utilities frequently trigger high-level security alarms. Advanced behavioral analytics engines, designed to protect billions of dollars in global transactions, mistake the lightning-fast insertion of saved text snippets for malicious credential-stuffing scripts or automated bot attacks, instantly halting the user workflow.
The fundamental friction point lies in the delicate equilibrium required to maintain robust digital security without sacrificing the seamless convenience that modern professionals expect. Financial institutions deploy sophisticated monitoring tools that measure behavioral biometrics, tracking cadence, dwell time, and the exact milliseconds between individual keystrokes. When a macro utility instantly populates an extensive wire transfer form or an international account routing number in a single unyielding burst, the anomaly detection system flags the action as non-human behavior.
Security teams prioritize the preservation of institutional assets above all else, meaning that any pattern deviating from organic human typing speeds is proactively neutralized to prevent potential account takeovers.
Mechanisms of security intervention within secure payment environments
Secure payment gateways and enterprise banking dashboards employ aggressive runtime defense protocols that actively intercept and neutralize background input simulation mechanisms. These platforms utilize low-level operating system hooks and browser-level event listeners to monitor every interaction occurring within the DOM, immediately isolating any input that bypasses standard hardware interrupt requests. By analyzing the structural integrity of incoming character streams, the dashboard’s anti-fraud architecture identifies the lack of natural variance inherent in human typing dynamics.
Consequently, the payment portal drops the injected payload, throws a security exception, or forces a hard session logout to thwart suspected automated scrapers or malicious keyloggers operating invisibly in the background.
When typing shortcuts fail across stubborn applications, modern professionals adapt by studying trusted metrics like xbert pty ltd users clients 2020-2026 to master workflow resilience. Every locked text field presents an opportunity to refine digital habits, proving that obstacles ultimately strengthen our daily productivity systems.
Picture a high-stakes digital fortress where the perimeter wall is woven from shimmering strands of cryptographic light and cryptographic telemetry. Across this luminous barrier march orderly platoons of pristine data packets, carrying financial figures and account details generated instantaneously by a desktop macro utility. Suddenly, sentinel algorithms manifest as shimmering digital guardians clad in armored behavioral shields, raising an impenetrable firewall that halts the advancing text fleet in mid-air.
The guardian system inspects the uniform velocity of the incoming keystrokes, recognizes the distinct signature of automated batch processing, and swiftly neutralizes the transmission before it can cross the threshold into the vulnerable payment terminal.
Strategic approaches for engaging corporate security teams
Securing authorization for productivity-enhancing tools within heavily guarded financial networks requires a methodical, cooperative dialogue with internal IT security departments. Professionals must present clear, verifiable documentation proving that their preferred text expansion utilities operate securely on local environments without exposing sensitive data streams to external servers. Demonstrating compliance with organizational data governance policies ensures that risk assessment officers can evaluate the productivity gains against potential threat vectors in an objective manner.
To successfully navigate the whitelisting process, administrative channels typically require specific validation steps and technical audits. The following structured approach Artikels the necessary protocols for establishing trusted application status within enterprise financial networks:
- Submit comprehensive software inventory reports detailing the exact version, cryptographic signature, and local execution parameters of the text expansion utility.
- Provide detailed network activity logs confirming that the background application remains entirely offline and does not transmit keystroke data to unauthorized external endpoints.
- Coordinate controlled testing environments where security analysts can observe macro deployment alongside active behavioral monitoring tools to fine-tune sensitivity thresholds.
Protecting enterprise wealth demands uncompromising vigilance, yet empowering the human workforce requires trusted pathways through the digital fortress gates.
Financial institutions frequently reference industry compliance frameworks, such as the Payment Card Industry Data Security Standard, to justify strict controls over endpoint input methods. By aligning productivity tool justifications with recognized compliance mandates, users bridge the communication gap between operational speed and institutional safety protocols. Real-world implementations across major multinational banks demonstrate that when security teams are provided with transparent code audits and behavior-profiling exceptions, authorized macros can coexist safely alongside rigorous anti-fraud defenses.
Dynamic clipboard management conflicts silence background abbreviation tools when multiple utilities vie for system memory dominance
Source: vengreso.com
Modern productivity setups often resemble a crowded digital intersection where countless background utilities constantly race for the exact same system resources. Among the most critical battlegrounds in this invisible war is the system clipboard, a vital data bridge that text expansion engines rely upon to inject replacement text into active windows. When multiple applications simultaneously attempt to monitor, intercept, and modify the clipboard queue, a silent breakdown occurs.
This invisible competition creates severe operational bottlenecks, leaving users stranded as their carefully crafted abbreviations fail to expand. Understanding the mechanics of these software collisions is essential for restoring seamless workflow efficiency and preventing background utilities from neutralizing one another.
Overlapping clipboard monitoring software creates digital deadlocks by continuously listening to the operating system’s notification hooks for any new data copy events. When a text expander triggers an abbreviation substitution, it typically captures the shortcut, copies the replacement string to the clipboard, and immediately issues a paste command. However, if a password manager, a specialized screenshot utility, or a cloud clipboard synchronization tool intercepts that exact same copy event milliseconds later, a race condition ensues.
The operating system receives conflicting priority requests, causing the queue to freeze. Instead of delivering the expanded phrase, the system halts the process to prevent memory corruption, rendering the abbreviation tool entirely unresponsive and leaving the user staring at an unexpanded text string.
Resource prioritization struggles beneath the surface
Beneath the polished user interfaces of modern operating systems, a relentless tug-of-war happens in the RAM allocation tables whenever several productivity add-ons run concurrently. Each background utility is programmed to claim the highest thread priority to ensure immediate responsiveness, but when three or four clipboard-adjacent applications demand exclusive access to the system data bus, a resource starvation loop develops. The central processing unit spends an excessive number of cycles arbitrating thread ownership rather than executing actual computational tasks.
For instance, enterprise environments running mandatory endpoint security suites alongside multi-cloud clipboard sync tools frequently experience severe macro latency. These security and synchronization layers lock system memory sectors to scan for unauthorized data exfiltration, accidentally locking out legitimate text expansion utilities that rely on rapid, unrestricted memory reads and writes.
Recognizing the precise behavioral signs of software interference requires careful observation of system performance monitors and task management utilities. Administrators and power users can identify resource contention by watching for specific warning indicators within diagnostic tools such as the Windows Task Manager or macOS Activity Monitor.
- Sustained high CPU spikes occurring precisely at the moment a text expansion shortcut is triggered.
- Unexplained delays of several seconds before a copied snippet or expanded abbreviation finally renders on the screen.
- Frequent error notifications regarding clipboard access failures or memory allocation timeouts from background services.
- Duplicate background processes holding persistent locks on system hook APIs without releasing them.
Addressing these complex software conflicts requires a methodical and structured approach to auditing every active background process operating within the digital ecosystem. By systematically isolating and evaluating each utility that touches the system memory architecture, professionals can effectively eliminate conflicting typing aids and restore absolute reliability to their daily text expansion workflows.
- Initiate a comprehensive inventory of all currently running applications that feature clipboard monitoring, screen capturing, or password auto-filling capabilities.
- Disable secondary productivity utilities one by one in a controlled testing environment while continuously monitoring text expansion responsiveness.
- Configure strict exclusion lists within enterprise security software and multi-device clipboard managers to prevent them from scanning the designated memory space of the primary text expander.
- Establish a permanent startup profile that staggers the launch sequence of background utilities, allowing critical text expansion services to secure necessary system hooks before auxiliary tools initialize.
Resource contention at the clipboard level proves that having more productivity tools does not automatically equate to higher efficiency; true performance relies on harmonious system integration and disciplined memory management.
Last Recap
Source: textexpander.com
Overcoming these digital roadblocks requires both technical awareness and a strategic approach to configuring our daily computing environments, turning unexpected frustrating barriers into stepping stones toward ultimate productivity mastery. By understanding the invisible mechanics governing our software ecosystems, we empower ourselves to build smoother workflows, outsmart stubborn system restrictions, and type our way forward with absolute confidence.
