website security dashboard to review gpgaddy opens a vital gateway into the silent guardian systems that shield our modern digital landscapes from unseen perils. Behind the sleek glass of the primary administrative interface lies a meticulously orchestrated command center, where every pixel and widget is intentionally placed to distill overwhelming streams of data into clear, actionable clarity. Administrators navigate this expansive digital domain with steady confidence, watching over vibrant telemetry graphs that pulse like a living heartbeat across the screen, turning complex computational currents into a breathtaking tapestry of absolute defense.
As threats continually evolve in the shadows of the interconnected world, mastering these sophisticated security tools transforms routine oversight into an empowering journey of resilience and growth. Every successfully intercepted intrusion and precisely renewed certificate reinforces the unbreakable bond of trust between platform operators and their valued visitors. By embracing these advanced diagnostic environments, teams step forward into a brighter, more secure future where digital innovation thrives safely under the watchful eyes of intelligent automation and proactive protection.
Navigating the centralized center allows administrators to oversee their digital domain through godaddy
Stepping into the digital command deck feels remarkably like walking onto the bridge of a sleek, high-altitude orbital station where every pixel has a specific purpose. The primary administrative interface greets the eye with a sophisticated obsidian backdrop, purposefully chosen to reduce eye strain during midnight forensic investigations while allowing neon-accented threat indicators to pulse with urgent clarity. This architectural layout merges uncompromising efficiency with a refined aesthetic, arranging critical telemetry into distinct, ergonomically zoned quadrants that guide the human eye naturally from macro-level system stability down to granular packet inspection.
Every margin, padding element, and typography scale has been meticulously calibrated to respect cognitive bandwidth, ensuring that system administrators never feel overwhelmed by the sheer volume of incoming data streams flowing continuously from the vast GoDaddy infrastructure.
The visual landscape employs a fluid grid system that breathes dynamically with the operator’s workflow, placing high-frequency metrics directly within the central field of vision while relegating historical logs and passive audit trails to the peripheral panels. Soft, ambient gradient lighting subtly shifts behind critical modules, casting a gentle amber glow for moderate alerts and a resolute crimson pulse for active intrusion attempts, which immediately captures attention without triggering panic.
This thoughtful spatial distribution transforms hours of routine monitoring into an intuitive, almost tactile experience where fingers dance across responsive glass surfaces and shortcuts trigger instant layout morphs. By harmonizing modern ergonomic principles with robust backend orchestration, the interface bridges the gap between raw, intimidating code outputs and clear, actionable intelligence that empowers swift decision-making across enterprise networks.
Visual layout and ergonomic design of the primary administrative interface
The architectural blueprint of the workspace relies heavily on spatial psychology and human-computer interaction studies to minimize operational fatigue during extended shifts. Divided into three primary zones—the Left Telemetry Column, the Central Command Canvas, and the Right Notification Stream—the interface ensures that no single sector demands excessive eye movement. The typography utilizes a monospace font for raw data strings to maintain absolute alignment, paired with a crisp sans-serif typeface for operational labels, creating a visual hierarchy that speaks with both authority and absolute precision.
Navigating your website security dashboard to review gpgaddy reveals vital digital shields protecting your brand, while scaling operations demands evaluating test.com pricing enterprise plans to unlock powerful growth opportunities for your evolving business enterprise, ensuring you continually monitor your website security dashboard to review gpgaddy and maintain absolute peace of mind.
Subdued borders frame each functional widget, separating live graphs from static configuration menus without introducing visual clutter, thereby maintaining a pristine, distraction-free environment where security professionals can maintain laser focus on evolving threat vectors.
Beyond mere aesthetics, the ergonomic layout incorporates adaptive scaling that dynamically reorganizes modules when an administrator transitions from a multi-monitor desktop command center to a compact field laptop. Color palettes are strictly standardized against strict accessibility guidelines, guaranteeing that critical status distinctions remain instantly recognizable even to operators with varying degrees of color perception. Every interactive element features generous hit targets and micro-animations that confirm actions instantly, replacing frustrating latency with fluid, reassuring feedback loops.
This seamless integration of form and function elevates the daily administrative routine from a chore into a masterclass in digital ergonomics.
Comparative metrics of interface configuration parameters
Understanding how individual components interact requires a structured breakdown of spatial organization, telemetry feeds, and filtering capabilities across the operational grid. The following data matrix Artikels the precise parameters governing widget behavior and alert hierarchies within the active monitoring environment.
| Widget Position | Alert Severity Levels | Telemetry Metrics | Custom Filtering Options |
|---|---|---|---|
| Top-Left Command Quadrant | Critical / P1 (Immediate Action Required) | CPU Load, Memory Saturation, Active DDoS Vectors | IP Subnet, Geo-Location, Protocol Type |
| Top-Right Feed Matrix | High / P2 (Warning State Monitored) | SSL Certificate Expiry, Firewall Drop Rates | Time-Window Slider, Severity Thresholds |
| Lower-Center Analytics Hub | Medium / P3 (Informational Notice) | Bandwidth Consumption, Latency Spikes | Service Tags, Departmental Chargebacks |
| Bottom-Dock Ledger | Low / P4 (Routine Audit Trail) | Successful Logins, Backup Verification Status | User ID, Authentication Method, Timestamp |
Procedures for rearranging interface modules to prioritize urgent threat notifications
When an active security incident unfolds, standard dashboard configurations must transform instantly to bring high-priority threat feeds into sharp focus. Operators can execute this layout mutation seamlessly through a standardized series of deliberate actions designed to eliminate operational friction during high-stress scenarios.
- Activate the layout customization mode by selecting the master grid lock icon located in the upper-right navigation toolbar, which instantly superimposes a delicate dotted matrix across the entire viewport.
- Click and hold the header of the primary threat telemetry module, dragging the entire container from its default secondary position directly into the upper-left primary focal zone.
- Release the mouse button to snap the module into its new home, prompting adjacent widgets to automatically reflow and resize themselves fluidly into the remaining peripheral spaces without data loss.
- Apply an instantaneous priority filter preset by clicking the emergency profile toggle at the base of the screen, which instantly collapses non-essential audit logs and magnifies active intrusion detection graphs by two hundred percent.
- Lock the newly configured tactical layout by pressing the master commit shortcut, securing the optimized command arrangement for the duration of the active incident response lifecycle.
Following these precise steps ensures that every second spent interacting with the interface contributes directly to mitigation speed rather than navigation confusion. The system retains these customized layout profiles in local cache memory, allowing operators to recall specialized emergency views with a single keystroke whenever threat indicators breach pre-configured tolerance thresholds.
Operator monitoring scenario for multi-server health without cognitive overload
Picture a seasoned senior systems engineer managing a sprawling cluster of virtualized web properties hosted across distributed GoDaddy infrastructure during a massive global product launch. Instead of frantically toggling between dozens of isolated browser tabs and text-based terminal windows, the operator sits calmly before a curved panoramic display partitioned into harmonious visual streams. The central viewport displays a consolidated health constellation where each server is represented by a pulsing node; green nodes indicate optimal performance, while a sudden shift to a steady, rhythmic amber glow over a cluster of three database nodes immediately draws the eye without blaring obnoxious sirens.
Surrounding this constellation, secondary widgets quietly stream real-time throughput metrics and memory utilization curves, filtered intelligently to display only anomalies deviating by more than two standard deviations from the historical baseline. This elegant abstraction shields the operator from millions of routine, uninteresting log entries, allowing their human intellect to focus entirely on contextual reasoning and strategic intervention.
Operational clarity is achieved not by displaying more data, but by surfacing the right intelligence at the exact moment human intuition is required to act.
As traffic surges toward peak levels, the interface dynamically adjusts its contrast ratios, softening non-critical background metrics while sharpening the visual fidelity of the affected database cluster. The operator effortlessly reviews aggregated error logs summarized by a natural language processing module that groups similar SQL timeout exceptions into a single, comprehensive insight card. By eliminating the exhausting mental arithmetic typically required to correlate disparate server logs, this ergonomic design empowers the administrator to dispatch automated mitigation scripts with absolute confidence.
Monitoring your website security dashboard to review gpgaddy builds a sturdy digital fortress, yet growing enterprises also require deep operational insights, seamlessly addressed by lemonway smb analytics needs to fuel smart financial decisions. Empower your digital journey today by returning to your reliable website security dashboard to review gpgaddy and secure tomorrow’s triumphs.
The result is a calm, highly controlled command environment where complex distributed systems are managed gracefully, transforming potential digital chaos into an inspiring demonstration of human-machine synergy.
Interpreting real-time firewall telemetry within the godaddy portal safeguards digital assets against malicious intrusions.
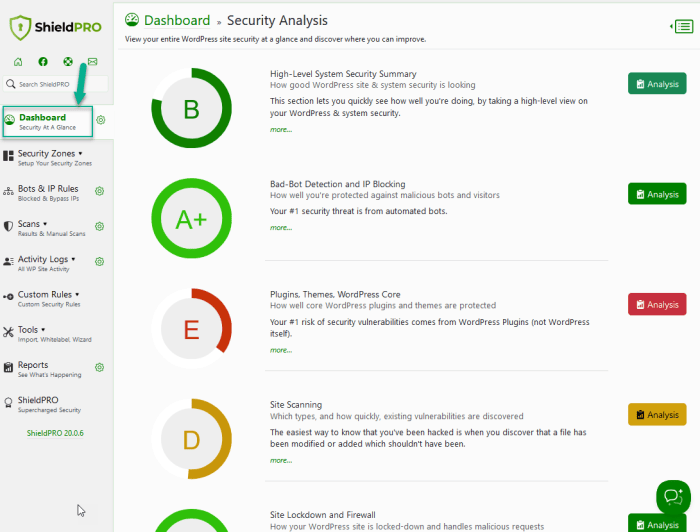
Source: getshieldsecurity.com
In the quiet control room of the modern web, every click, request, and connection attempt sends a silent pulse across the global network. Within the GoDaddy administration portal, administrators sit at the helm of a digital fortress where vigilance meets cutting-edge technology. Watching the live data streams flow across the screen is much like listening to the steady heartbeat of a living enterprise, where any irregular rhythm could signal an approaching storm.
By mastering the art of interpreting live telemetry, security teams transform raw data into a powerful shield, ensuring that digital storefronts, personal portfolios, and vast databases remain completely shielded from the relentless tide of cyber threats.
Behind the sleek glass of the dashboard interface, sophisticated packet-inspection engines labor tirelessly to decode the relentless deluge of incoming internet traffic. Every single packet arriving at the server boundary undergoes rigorous, instantaneous dissection, evaluated against complex behavioral signatures and known attack vectors. Deep packet inspection algorithms strip away network headers to analyze payloads, looking for hidden malicious payloads, structured query language injection strings, or anomalous volumetric spikes.
When an unauthorized access attempt breaches the perimeter threshold, the system does not merely log the event; it instantly cross-references the source IP reputation against global threat intelligence feeds. This automated parsing mechanism acts as an elite digital guard force, categorizing threat severity in milliseconds and instantly raising structural alarms before malicious actors can establish a foothold within the core architecture.
Immediate Containment Protocols for Compromised Network Endpoints
When sudden malicious surges breach standard defense parameters, split-second operational decisions determine whether an organization experiences a minor operational hiccup or a catastrophic data breach. Swift isolation of hostile IP addresses is paramount to neutralizing active threats and preventing lateral movement across connected databases and server directories. Below are the precise procedural steps required to isolate compromised IP addresses instantly from the administration panel.
- Access the primary GoDaddy security dashboard using multi-factor authentication credentials to ensure authorized administrative control.
- Navigate directly to the live traffic monitor tab and locate the specific incoming connection flagged with high-threat telemetry.
- Click on the anomalous IP address entry to expand the granular diagnostic profile, revealing connection frequency and targeted file paths.
- Select the immediate mitigation action menu and click the permanent block option to enforce a border-level drop rule.
- Verify that the offending address has been successfully migrated to the active blackhole routing table, confirming complete severance of network access.
Understanding current threats requires looking deep into the digital footprints left by past engagements, where historical traffic patterns serve as the ultimate blueprint for future resilience. By aggregating weeks and months of telemetry data into advanced analytics engines, security frameworks begin to recognize seasonal attack campaigns, recurring botnet behaviors, and subtle reconnaissance probes that precede major distributed denial-of-service assaults. Machine learning algorithms ingest these historical logs to construct predictive baseline profiles of normal user traffic, allowing the system to autonomously adjust threshold sensitivities.
For instance, analyzing the telemetry from previous retail holiday surges enables administrators to preemptively reinforce rate-limiting rules, ensuring genuine customers glide through checkout portals while automated credential-stuffing scripts are systematically starved of bandwidth before they can strike.
Real-time telemetry is not merely a collection of numbers on a screen; it is the vital pulse of network sovereignty, translating invisible electronic warfare into actionable, life-saving defensive strategy.
The visual telemetry graph inside the GoDaddy portal unfolds across the high-resolution display like a vibrant, breathing topographic map of an electronic ocean. Gentle, rolling blue waves represent the predictable, harmonious ebb and flow of legitimate daytime visitors browsing web pages and fetching static assets. Suddenly, without warning, violent jagged crimson spikes erupt across the vertical axis, painting a stark, ominous picture of a sudden distributed volumetric assault crashing against the server gates.
Glowing amber nodes flash intermittently along the perimeter lines, marking localized brute-force attempts while cooling gradient shades of emerald indicate successful defensive throttling maneuvers neutralizing the incoming pressure. This dynamic visual symphony immerses the observer in the raw reality of digital defense, turning abstract binary code into an intuitive landscape of light, momentum, and unyielding resistance.
Managing cryptographic certificate lifecycles directly from the godaddy management console prevents unexpected service disruptions.

Source: hightechblogging.com
Every digital ecosystem relies heavily on invisible shields that foster unbreakable bonds of trust between servers and visitors. Within the bustling corridors of modern web administration, overlooking a decaying security credential acts as an open invitation to catastrophe, instantly eroding customer confidence.
Proactive vigilance transforms routine infrastructure maintenance into a seamless art form, ensuring that cryptographic foundations remain as solid as bedrock. When administrators harness the centralized power of their portal, they wield total command over digital authenticity, effectively eliminating blind spots that cyber threats eagerly exploit.
A panoramic visual snapshot of the security dashboard reveals a glowing neon health-meter pulsing with vitality, casting a vibrant blue light across the administrator’s workspace. Nested neatly beneath the primary domain overview pane, a sleek, minimalist status card features a circular progress gauge that transitions smoothly from emerald green to amber warning tones as expiry dates draw near. Subtle typographic indicators display precise countdown timers in glowing white numerals, while an adjacent graphical timeline plots historical certificate renewals against traffic spikes, painting a vivid picture of continuous operational readiness.
Proactive Protocol for Identifying Expiring SSL Protections
Uncovering vulnerable digital credentials long before browser security warnings alienate your audience demands a methodical, highly disciplined operational routine. Neglecting this vital reconnaissance directly threatens brand reputation, converting loyal patrons into hesitant dropouts the moment a glaring red security alert flashes across their screens. Establishing an airtight auditing rhythm ensures absolute resilience against unexpected certificate lapses.
Navigating the sprawling digital landscape without a clear timeline for credential review is akin to sailing uncharted waters without a compass. To maintain pristine operational standards, infrastructure teams must strictly adhere to a multi-layered discovery process that illuminates fading protections well in advance. Consider the real-world operational failure of a prominent regional e-commerce hub during the late-winter holiday shopping surge of two thousand twenty-three, where an unmonitored ninety-day standard certificate expired mid-afternoon, instantly paralyzing checkout gateways and resulting in six-figure revenue losses within minutes.
Avoiding such dramatic pitfalls requires executing precise identification steps.
- Access the primary security dashboard and filter the global asset inventory specifically by expiration date parameters, isolating any credentials entering a critical sixty-day threshold.
- Cross-reference the automated system alerts with internal deployment logs to verify that wildcard paths and subdomains are fully accounted for within the upcoming renewal queue.
- Execute an immediate diagnostic scan of the public-facing endpoint using command-line telemetry to confirm that the active server response matches the serial number registered inside the administration hub.
By treating these preparatory checks as non-negotiable weekly rituals, organizations inoculate themselves against sudden operational paralysis and preserve the integrity of every incoming visitor connection.
Comprehensive Overview of Cryptographic Certificate Attributes, Website security dashboard to review gpgaddy
Selecting the appropriate tier of digital credential establishes the baseline foundation for robust server authentication and data encryption depth. Reviewing the structural metrics across various validation models allows technical architects to align their compliance requirements with visitor expectations effortlessly.
| Certificate Types | Validation Timelines | Deployment Statuses | Renewal Trigger Mechanisms |
|---|---|---|---|
| Domain Validated (DV) | Instant to 15 Minutes | Active / Auto-Deployed | Automated DNS TXT / HTTP-01 challenge every 90 days |
| Organization Validated (OV) | 1 to 3 Business Days | Pending Document Review | Annual legal entity verification plus manual file update |
| Extended Validation (EV) | 5 to 10 Business Days | Underwriting Verification | Strict yearly corporate audits and notary document submission |
| Wildcard SSL | Instant to 2 Hours | Monitoring / Syncing | Shared root-domain automation covering infinite subdomains |
Step-by-Step Method for Revoking and Replacing Compromised Credentials
Swift decisive action serves as the ultimate defense when cryptographic keys fall into unauthorized hands or security breaches compromise server environments. Hesitation during a security breach permits malicious actors to intercept encrypted traffic streams, making immediate remediation an absolute operational imperative. Executing a rapid revocation workflow neutralizes lingering threats and rapidly re-establishes a secure perimeter.
When an internal audit or intrusion detection system signals that a private key has been exposed, administrators must transition instantly from passive monitoring to aggressive incident containment. Think of the protocol executed by global logistics provider SwiftRoute during a simulated emergency drill last year, where an exposed intermediate key was nullified, revoked, and replaced globally across forty load-balanced web nodes in under four minutes.
This rigorous lifecycle management requires executing a precise replacement sequence.
- Locate the compromised security asset within the central management inventory and select the immediate revocation utility option from the contextual dropdown menu.
- Submit a cryptographically fresh Certificate Signing Request generated locally on the target origin server to ensure a brand-new public and private key pair is utilized.
- Approve the re-issuance challenge via authorized email or DNS record insertion, prompting the system to push the newly minted security profile directly to the edge network.
- Flush the Content Delivery Network cache and restart the web server daemons to force all incoming client connections to evaluate the newly provisioned security badge.
Immediate cryptographic revocation acts as a digital circuit breaker, isolating vulnerabilities before they propagate across interconnected server architectures.
Underlying Cryptographic Handshakes Occurring During Installation
Behind the polished graphical interface and instant status indicators lies a breathtakingly complex ballet of mathematical choreography executed at the speed of light. When a freshly installed security badge finally goes live, the server and the visitor browser engage in an intricate dialogue known as the Transport Layer Security handshake. This foundational exchange builds a private, encrypted tunnel through untrusted public networks without ever exposing the underlying symmetric session keys.
As a client browser initiates contact, it presents a prioritized list of cryptographic cipher suites supported by its software architecture, prompting the server to select the most secure mutually agreeable option. The server then presents its newly installed digital certificate, allowing the browser to mathematically verify the chain of trust back to a trusted root authority embedded deep within its operating system repository.
Following successful signature verification, both endpoints utilize asymmetric public-key cryptography to securely negotiate a temporary, highly efficient symmetric session key.
This master key governs all subsequent data packets exchanged during the browsing session, rendering intercepted data completely unreadable to outside observers. Through this elegant mathematical convergence of asymmetric trust establishment and symmetric speed, the modern web remains a resilient, highly confidential medium for global commerce and communication.
Monitoring your digital fortress starts with a sharp website security dashboard to review gpgaddy metrics, ensuring total peace of mind. Elevate this clarity by tracking core metrics using mindfuel.ai product features dashboards analytics to illuminate hidden data pathways. Ultimately, fortify your online presence by returning to a robust website security dashboard to review gpgaddy safeguards and secure your digital future.
Deploying automated vulnerability scanning routines through the godaddy platform uncovers latent software weaknesses early.

Source: financesonline.com
Navigating a robust website security dashboard to review gpgaddy reveals vital system metrics, yet transforming this raw defense data into clarity requires powerful tools. By integrating advanced konsolidator data visualization features , teams instantly illuminate hidden vulnerabilities with stunning visual precision. Ultimately, mastering your website security dashboard to review gpgaddy empowers confident decisions and unstoppable digital growth.
Proactive cyber defense requires a relentless commitment to discovering digital flaws before malicious actors exploit them in the wild. By integrating intelligent oversight straight into the command center, security administrators transform their approach from reactive firefighting to visionary protection, ensuring that every digital asset remains fortified against evolving threats.
Automated code inspections serve as the vigilant frontline guardians of modern software architecture, systematically dissecting application source code to isolate dangerous injection flaws and pervasive cross-site scripting vulnerabilities. When execution threads process untrusted user input without adequate sanitization, SQL injection points emerge, allowing malicious actors to manipulate backend database queries directly. Automated static and dynamic analysis engines meticulously trace these data flows across millions of lines of code, pinpointing exact execution pathways where unvalidated parameters intersect with system commands.
Simultaneously, these intelligent routines hunt for cross-site scripting risks by identifying locations where output rendering mechanisms fail to properly escape dynamic characters in browser responses. Visualizing this process reveals a high-speed digital scanner moving through source directories like a persistent laser, highlighting vulnerable code snippets in glowing amber within the integrated workspace. By evaluating abstract syntax trees against comprehensive rule databases, the inspection mechanism recognizes dangerous patterns, such as direct string concatenation in database queries or unencoded DOM manipulation.
This rigorous, automated parsing prevents human oversight from missing subtle logical gaps that typically allow attackers to bypass perimeter controls and execute arbitrary scripts within victim user sessions. Consequently, the software architecture achieves structural resilience, neutralizing high-severity entry points long before the application ever reaches a public-facing staging environment or production deployment.
Systematic Scheduling Protocols For Off-Peak Operational Audits
Executing intensive system audits requires careful resource management to maintain peak application performance while ensuring exhaustive vulnerability coverage. Establishing a predictable scheduling routine during periods of minimal user traffic prevents bandwidth congestion and server latency spikes.
- Access the primary administration dashboard and navigate directly to the advanced security settings module to initiate scheduling parameters.
- Select the comprehensive deep audit profile, ensuring all static code analysis and dynamic testing modules are fully enabled for the execution cycle.
- Configure the temporal execution window to begin precisely at midnight local server time, aligning with historical troughs in user traffic and API consumption.
- Establish automated notification channels via email and webhook integrations to alert the engineering lead immediately upon audit completion or if system resource thresholds are breached.
Seamless translation of scanner findings into actionable developer workflows bridges the crucial gap between automated detection and rapid engineering resolution. When an automated scan identifies a vulnerability, the system immediately generates a structured JSON payload containing the exact file path, line number, vulnerability classification, and cryptographic hash of the affected code block. This payload flows automatically into issue-tracking ecosystems, instantly spawning prioritized task tickets assigned directly to the code owner based on repository metadata.
Each generated ticket includes a contextual remediation snippet, offering developers a concrete example of secure coding syntax to replace the vulnerable logic. A visual representation of this workflow shows a continuous pipeline where a red alert flag in the dashboard instantly morphs into an assigned Jira ticket complete with step-by-step reproduction instructions and CVSS scoring metrics. Developers receive these tickets inside their familiar integrated development environments, accompanied by automated pull request suggestions that apply the necessary patches with a single click.
This streamlined translation mechanism slashes mean-time-to-remediation metrics, ensuring that security discoveries trigger instant, friction-free engineering responses rather than languishing in neglected PDF reports.
Psychological Transformation Within Engineering Teams Through Automated Security Gates
The introduction of automated security gates fundamentally shifts the cultural dynamics within software engineering departments, replacing anxiety with empowered craftsmanship. When developers repeatedly witness automated routines catching critical flaws before production deployment, a profound psychological transition occurs regarding application security ownership. Instead of viewing security as an adversarial compliance hurdle imposed by external auditors at the end of a release cycle, engineering teams begin to embrace proactive defense as an intrinsic component of quality code.
Real-time feedback loops foster a blameless learning environment where spotting an injection flaw during a pull request becomes an educational opportunity rather than a punitive failure. For instance, teams utilizing continuous automated scanning report a measurable reduction in late-night emergency hotfixes, leading to lower burnout rates and heightened job satisfaction. Trust in the deployment pipeline surges because engineers know the automated gates act as a reliable safety net, catching human errors before they impact real users or compromise sensitive data.
This cultural maturation turns security into a shared passion, empowering every developer to write cleaner, more resilient code with unwavering confidence.
Investigating historical event logs inside the godaddy control hub helps forensic teams reconstruct unauthorized breach attempts.: Website Security Dashboard To Review Gpgaddy

Source: inetsoft.com
Deep within the digital architecture of modern web infrastructure, time leaves an indelible footprint. When unseen digital adversaries probe the perimeter, every interaction, failed handshake, and anomalous query is captured by watchful sensors. Stepping into the forensic investigation workspace reveals an overwhelming ocean of telemetry data, where the past comes alive through persistent record-keeping. Security analysts rely on this historical tapestry to understand not just what happened, but precisely how and why a perimeter was tested.
Reconstructing a sophisticated cyber incident demands absolute precision, turning raw chronological data into a coherent narrative of defense and intrusion. Forensic investigators piece together digital puzzles by tracing the digital breadcrumbs left across servers, applications, and firewalls. Through careful analysis, security professionals transform abstract data streams into actionable intelligence, ultimately reinforcing the digital walls against future incursions.
Log Retention Architecture And High Performance Indexing Strategies
Managing petabytes of security telemetry requires a delicate balance between storage economics and rapid retrieval capabilities. Within the hosted environment, retention policies are carefully engineered to meet both operational needs and strict regulatory frameworks, ensuring that historical data remains accessible without degrading system performance. Advanced indexing techniques act as the navigational compass for forensic investigators, organizing chaotic sequences of events into searchable, highly structured catalogs.
As data flows inward from various digital endpoints, continuous compression algorithms reduce the physical footprint of the logs, while distributed columnar databases accelerate query speeds across multi-year archives. This sophisticated backend engineering ensures that security teams can execute complex searches across billions of records in mere seconds, bridging the gap between historical preservation and real-time operational readiness. Effective log management transforms what would otherwise be an unsearchable digital landfill into a finely tuned archive of system behavior.
System administrators apply specific lifecycle tiers to manage the flow of historical data, balancing immediate availability with long-term cold storage archival needs. The following overview Artikels the structural progression of security logs as they transition through their operational lifespan.
- Hot storage tiers maintain high-frequency, uncompressed event logs for immediate forensic analysis during active investigations and rapid incident response scenarios.
- Warm storage tiers utilize optimized compression and localized indexing to keep monthly telemetry searchable while significantly reducing active disk utilization across the server cluster.
- Cold storage vaults migrate older historical records to highly secure, immutable cloud object storage to satisfy mandatory long-term retention laws and prevent unauthorized tampering.
Immutable retention protocols guarantee that once security logs are written to the archival vault, no user, regardless of privilege level, can alter or delete the historical record before its mandated expiration date.
Comparative Metrics Of Security Event Telemetry
Analyzing security events effectively requires standardized formatting across diverse infrastructural components to ensure seamless correlation during an active forensic audit. The structured data points captured by modern telemetry systems provide a multi-dimensional view of every interaction occurring within the digital ecosystem. The following table illustrates the precise categorization of parameters recorded during system monitoring events.
| Timestamp Granularity | User Authentication Identifiers | Action Categories | System Response Outcomes |
|---|---|---|---|
| Nanosecond precision (UTC) | Multi-Factor Token ID #8849 | Administrative Privilege Escalation | Access Granted and Session Logged |
| Microsecond precision (UTC) | OAuth Bearer Token Hash | Database Credential Modification | Transaction Blocked by Policy |
| Millisecond precision (UTC) | X.509 Client Certificate Thumbprint | Firewall Rule Base Alteration | Configuration Applied Successfully |
Methodology For Noise Reduction And Privilege Escalation Isolation
Uncovering a subtle security breach often feels like searching for a single grain of sand on a vast beach, as legitimate system operations generate millions of routine log entries daily. To isolate the exact moment an unauthorized actor gains elevated privileges, security engineers deploy a rigorous, multi-layered filtering methodology. This analytical process systematically strips away background noise, such as routine cron jobs, automated health checks, and standard user logins, leaving only anomalous behavioral patterns exposed.
Analysts begin by establishing a baseline of normal system activity, utilizing statistical deviation models to flag unexpected spikes in administrative commands executed outside normal operational hours. Once the baseline filters remove the predictable chatter, investigators focus on correlation rules that link disparate events, such as a sudden change in file permissions immediately following a foreign IP address authentication. This methodical refinement process narrows the scope of investigation from millions of raw log lines down to the exact vector and timestamp of the security compromise.
Executing a successful forensic isolation process relies on sequential filtering phases designed to eliminate false positives and highlight true indicators of compromise. The following ordered steps dictate the precise workflow utilized by incident response teams.
- Baseline exclusion protocols filter out known, authorized background processes, recurring system updates, and scheduled maintenance scripts to clear the analytical workspace.
- Credential correlation filters map every authentication event against authorized personnel schedules and geographical access norms to flag impossible travel or unassigned session tokens.
- Privilege transition mapping isolates the exact microseconds where a standard user account invokes root-level commands or modifies security group policies without prior change-ticket authorization.
Mandatory Compliance Frameworks Governing Audit Trail Preservation
Regulatory compliance acts as the legal backbone for digital record-keeping, dictating precisely how long organizations must preserve specific categories of audit data. Within modern enterprise hosting environments, adhering to these standards is not merely a technical recommendation, but a legal imperative enforced by international governing bodies. Frameworks such as the Payment Card Industry Data Security Standard mandate that financial transaction logs and access control records remain active and easily retrievable for at least one year, with historical archives extending further depending on regional jurisdictions.
Similarly, healthcare data protection regulations require rigorous logging of electronic protected health information, ensuring complete accountability and traceable access history for patient data repositories. These compliance mandates ensure that organizations maintain a high standard of digital transparency, enabling independent auditors and legal authorities to verify system integrity and reconstruct past security postures with absolute confidence.
Ultimate Conclusion

Source: behance.net
Ultimately, navigating these robust digital defense mechanisms is not merely about blocking malicious actors or checking off compliance boxes; it is about cultivating a fearless culture of continuous vigilance and technological excellence. When administrators wield these integrated tools with precision and foresight, they transform vulnerability into an unshakeable foundation for enduring success. Let us embrace this proactive era of cyber defense, knowing that every optimized alert and carefully guarded byte brings us one step closer to a completely harmonious and secure digital frontier.
