data protection addendum for vendor agreements stands as the crucial boundary protecting modern enterprises as digital landscapes shift beneath our feet. Across the global marketplace, organizations face mounting pressure to safeguard sensitive consumer records shared with external partners. When legacy procurement systems collide with unforgiving regulatory mandates, a heavy administrative friction emerges across corporate ecosystems. Unearthing hidden legal liabilities lurking inside standard third-party contracting frameworks demands rigorous scrutiny from executive leadership and legal counsel alike.
Navigating this intricate web of compliance requires more than just good intentions; it calls for precision, foresight, and unyielding dedication to operational security. By establishing robust risk transference mechanisms and crystal-clear definitions of data ownership, businesses can transform potential vulnerabilities into pillars of resilience. The journey toward absolute digital accountability begins here, offering a path where commercial growth and unwavering privacy standards walk hand in hand toward a secure future.
Unearthing the hidden legal liabilities lurking inside standard third-party contracting frameworks requires careful scrutiny
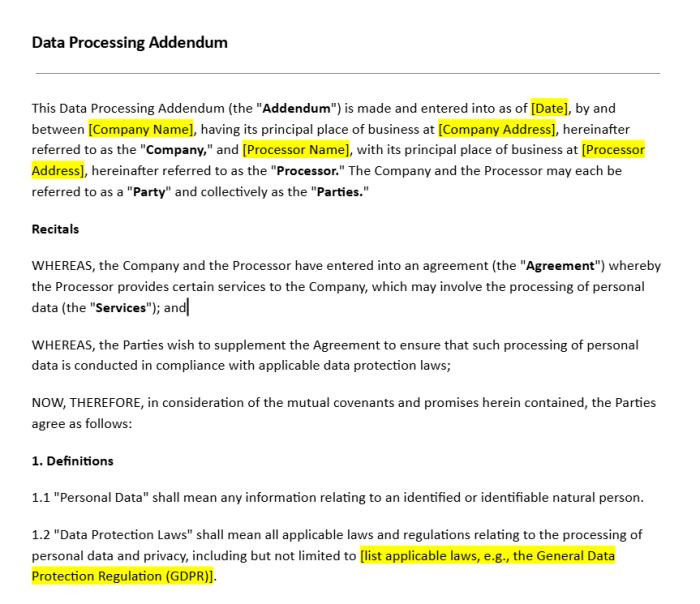
Source: freshdox.com
The modern digital landscape thrives on interconnected ecosystems, yet every external handshake carries the quiet weight of unmanaged vulnerability. When sensitive consumer data crosses organizational boundaries, the enterprise effectively surrenders its absolute perimeter control while retaining total regulatory accountability. Navigating this delicate terrain demands a meticulous architectural approach to vendor management, where legal agreements evolve from passive administrative paperwork into active shields of operational resilience.
Organizations sharing consumer records with external service providers face an intricate matrix of primary legal exposures that can fundamentally threaten their financial and reputational standing. Regulatory frameworks such as the General Data Protection Regulation and the California Consumer Privacy Act impose unyielding mandates on data controllers, meaning that outsourcing a process never outsources the ultimate responsibility for compliance failures. When a third party mishandles, leaks, or improperly monetizes consumer records, the host organization frequently becomes the primary target for enforcement actions, class-action lawsuits, and severe public censure.
Beyond direct statutory penalties, these exposures manifest as operational paralysis, catastrophic brand erosion, and the permanent loss of consumer trust. The financial impact extends far beyond immediate breach notification costs, encompassing multi-year forensic investigations, mandatory security overhauls, and steep litigation expenses. Furthermore, unauthorized data secondary usage by rogue vendors can quietly compromise proprietary market advantages, turning trusted partnerships into existential liabilities if the underlying contracts fail to establish absolute operational boundaries and immediate accountability.
Foundational principles of risk transference through contractual guardrails
Establishing effective risk transference requires constructing precise contractual mechanisms that legally isolate the enterprise from the operational failures of its vendors. This discipline relies on defining explicit boundaries of responsibility, ensuring that downstream partners shoulder the financial and legal burdens of their own security lapses. Indemnification provisions, rigorous audit rights, and mandatory incident notification timelines form the bedrock of this defensive posture.
Securing vendor contracts through a solid data protection addendum builds immediate operational trust and safeguards vital assets. As modern enterprises scale, evaluating the lemonway business model strengths weaknesses reveals critical insights into risk management and sustainable financial architecture. Ultimately, anchoring every partnership with a meticulous data protection addendum for vendor agreements guarantees enduring resilience, empowering your brand to thrive securely amidst evolving regulatory landscapes.
Rather than merely hoping for the best, organizations use these structural pillars to enforce accountability, transforming vague expectations into enforceable legal obligations that deter negligence and secure financial recovery when breaches occur.
- Indemnification clauses mandate that external providers cover all legal fees, regulatory fines, and settlement costs arising from data security incidents originating on their systems.
- Audit rights grant the enterprise unannounced access to inspect vendor facilities, infrastructure, and compliance documentation, ensuring continuous adherence to agreed-upon security baselines.
- Incident notification triggers establish strict chronological windows, often requiring vendors to report unauthorized access within hours to prevent compounding regulatory penalties.
Administrative friction within legacy procurement systems and modern regulatory mandates
The collision between aging procurement workflows and contemporary privacy statutes creates a profound operational bottleneck that slows down business agility while escalating legal exposure. Legacy systems were originally designed around fast-paced financial transactions and basic service level agreements, lacking the nuanced data-mapping capabilities required by today’s continuous compliance ecosystems. When modern regulatory mandates demand real-time visibility into data flows, cross-border transfers, and automated deletion requests, traditional procurement teams often find themselves relying on manual spreadsheets and disconnected approval chains.
This friction inevitably introduces human error, leaves critical vendor relationships unmonitored, and creates dangerous compliance gaps before contracts are even signed. Bridging this structural chasm requires a complete re-engineering of vendor onboarding, turning a historically bureaucratic hurdle into an intelligent, tech-enabled gateway that aligns commercial velocity with uncompromising legal protection.
Navigating data protection addendums for vendor agreements secures vital patient trust in modern healthcare operations. As teams build transparent solutions using rater8 healthcare reputation management github open source , open collaboration thrives alongside strict compliance. Ultimately, prioritizing these rigorous data protection addendums for vendor agreements safeguards sensitive medical information while empowering innovative digital growth.
True risk mitigation is not achieved through the sheer volume of contractual text, but through the seamless operationalization of accountability across every tier of the vendor ecosystem.
The following structural breakdown maps the direct correlation between common vendor vulnerabilities and the targeted administrative defenses required to neutralize them across enterprise departments.
| Contract Clauses | Associated Vulnerabilities | Mitigation Tactics | Responsible Departments |
|---|---|---|---|
| Data Retention and Deletion | Unauthorized long-term storage of consumer records after contract termination, increasing exposure window during a breach. | Enforce automated cryptographic shredding protocols and require certified proof of deletion within thirty days of contract end. | Legal and Information Security |
| Subprocessor Cascades | Unvetted fourth-party vendors accessing consumer data without the primary controller’s explicit knowledge or consent. | Mandate prior written approval for all subcontractor engagements and continuous automated discovery scans of vendor networks. | Procurement and Vendor Management |
| Cross-Border Transfers | Violations of regional data residency laws due to cloud backups routing through unauthorized international jurisdictions. | Implement strict geographical data pinning within cloud architecture provisions and utilize standard contractual clauses. | Compliance and Enterprise Architecture |
| Security Incident Response | Delayed reporting of security anomalies by vendors, allowing breaches to fester and multiplying regulatory penalties. | Establish mandatory four-hour notification SLAs coupled with pre-agreed forensic cooperation protocols and financial penalties. | Information Security and Public Relations |
Crafting operational definitions within auxiliary legal instruments prevents costly jurisdictional misunderstandings between enterprise buyers and suppliers.

Source: template.net
Modern commercial partnerships thrive when expectations are etched in absolute clarity, especially as digital ecosystems expand across global boundaries. When enterprise buyers shake hands with innovative software vendors, a failure to establish sharp operational definitions transforms minor procedural disagreements into enterprise-threatening litigation. Navigating the complex architecture of auxiliary legal agreements requires precision, foresight, and an uncompromising commitment to linguistic accuracy.
Every single clause acts as a structural pillar holding up the entire contractual bridge; if one definition is left ambiguous, the weight of a multi-million-dollar data breach can bring the whole arrangement crashing down into federal courtrooms.
Ambiguity in commercial contracts is an invitation for endless legal warfare, where corporate legal teams spend millions arguing over the intended meaning of simple words. When auxiliary agreements gloss over the exact parameters of information ownership, both enterprise buyers and third-party vendors often assume they retain ultimate dominion over generated insights. This dangerous oversight frequently manifests during high-stakes corporate disputes, such as the landmark litigation seen when enterprise cloud analytics providers clashed with multinational retail clients over proprietary customer telemetry data.
Without explicit language detailing whether raw inputs transform into proprietary vendor analytics, courts are forced to interpret vague intentions, resulting in multi-year legal marathons that bleed financial resources and paralyze brand reputation. Precise contractual design removes this judicial guesswork entirely, establishing an undeniable paper trail that honors the commercial intent of both parties from day one.
Definational Distinctions for Information Stewards
Establishing operational transparency demands a strict architectural breakdown of the entities handling corporate data assets within the supply chain ecosystem. Enterprise buyers must explicitly categorize their third-party partners to prevent dangerous regulatory compliance gaps under frameworks like the General Data Protection Regulation and the California Consumer Privacy Act. A data controller acts as the ultimate visionary, determining the explicit purposes and means of processing personal information, while a data processor strictly follows documented instructions to execute specific technical tasks on behalf of the controller.
Independent custodians operate under distinct legal obligations, maintaining neutral, secure storage environments without leveraging the underlying intelligence for commercial gain. Mapping these roles accurately inside supplemental agreements ensures accountability remains anchored precisely where the operational risk actually resides.
Linguistic Pitfalls in Territorial Jurisdiction
Drafting geographic boundaries and legal oversight zones requires meticulous attention to syntax, as a single misplaced preposition can accidentally subject a domestic enterprise to foreign judicial enforcement. Legal drafters must consciously eliminate vague geographic modifiers that leave room for aggressive regulatory interpretation across international borders. The following linguistic missteps consistently plague third-party vendor agreements and must be actively avoided during the drafting phase:
- Using broad phrases like global compliance standards without tying obligations to specific regional statutory frameworks, which inadvertently exposes the enterprise to conflicting international mandates.
- Failing to specify the exact physical location of data centers, creating a dangerous legal gray area regarding which nation’s sovereignty governs during a catastrophic cybersecurity incident.
- Relying on subjective terms such as reasonable local jurisdiction, which invites opposing counsel to argue endlessly over which municipal or federal court holds proper venue.
- Omitting explicit conflict-of-law clauses, leaving the governing legal framework completely vulnerable to unilateral interpretation by whichever party files a lawsuit first.
Comprehensive Asset Categorization Methodology
Organizing corporate assets within a supplemental agreement requires a structured matrix that evaluates both sensitivity levels and potential exposure impact. Enterprises must move beyond generic data labels and adopt a multi-tiered classification methodology that dictates exact security protocols for every byte moving through vendor pipelines. The implementation of this systematic approach allows compliance officers to immediately identify vulnerabilities and apply targeted cryptographic defenses before information leaves the secure corporate perimeter.
By categorizing assets based on regulatory exposure, proprietary value, and operational recoverability, organizations build an unshakeable defense mechanism.
Precise terminology acts as the ultimate digital armor, shielding modern enterprises from the devastating financial fallout of jurisdictional ambiguity and misplaced asset ownership.
Implementing this structured framework transforms abstract legal theory into a reliable operational shield, ensuring that enterprise buyers and their vendors operate with complete transparency. As global data privacy regulations continue to evolve at a relentless pace, the companies that survive and thrive are those that replace vague assumptions with bulletproof definitions. Every word written in an auxiliary agreement represents either a liability waiting to explode or a safeguard securing future innovation.
Establishing rigorous oversight mechanisms ensures that external partners maintain continuous operational vigilance over entrusted digital repositories.
Modern enterprises operate within a sprawling web of digital partnerships, where data flows seamlessly across distant servers, cloud environments, and external networks. Picture a bustling global trade port where thousands of shipping containers cross international borders daily; similarly, valuable corporate information crosses organizational boundaries into third-party hands every single second. Protecting this vital intellectual capital and sensitive customer data demands more than a handshake or a static annual security questionnaire.
Organizations must transition from passive trust to active, dynamic engagement, ensuring that external partners uphold the highest standards of digital hygiene without feeling micromanaged or legally suffocated.
Striking the delicate balance between robust security oversight and respect for vendor sovereignty requires innovative architectural planning and transparent communication channels. Rather than deploying intrusive surveillance tools that disrupt daily operations or violate proprietary business boundaries, forward-thinking enterprises implement telemetry-driven monitoring frameworks. These systems ingest non-invasive log data, vulnerability scan summaries, and encrypted compliance attestation feeds, offering a crystal-clear dashboard of security posture in real time.
For instance, global financial institutions routinely utilize automated API connectors that query external cloud configurations, instantly flagging unauthorized permission shifts without ever demanding direct access to the vendor’s underlying source code or proprietary algorithms.
True operational vigilance blooms not from aggressive policing, but through collaborative transparency where security becomes a shared competitive advantage rather than a bureaucratic burden.
Continuous monitoring implementation pathways
Deploying automated monitoring protocols across decentralized external infrastructures requires a structured, multi-layered strategy that honors contractual boundaries. Organizations must establish clear technical parameters during the initial contracting phase to define precisely what data telemetry is gathered, how it is encrypted in transit, and who retains viewing permissions. This methodology prevents friction, builds deep mutual trust, and guarantees that security teams receive vital operational insights without crossing into industrial espionage or overstepping jurisdictional limits.
- Establish mutually agreed-upon telemetry baselines that define acceptable performance indicators and security threshold metrics prior to data integration.
- Deploy read-only API connectors that securely stream encrypted compliance logs and system configuration metadata directly into the central enterprise dashboard.
- Implement automated anomaly detection algorithms that isolate unusual data access patterns, triggering immediate notification alerts for designated security liaisons.
- Schedule regular calibration workshops with vendor technical leads to review telemetry accuracy, minimizing false positives and refining system sensitivities continuously.
Oversight metrics and evaluation frameworks
Quantifying third-party digital health requires standardized evaluation matrices that translate complex technical behaviors into actionable governance insights. The following structured overview highlights the core parameters utilized by enterprise risk committees to measure, evaluate, and enforce operational vigilance across diverse vendor ecosystems.
| Oversight Metrics | Evaluation Frequencies | Remediation Triggers | Penalty Structures |
|---|---|---|---|
| API Access Anomaly Rates | Real-time streaming | Spike exceeding 15 percent over baseline | Temporary suspension of data feed access |
| Patch Deployment Velocity | Bi-weekly automated audits | Critical vulnerabilities remaining unpatched past 72 hours | Financial withholdings per delayed SLA |
| Encryption Protocol Integrity | Monthly cryptographic scans | Detection of deprecated cipher suites or expired certificates | Mandatory third-party security re-certification |
| Subcontractor Compliance Audit | Quarterly documentation review | Unapproved fifth-party data handlers identified | Contract termination proceedings initiation |
Procedural steps for unannounced digital infrastructure audits
Executing sudden yet legally compliant security inspections on remote vendor environments demands absolute precision, careful legal framing, and strict adherence to established protocols. When critical threat intelligence suggests a potential vulnerability or an unauthorized data exposure within a supplier’s network, security teams must act swiftly. These targeted investigations must bypass normal administrative bottlenecks while remaining strictly confined to the scope authorized by the original enterprise agreement, ensuring that forensic findings remain legally admissible and operationally actionable.
- Activate the emergency audit clause within the master services agreement, officially notifying the vendor’s designated legal counsel and chief information security officer simultaneously.
- Deploy certified forensic inspection tools that capture volatile memory states, network traffic logs, and access control lists without altering or corrupting native system data files.
- Isolate the suspected digital perimeter through temporary network segmentation protocols, preventing lateral movement of potential malware or unauthorized data extraction processes.
- Conduct a joint debriefing session with the vendor engineering team within twenty-four hours of audit completion to review raw forensic telemetry and draft an immediate remediation roadmap.
Rigorous framework for reviewing third-party subcontracting chains
Modern supply chains rarely consist of a simple one-to-one relationship, often expanding into complex webs of fourth and fifth-party vendors that handle sensitive information streams. An enterprise might completely trust its primary cloud analytics provider, only to discover that the provider outsources data storage to an unvetted offshore subcontractor with weak cybersecurity controls. Unearthing and neutralizing these hidden liabilities requires a methodical, top-down evaluation framework that traces every single data pathway from origin to final destination.
- Mandate complete transparency by requiring primary vendors to submit and continuously update a comprehensive register of all downstream subcontractors touching enterprise data streams.
- Enforce strict pass-down data protection clauses, legally binding every subcontractor to the exact same security, encryption, and privacy standards agreed upon in the primary contract.
- Conduct independent risk assessments and background verifications on critical subcontractors that possess administrative privileges over core digital repositories.
- Retain the absolute contractual right to veto any downstream subcontractor whose security posture fails to meet enterprise risk tolerance thresholds, forcing immediate vendor replacement.
Navigating the treacherous waters of cross-border information transfers demands adherence to complex international privacy frameworks.: Data Protection Addendum For Vendor Agreements

Source: template.net
Moving sensitive data across international borders resembles steering a heavily laden cargo ship through a dense, storm-tossed fog where hidden reefs threaten financial ruin at every coordinate. Global enterprises constantly wrestle with the profound gravity of protecting personal identifiers while maintaining the frictionless velocity required by modern digital commerce. Behind every routine cloud synchronization lies a labyrinth of statutory obligations that tests the operational resilience of even the most sophisticated vendor ecosystems.
Securing vendor partnerships requires a solid data protection addendum, much like bringing order to chaos by learning how to sort alphabetically in excel to align every critical compliance detail. Mastering this organizational rhythm transforms overwhelming security reviews into clear pathways for growth, ensuring every vendor agreement remains meticulously protected and transparently managed.
Organizations must weave intricate webs of administrative safeguards to ensure that information assets remain protected from unauthorized foreign surveillance and accidental exposure during transit. The ultimate success of any multinational supply chain relies entirely on how seamlessly its technical architects translate dense statutory mandates into concrete, daily engineering practices across disparate geographic regions.
Operational Hurdles of Transatlantic Information Migration
Transporting European citizen profiles across transatlantic cloud boundaries introduces a monumental strain on corporate engineering teams who must reconcile conflicting legal philosophies regarding fundamental human rights and commercial necessity. European regulatory bodies demand absolute control and continuous oversight over digital assets originating within their territory, creating immense friction when US-hosted infrastructure processes those same records. Vendors frequently discover that maintaining synchronized databases requires deploying costly local proxy servers and implementing strict data minimization strategies to limit the volume of personal information exposed to foreign soil.
Real-world enforcement actions vividly illustrate the tangible risks of failing to navigate these turbulent migration waters effectively. A prominent multinational financial services provider recently encountered severe operational paralysis and substantial monetary penalties when local supervisory authorities audited their cloud storage architecture and uncovered unauthorized telemetry tracking of EU residents flowing directly into unencrypted stateside analysis pipelines. To prevent such costly disruptions, modern supply chain operators must completely restructure their deployment pipelines to guarantee that European citizen profiles remain partitioned within sovereign cloud zones, effectively decoupling local user experiences from centralized foreign processing nodes.
Regulatory Divergences Between Regional Compliance Models, Data protection addendum for vendor agreements
Multinational supply chains operate under a patchwork of overlapping and frequently contradictory legal regimes that dictate how digital assets must be stored, processed, and protected. Understanding the foundational differences between these regional frameworks is essential for preventing catastrophic compliance failures that can halt cross-border commerce overnight.
The following structural comparison highlights the primary operational distinctions governing international information stewardship across major economic jurisdictions.
| Compliance Framework | Primary Enforcement Focus | Default Stance on Cross-Border Flow | Maximum Financial Exposure |
|---|---|---|---|
| European Union GDPR | Fundamental individual privacy rights and explicit consent | Restricted unless rigorous adequacy decisions or standard contractual clauses apply | Up to 4 percent of global annual turnover or 20 million Euros |
| California Consumer Privacy Act | Consumer transparency, opt-out mechanisms, and data monetization | Permitted with mandatory disclosure and consumer opt-out rights | Statutory fines scaled per intentional violation plus civil litigation risks |
| People’s Republic of China PIPL | National security, critical information infrastructure, and local data localization | Strictly controlled through mandatory government security assessments | Severe administrative penalties, business suspension, and personal liability |
Visual Architecture of International Information Transit Networks
Comprehensive situational awareness of global network topology requires visualizing the exact physical and logical pathways that digital assets traverse during international transit operations. A detailed cartographic representation of an international information transit map reveals a glowing digital canvas stretched across a dark vector map of the globe, vividly illustrating the intricate journey of enterprise assets.
Brilliant cyan data streams pulse along transatlantic fiber-optic cables resting on the dark ocean floor, converging at brightly illuminated coastal landing stations equipped with biometric security perimeters. As the streams approach specific continental borders, they encounter towering, semi-transparent holographic pillars representing strict jurisdictional thresholds where automated compliance gateways inspect every packet for valid cryptographic signatures. Deep inside secure subterranean vaults depicted as gleaming, modular storage silos, information rests behind multi-layered encryption checkpoints operating on advanced post-quantum algorithms, ensuring that even if physical hardware is intercepted, the contents remain completely indecipherable.
Mandatory Notification Timelines for Lawful Interception Demands
When foreign intelligence agencies issue lawful interception demands to third-party vendors, the speed and transparency of the subsequent communication dictate whether an enterprise can mitigate regulatory liability or face devastating legal consequences. Foreign surveillance directives often arrive under a heavy shroud of secrecy, accompanied by statutory gag orders that forbid immediate public disclosure, creating an agonizing dilemma for vendor compliance officers.
Safeguarding sensitive assets through a robust data protection addendum for vendor agreements remains vital today. Organizations now monitor compliance dynamically using ocula.tech product features dashboards to illuminate hidden risks. Harnessing these bright visual insights empowers teams to conquer regulatory hurdles, ensuring every vital partnership strictly upholds rigorous data protection addendum for vendor agreements standards.
To maintain regulatory alignment with stringent extraterritorial privacy laws, enterprise agreements must enforce strict operational protocols regarding how and when vendors disclose these external demands to data controllers.
- Vendors must acknowledge receipt of any foreign intelligence interception demand within an aggressively compressed window, typically not exceeding twenty-four hours from the initial issuance.
- If legally permitted by the issuing jurisdiction, the vendor is contractually obligated to notify the affected enterprise data controller within forty-eight hours to allow for immediate legal challenge and containment measures.
- In scenarios involving absolute secrecy orders, the vendor must implement automated cryptographic canary systems that alert enterprise security teams the moment standard operational transparency protocols are forcefully interrupted.
- Comprehensive post-incident forensic reports detailing the exact scope of accessed metadata must be delivered to compliance stakeholders within seventy-two hours of the interception order being lifted or modified.
Absolute transparency in the face of foreign surveillance demands is the ultimate firewall protecting organizational integrity across international borders.
Orchestrating a seamless offboarding protocol guarantees that retained institutional assets are permanently scrubbed from external hardware.
When enterprise partnerships dissolve, the digital footprint left behind can easily transform into a ticking compliance time bomb if left unattended. Bringing an external vendor relationship to a close requires much more than simply revoking API keys and closing communication channels; it demands a surgical, definitive end to data stewardship. Imagine digital vaults locking forever, leaving zero room for lingering files or forgotten caches of sensitive corporate intelligence.
Transforming a messy vendor exit into an immaculate data wipe protects brand integrity and keeps enterprise balance sheets safe from catastrophic regulatory penalties under strict global privacy laws.
Achieving absolute data eradication demands advanced cryptographic sanitization techniques that render shared intellectual property utterly unrecoverable. Standard file deletion merely removes pointers in a directory, leaving the actual binary data sitting quietly on storage blocks waiting to be harvested. Enterprise-grade cryptoshredding solves this vulnerability by encrypting the data at rest with a robust key, such as AES-256, and then permanently destroying that key.
Without the decryption key, any remaining bits of proprietary algorithms, customer records, or trade secrets are mathematically transformed into meaningless, unrecoverable noise. This methodology aligns with rigorous standards like NIST SP 800-88 Revision 1, ensuring that even state-of-the-art forensic recovery tools deployed by malicious actors or disgruntled former partners return nothing of value.
Cryptographic Sanitization and Verification Protocols
Validating the complete removal of intellectual property requires a meticulous sequence of mathematical proofs and status logs generated directly by the hardware controller. Vendors must utilize secure overwrite commands, such as block-level zero-fills combined with pseudo-random pattern injections across every addressable logical sector. Following the wiping phase, independent cryptographic hash functions like SHA-256 are executed against the storage media to compare pre-wipe and post-wipe signatures.
A successful verification yields a deterministic output confirming that zero residual data structures match the original enterprise assets.
Post-agreement retention of unauthorized archival backups constitutes a severe breach of data protection mandates, exposing the offending entity to mandatory statutory fines, severe reputational erosion, and direct civil litigation for corporate espionage and privacy negligence.
Solid-state drives present unique challenges during decommissioning because wear-leveling algorithms dynamically remap sectors, often hiding remnants of sensitive consumer metrics in inaccessible over-provisioned areas. Addressing this physical reality requires executing native drive commands like the SATA Secure Erase or NVMe Sanitize Crypto Scramble, which instruct the internal controller to reset all mapping tables and destroy the internal encryption keys simultaneously.
When software-based sanitization fails to guarantee complete eradication due to hardware failure, mechanical shredding and high-intensity degaussing must be deployed. External partners are obligated to provide a notarized certificate of destruction, complete with serial numbers, cryptographic verification hashes, and photographic evidence of the pulverized media, effectively sealing the offboarding lifecycle with undeniable accountability.
Ultimate Conclusion

Source: bling.cloud
Ultimately, mastering the art of third-party compliance empowers organizations to navigate complex regulatory waters with absolute confidence and unwavering strategic vision. From establishing airtight jurisdictional definitions to executing cryptographic sanitization upon contract termination, every single safeguard deployed represents a profound investment in organizational trust. As we look toward an increasingly interconnected digital horizon, proactive risk management remains the defining hallmark of industry leaders who refuse to leave their digital assets to chance.
