netscout commercial filtering network data transfer product models stand at the vanguard of modern digital infrastructure, silently orchestrating the immense, invisible rivers of information that power our global economy. Beneath the hum of enterprise server racks and the blinding speed of fiber-optic cables lies a sophisticated ecosystem where raw electrical impulses are captured, examined, and transformed into actionable intelligence with absolute precision.
As digital traffic scales to unprecedented velocities, the imperative to maintain pristine network visibility becomes a defining challenge for organizations worldwide. Through the deployment of advanced hardware telemetry probes and intelligent packet scrubbing architectures, engineers can now dissect multi-gigabit data streams in real time. This comprehensive exploration examines the intricate mechanisms, structural hardware variants, and resilient synchronization frameworks that empower modern enterprises to navigate complex digital landscapes without compromising performance or security.
Unraveling the architectural foundation behind enterprise telemetry interception systems and how packet flow filtering operates at gigabit velocities
Source: com.tw
Modern digital enterprises generate unprecedented volumes of traffic traversing complex network veins, requiring advanced observation frameworks to maintain operational visibility. As data streams accelerate past gigabit thresholds, traditional monitoring paradigms falter under the sheer mass of colliding information. The modern engineering landscape demands robust interception systems capable of maintaining absolute fidelity without introducing operational lag into mission-critical pipelines.
Deep packet inspection engines deployed within contemporary data switching fabrics operate as high-speed analytical sentinels, dissecting raw binary traffic at wire speed. At the heart of this capability lies the intersection of specialized application-specific integrated circuits and parallelized multi-core processing units. As packets traverse the optical transceivers, physical layer signals are immediately digitized and ingested into massive high-speed SRAM buffers.
The silicon fabric executes line-rate regex matching and stateful flow tracking simultaneously, evaluating millions of packet headers per second against complex corporate security and performance policies. This immediate inspection layer strips away irrelevant broadcast traffic while prioritizing critical application telemetry, ensuring that downstream monitoring tools receive only the most actionable intelligence.
Architectural Deployment and Strategic Hardware Probe Placement
Deploying observation hardware requires meticulous topographical planning to ensure zero blind spots exist across the digital enterprise ecosystem. Strategic placement of physical interception probes directly along core routing bottlenecks guarantees the capture of transient synchronization frames that indicate micro-bursts and connection anomalies. Engineers position these passive optical splitters and active TAP modules precisely at the convergence points between enterprise data centers and wide-area network gateways, capturing every photon traversing the fiber optic cables without inducing optical insertion loss.
Visualizing this setup reveals a pristine server rack within a dimly lit enterprise data center, where high-density fiber optic patch panels glow with amber link lights. Heavy-duty copper cables feed directly into rack-mounted telemetry appliances equipped with custom FPGA acceleration cards. A cascade of blinking green status LEDs indicates real-time packet ingestion across forty-gigabit interfaces, while thermal management units softly hum to dissipate the intense heat generated by millions of parallel evaluations happening every microsecond.
Understanding the precise operational sequence of payload handling requires examining the systematic dismantling of encapsulation layers. When packets arrive encapsulated within complex tunneling protocols, the interception fabric initiates a multi-stage decoding process:
- The incoming frame undergoes initial layer-two and layer-three validation to ensure structural integrity before entering the primary processing queue.
- Outer tunnel headers, such as GRE, VXLAN, or IPsec, are systematically parsed and stripped by dedicated hardware lookup tables.
- The inner payload is exposed and normalized into a standard telemetry format, stripping away proprietary transport noise while preserving application-level context.
- Extracted metadata and sanitized packet pointers are directed toward analytical buffers, while the raw payload continues its unaltered journey through the primary switching fabric.
Precision telemetry interception requires balancing aggressive packet filtering with absolute transparency, ensuring zero degradation to the underlying carrier network.
Evaluating the generational leap in interception technology involves analyzing key performance metrics across legacy systems and contemporary high-velocity units. The following comparative data illustrates the exponential improvements achieved in modern network telemetry architectures:
| Interception Unit Generation | Latency Metrics (Nanoseconds) | Buffer Sizes (Megabytes) | Packet Drop Thresholds (Percentage) | Throughput Capacities (Gigabits per Second) |
|---|---|---|---|---|
| Legacy Units (Circa 2012) | 4500 ns | 64 MB | 2.5% at peak load | 10 Gbps |
| Contemporary Units (Modern Era) | 180 ns | 1024 MB | < 0.001% at saturation | 100 Gbps to 400 Gbps |
Examining the diverse commercial hardware variants engineered for high-density packet scrubbing and continuous traffic categorization

Source: cloudfront.net
Beneath the sleek steel bezels of modern enterprise network security appliances lies a relentless engineering marvel designed to tame the chaotic deluge of global data traffic. When millions of packets slam into a data center gateway every single second, ordinary computing hardware buckles under the immense pressure of deep packet inspection and real-time behavioral analytics. Engineers have therefore forged specialized physical guardians—heavy-duty commercial hardware variants built specifically to capture, scrub, and categorize massive streams of network telemetry without dropping a single vital frame.
These machines do not merely process data; they impose absolute order upon the digital storm, ensuring that every gigabit of information is meticulously inspected, categorized, and channeled to its proper destination with zero latency penalty.The physical reality of deploying such power requires an uncompromising marriage of raw mechanical durability and ultra-dense silicon efficiency. Every chassis deployed within a modern enterprise floor represents a carefully calculated balance of thermal dissipation, electrical redundancy, and modular expandability.
Whether dealing with sudden traffic spikes caused by global digital events or maintaining steady-state enterprise operations, these hardware platforms stand ready to absorb the strain. They serve as the unyielding physical backbone of digital defense, transforming abstract network protocols into tangible, manageable streams of pristine telemetry.
Modular Chassis Versus Fixed Configuration Gateway Specifications
The architectural divide between modular rack-mounted appliances and fixed-configuration gateway boxes defines how modern enterprises scale their telemetry filtering infrastructures. Modular appliances are the heavy cruisers of the server room, engineered for environments where network demands evolve overnight and downtime carries an unacceptable financial toll. These flexible powerhouses feature hot-swappable line cards, redundant power supply units, and expandable backplanes capable of scaling from baseline gigabit speeds straight into terabit-per-second processing tiers.
Enterprise architects choose modular systems when future-proofing is paramount, allowing them to slide in fresh processing blades or upgraded optical transceivers without ever powering down the main chassis. Conversely, fixed-configuration gateway boxes operate as the agile interceptors of the enterprise edge, optimized for space-constrained remote offices or dedicated regional monitoring nodes. Built into rigid, non-expandable 1U or 2U enclosures, these fixed units deliver blistering performance right out of the box at a fraction of the capital expenditure required for modular setups.
Their internal components are soldered directly to optimized printed circuit boards, reducing electrical resistance and signal degradation across high-speed internal traces. While they lack the battlefield upgradeability of their modular siblings, fixed gateways compensate with exceptional reliability, lower baseline power draws, and simplified deployment procedures that minimize human configuration errors during rapid rollouts.To better understand how these two contrasting hardware philosophies stack up against one another in demanding production environments, the following comparative breakdown illustrates their core operational parameters.
| Architectural Variant | Power Consumption Ratings | Cooling Requirements | Port Density Configurations | Field-Replaceable Unit Lifespans |
|---|---|---|---|---|
| Modular Rack-Mounted Appliance | 1,200W to 3,000W+ under peak enterprise load conditions | High-velocity multi-fan hot-swap rotor trays with front-to-back airflow zones | Up to 128x 10GbE / 32x 100GbE ports via swappable line cards | 5 to 7 years for active modules; chassis frame durable up to 10 years |
| Fixed-Configuration Gateway | 350W to 750W optimized for predictable edge workloads | Integrated dual-redundant blower fans with side-vent exhaust channels | Fixed array of 24x 1GbE/10GbE SFP+ ports and 4x 40GbE QSFP+ uplinks | 3 to 5 years sealed unit lifespan prior to scheduled hardware refresh |
Silicon Acceleration Modules and Cryptographic Offloading Mechanics
The sheer volume of encrypted traffic traversing modern corporate networks means that traditional central processing units quickly exhaust their core cycles attempting to decrypt and inspect payload contents. To conquer this computational bottleneck, hardware engineers integrate dedicated silicon acceleration modules, such as specialized field-programmable gate arrays and multi-core cryptographic coprocessors, directly onto the packet scrubbing board. These auxiliary processing engines function as tireless specialists, intercepting incoming data streams to perform heavy mathematical lifting like AES decryption, hash verification, and stateful packet matching in hardware.
By offloading these intense cryptographic verification tasks from the primary system CPU, the appliance preserves precious processing bandwidth for advanced behavioral analytics and policy enforcement. The internal silicon architecture utilizes parallelized pipelining, routing incoming packets through microscopic silicon pathways designed explicitly for bitwise pattern matching rather than general-purpose computing.
True enterprise-grade network visibility is achieved only when heavy cryptographic overhead is successfully banished from the central CPU to dedicated, wire-speed silicon accelerators.
This hardware-level division of labor ensures that even when organizations experience severe traffic surges or sophisticated obfuscation attempts, the telemetry pipeline remains completely fluid, maintaining consistent microsecond-level latency across all inspection channels.
Physical Mounting Dimensions and High-Density Data Center Integration, Netscout commercial filtering network data transfer product models
Integrating high-density packet filtering nodes into modern enterprise data centers demands strict adherence to rigorous spatial, weight, and thermal engineering standards. Most enterprise-grade modular filtering appliances occupy between 2U and 4U of standard 19-inch server rack space, weighing anywhere from twenty to over fifty kilograms once fully populated with power supplies and interface blades. Fixed-configuration gateways typically claim a modest 1U footprint, allowing administrators to pack multiple monitoring endpoints into vertical rack space that would otherwise remain underutilized.
Precision rail kits and cable management arms are mandatory accessories during installation, ensuring that heavy optical fiber bundles do not place undue mechanical stress on the chassis faceplates or obstruct critical airflow paths.The thermal footprint of these deployed nodes is equally vital, as high-density server cabinets can rapidly transform into localized heat traps if front-to-back cooling containment is compromised. Facilities engineering teams must account for heavy thermal output values, often exceeding 10,000 BTUs per hour for fully loaded modular chassis, requiring cold aisle containment pods and intelligent floor tile placement to maintain optimal operating temperatures.
Visual inspection of a properly deployed telemetry rack reveals orderly rows of vibrant yellow and aqua fiber-optic cables sweeping cleanly into high-density transceiver banks, anchored securely to reinforced vertical mounting rails designed to withstand minor seismic disturbances. Every millimeter of rack real estate is treated as a critical asset, balancing physical accessibility for field engineers with the unyielding requirement for maximum computational density per square foot of data center floor space.
Translating raw electrical signal fluctuations into structured behavioral telemetry suitable for downstream storage and anomaly detection engines
The journey from chaotic photon waves traveling across fiber-optic strands to pristine, actionable network intelligence is a marvel of modern engineering. Within the high-stakes theater of enterprise cybersecurity, milliseconds separate total network compromise from swift, automated defense. Transforming chaotic physical phenomena into disciplined, organized data streams requires sophisticated hardware-software co-design that operates at wire speed without dropping a single packet.
As asynchronous packet bursts hit the specialized network interface cards of these interception appliances, the incoming torrent undergoes rigorous normalization procedures. Physical-layer voltage oscillations are instantly sampled, clock-recovered, and converted into discrete digital symbols. The ingestion engine strips away proprietary physical framing, aligns varying MTU sizes, and neutralizes micro-burst jitter through dedicated elastic buffering buffers. Every timestamp is meticulously synchronized to atomic precision via Precision Time Protocol, ensuring that temporal ordering remains absolute even when millions of concurrent connections flood the pipeline simultaneously.
This systematic scrubbing eliminates line noise, corrects minor signal degradations inherent in long-haul transmission, and establishes a uniform baseline format before the payload ever touches general-purpose memory registers.
Algorithmic Session Reconstruction and Memory Management
Reassembling fragmented transport layer segments into cohesive session records demands an uncompromising balance between stateful tracking and memory conservation. The ingestion firmware deploys lock-free ring buffers alongside hierarchical hash tables to track millions of concurrent TCP/UDP streams in real time. When out-of-order packets arrive, they are temporarily parked in bounded scratchpads while sequence numbers are mathematically reconciled. To protect against sophisticated denial-of-service vectors aimed at memory exhaustion, deterministic eviction algorithms aggressively prune stale or half-open connections.
Memory allocation operates on strict static pools rather than dynamic heap allocations, effectively eliminating memory leakage risks during extended operational cycles under maximum load.
As advanced netscout commercial filtering network data transfer product models rapidly secure our digital highways, organizations must simultaneously optimize hidden operational drains through efficient utility expense management. Mastering this financial balance illuminates a brighter corporate future, empowering these robust netscout commercial filtering network data transfer product models to drive peak performance effortlessly.
Sustaining zero-allocation state tracking at 100Gbps line rates requires bounded memory pools and deterministic garbage collection alternatives.
Before persistent indexing takes place, eliminating redundant network noise is crucial for preserving storage bandwidth and accelerating downstream anomaly detection engines. Several targeted filtering methods actively purge uninformative traffic prior to disk or database commitment.
- Discarding gratuitous ARP broadcasts and local subnet discovery chatter that carry zero enterprise behavioral value.
- Suppressing repetitive keep-alive packets and empty TCP acknowledgment loops that artificially inflate storage volumes.
- Filtering known benign background multicast streams originating from local printer discovery and media server protocols.
- Dropping malformed packets failing basic checksum validation before they consume expensive CPU cycles in deep packet inspection stages.
The intricate transformation of raw wire data into secure, searchable telemetry relies on a finely tuned matrix of processing speeds, compression thresholds, and cryptographic validation. The following architectural specifications dictate how enterprise collectors handle payload sanitization at scale.
| Data Conversion Speed | Compression Ratio | Hashing Algorithm | Schema Definition |
|---|---|---|---|
| 100 Gbps per processing blade | 3.2 : 1 lossless delta | XXH64 non-cryptographic fast hash | Protobuf v3 binary schema |
| 40 Gbps aggregate per core | 4.5 : 1 dictionary-based | SipHash-2-4 collision-resistant | Apache Parquet columnar layout |
| 200 Gbps burst capability | 2.1 : 1 run-length encoding | CityHash128 high-velocity | FlatBuffers optimized structure |
| 10 Gbps legacy fallback | 5.0 : 1 zstandard maximum | MurmurHash3 low-latency | JSON Schema strict-typed |
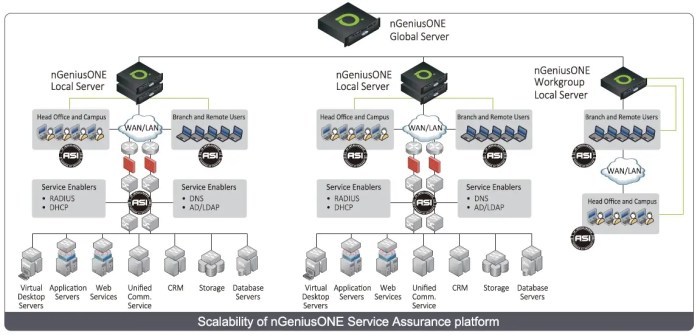
Establishing resilient operational workflows for synchronizing distributed filtering appliances across geographically segregated enterprise network topologies

Source: cloudfront.net
NetScout commercial filtering network data transfer product models rapidly dissect complex digital traffic with clinical precision, illuminating hidden operational insights. Just as analysts master how to build pivot table structures to transform chaotic spreadsheets into beacons of clarity, these robust enterprise solutions empower organizations to filter overwhelming data streams, ensuring seamless network performance and unstoppable growth.
Enterprise networks span vast continental divides, weaving a complex digital web where milliseconds matter and data visibility cannot afford a single blind spot. When global organizations deploy high-density packet scrubbing sensors across Tokyo, Frankfurt, and New York, maintaining a synchronized heartbeat across these far-flung nodes becomes the ultimate engineering tightrope walk. Picture a colossal, invisible symphony orchestra spread across continents, where every single musician must strike the exact same chord simultaneously, regardless of oceanic lag.
This operational choreography relies on absolute precision, robust automation, and resilient network design that transforms chaotic global traffic into a harmonious, unified stream of actionable telemetry.Achieving this level of synchronized vigilance requires sophisticated underlying architecture that bridges massive geographical distances without introducing latency bottlenecks or policy drift. Regional scrubbing stations constantly ingest terabits of raw electrical and optical data, demanding a centralized command structure that pushes filtering rules instantly to the edge.
Real-life deployments, such as those managed by multinational financial clearinghouses during peak trading hours, demonstrate that even a microsecond delay in policy propagation can leave security perimeters vulnerable. By leveraging state-of-the-art out-of-band management channels and optimized distribution pipelines, network architects ensure that every localized sensor operates from an identical, immutable source of truth.
Unified Policy Distribution Protocols Across Regional Scrubbing Stations
Maintaining a cohesive security posture across disparate international boundaries demands a rigorous, highly secure configuration management framework that leaves zero room for manual discrepancies or human error. Enterprise telemetry systems utilize encrypted, mutually authenticated RESTCONF and NETCONF protocols layered over high-availability Transport Layer Security connections to distribute policy definitions from central orchestration engines down to localized hardware nodes. As configuration templates are updated at headquarters, hierarchical YANG data models systematically validate syntax, structural integrity, and hardware capability constraints before dispatching the payload to regional appliances.
Absolute synchronization of security policies across global nodes transforms fragmented regional defenses into an impenetrable, unified digital shield.
Once the encrypted policy package arrives at a regional scrubbing station, local daemons ingest the payload into staging memory banks, executing cryptographic checksum verifications to confirm zero transit corruption. The appliance then performs a dry-run compilation of the packet filtering rules against its specific physical ASIC architecture, ensuring that line-rate processing speeds will not degrade upon activation. This seamless, automated handshake guarantees that a newly minted threat signature deployed in a London data center is actively scrubbing traffic across Asian and American nodes within a fraction of a second, perfectly harmonizing global enterprise defense mechanisms.
Emergency Failover Mechanics During Power Interruptions and Link Degradations
When catastrophic infrastructure failures strike—ranging from regional power grid collapses to severed undersea fiber-optic cables—enterprise telemetry architectures must execute lightning-fast, deterministic failover routines to preserve network continuity. Hardware-level optical bypass taps instantly trigger upon detecting a drop in carrier signal or internal power loss, mechanically snapping mirrors into position to bridge incoming and outgoing fiber strands in less than fifty milliseconds.
This hardware fallback ensures that critical business traffic bypasses the unpowered or degraded scrubbing node entirely, converting a potential bottleneck into an uninterrupted, raw pass-through conduit.Concurrently, software-defined control planes detect the telemetry collection node’s heartbeat failure and dynamically reroute residual data streams toward secondary regional scrubbing stations using optimized Border Gateway Protocol path manipulation. For instance, if the primary telemetry aggregator in Frankfurt experiences a catastrophic power outage, neighbouring routing nodes instantly withdraw their reachability advertisements, shifting ingestion loads to redundant appliances in Zurich.
- Primary nodes continuously broadcast micro-heartbeats via dedicated out-of-band management interfaces to verify immediate cluster health.
- Optical bypass relays mechanically re-route physical light paths within milliseconds of detecting internal component electrical failure.
- BGP route-health metrics automatically withdraw faulty collector IP advertisements from the global routing table to prevent packet blackholing.
- Secondary regional scrubbing appliances dynamically scale their processing allocation pools to absorb the newly redirected telemetry influx without dropping packets.
Administrative Validation Checks Prior to Firmware Deployment
Deploying firmware updates to live operational sensors monitoring multi-gigabit traffic requires an uncompromising validation methodology to prevent catastrophic network outages or telemetry blackouts. Administrators must navigate a strict sequence of pre-flight inspections before authorizing any software transition on production-grade packet scrubbing appliances.
- Execute comprehensive compatibility matrices comparing current ASIC microcode versions against the proposed firmware release notes to identify hardware-level deprecations.
- Perform offline sandbox validation by replaying historical, packet-captured anomaly traffic through a virtualized twin of the target sensor model.
- Verify cryptographic image signatures using hardware-anchored Trusted Platform Module keys to confirm the update binary originates from a verified, uncompromised source.
- Schedule automated rollback triggers within the bootloader configuration to revert to the previous stable firmware image if post-boot health checks fail.
- Audit available storage partitions and verify that active logging directories retain sufficient free capacity to archive pre-update diagnostic dumps.
Multi-Site Deployment Parameters and Operational Metrics
The intricate balance between synchronization speed, network overhead, and failover resilience across global scrubbing appliances is meticulously quantified through standardized operational metrics designed to maintain peak enterprise performance.
As enterprise traffic surges through advanced netscout commercial filtering network data transfer product models, organizations suddenly discover a vivid blueprint for digital clarity. By seamlessly aligning this robust infrastructure with custimy.io platform features , leaders unlock unprecedented insight to empower their teams. Ultimately, this dynamic synergy optimizes vital intelligence across every netscout commercial filtering network data transfer product models deployment today.
| Deployment Region | Synchronization Interval | Bandwidth Overhead (%) | Failover Recovery Time | Heartbeat Timeout |
|---|---|---|---|---|
| North America Primary | 100 milliseconds | 1.2% | 45 milliseconds | 3 seconds |
| European Union Hub | 150 milliseconds | 1.5% | 50 milliseconds | 3 seconds |
| Asia-Pacific Gateway | 250 milliseconds | 2.1% | 65 milliseconds | 5 seconds |
| South American Outpost | 300 milliseconds | 2.4% | 80 milliseconds | 5 seconds |
Visualizing this global telemetry network reveals a dazzling, interconnected matrix of pulsing light nodes stretching across digital maps, where every color-coded marker represents millions of packets being analyzed and categorized in real-time. Glowing green synchronization lines weave effortlessly across oceans, representing the constant hum of policy data keeping every continent unified. When a localized storm threatens a regional node, amber alert pulses illuminate the affected zone before optical bypass paths instantly route around the friction, maintaining the serene, continuous flow of enterprise intelligence.
Integrating real-time traffic purification mechanisms with third-party security orchestration platforms to accelerate threat mitigation responses

Source: skomplekt.com
Advanced Netscout commercial filtering network data transfer product models systematically secure digital highways by isolating critical bandwidth streams. Amidst this technological evolution, communities bravely empower philanthropy through the dilon concept foundation givebutter initiative, fostering incredible hope and sustainable growth. Ultimately, these robust enterprise filtering solutions guarantee optimal routing efficiency, safeguarding every vital packet traversing modern global infrastructures today.
Modern enterprise defense requires an instantaneous bridge between raw telemetry collection and automated remediation systems. When malicious actors breach traditional perimeters, every millisecond counts in preventing widespread data exfiltration.
The journey from raw packet inspection to automated threat containment relies on sophisticated API handshake mechanisms that operate seamlessly beneath the enterprise surface. As purified telemetry streams leave the filtering appliances, they initiate a cryptographic dialogue with external security orchestration, automation, and response (SOAR) dashboards. This initial connection begins with a mutual Transport Layer Security validation, wherein the filtering hardware and the receiving endpoint exchange digital certificates to establish a zero-trust communication tunnel.
Once trust is verified, the telemetry engine initiates a persistent WebSocket or HTTP/2 multiplexed session, designed to bypass the latency penalties of traditional request-response cycles. Incoming data packets are serialized into lightweight JSON payloads, encapsulating metadata such as anomaly scores, source IP profiles, and behavioral deviation flags. To maintain sub-second delivery speeds during traffic spikes, the API utilizes token bucket algorithms for dynamic rate adjustments, ensuring that critical security events are prioritized over routine diagnostic logs without dropping packets.
This continuous stream of structured intelligence empowers incident response analysts to visualize emerging threat vectors on centralized dashboards the exact moment anomalies cross the purification threshold.
API Integration Specifications for Telemetry Transmission
Deploying secure data pipelines between high-capacity hardware filters and external security platforms demands strict adherence to standardized data structures, authentication protocols, and cryptographic safeguards to prevent unauthorized data exposure.
| JSON Payload Structure | Authentication Token Types | Rate-Limiting Thresholds | Encryption Standards |
|---|---|---|---|
"event_id": "uuid", "timestamp": "ISO8601", "threat_score": float, "subnet": "string" |
JSON Web Tokens (JWT) with short-lived expiration and elliptic-curve digital signatures | 10,000 requests per second per tenant API key with burst allowances up to 15,000 | TLS 1.3 mandatory with Perfect Forward Secrecy via cipher suites like TLS_AES_256_GCM_SHA384 |
"packet_vector": "hex", "action_taken": "quarantine", "severity": "critical" |
OAuth 2.0 Bearer tokens managed via centralized enterprise identity providers | 5,000 requests per second for standard telemetry feeds; dynamic throttling on congestion | AES-256 payload encryption at the application layer prior to transport transmission |
Automated Network Containment Protocols
Detecting an active breach is only the first step in operational defense; instantly severing the path of unauthorized data exfiltration requires precise, event-driven isolation triggers embedded directly within the hardware forwarding plane.
When the traffic purification engine identifies anomalous outbound data flows indicative of a data breach, it bypasses human-in-the-loop delays by executing pre-compiled mitigation scripts. These event-driven triggers evaluate behavioral anomalies against strict policy thresholds. Upon confirmation, the system issues an immediate hardware-level instruction to reconfigure Virtual Local Area Network (VLAN) assignments or inject dynamic Border Gateway Protocol (BGP) blackhole routes.
For example, if a compromised database server begins exfiltrating sensitive intellectual property to an external command-and-control server, the filtering appliance instantly drops traffic originating from that specific host port while simultaneously cloning the malicious session for forensic analysis. This rapid containment prevents lateral movement across adjacent enterprise subnets, effectively quarantining the threat before security analysts even acknowledge the primary alert.
Instantaneous network isolation transforms passive telemetry monitoring into an active biological immune system for enterprise architecture.
Administrative Access Control and Channel Security
Securing the communication channels that transmit critical telemetry data requires rigorous administrative access policies designed to neutralize man-in-the-middle interception attacks and unauthorized credential harvesting.
Enterprise administrators must enforce multi-factor authentication combined with hardware-bound security keys for all personnel interacting with the API gateway. Furthermore, communication channels are strictly segregated through dedicated management VLANs and software-defined micro-segmentation, ensuring that API traffic never traverses public or untrusted internal networks without encapsulation. Certificate pinning is universally deployed across all connected orchestration platforms to prevent forged certificate authorities from spoofing legitimate telemetry endpoints.
Regular cryptographic rotation schedules for API keys and tokens limit the window of vulnerability should administrative credentials ever be compromised. Comprehensive audit logging tracks every handshake, token exchange, and administrative configuration change, providing security operations teams with the complete visibility required to maintain absolute integrity across the entire telemetry pipeline.
Optimizing internal memory allocation strategies to sustain uninterrupted packet streaming during sudden enterprise bandwidth saturation events
When enterprise networks experience unexpected surges in data traffic, the underlying telemetry infrastructure faces an immediate danger of packet loss and latency spikes. Maintaining continuous visibility requires sophisticated memory management frameworks that can instantly adapt to volatile data influxes without dropping critical packets. The architecture must dynamically absorb massive traffic spikes while preserving the integrity of downstream analytics engines.Modern enterprise environments routinely witness unpredictable traffic surges driven by sudden cloud data migrations, massive software updates, or unexpected distributed denial-of-service vectors.
To prevent catastrophic bufferbloat and frame drops at line rate, advanced filtering appliances implement dynamic buffer reallocation techniques deployed when inbound traffic volume exceeds nominal interface thresholds. As incoming bitrates threaten to saturate physical interface cards, the system initiates a rapid reallocation protocol across unified memory architectures. Instead of relying on static, pre-allocated memory pools which inevitably lead to fragmentation or exhaustion during peak loads, the memory manager utilizes predictive sliding-window algorithms.
These algorithms continuously monitor packet arrival rates and automatically shrink non-essential logging buffers to expand the ring buffers dedicated to raw ingress traffic. When the physical interface registers a sudden surge surpassing eighty percent capacity, the firmware triggers an immediate reallocation of system memory blocks, shifting allocation away from historical session indexing and directing it entirely toward high-speed ring buffers.
This elasticity ensures that multi-gigabit data streams flow seamlessly into processing pipelines without stalling the hardware bus.
Dynamic buffer elasticity transforms rigid hardware limitations into adaptable processing pathways, ensuring zero frame loss during critical enterprise bandwidth saturation events.
Kernel-level network socket parameter tuning procedures
Preventing packet ring-buffer overflows demands meticulous configuration of the operating system kernel. Adjusting low-level networking parameters allows enterprise appliances to handle immense packet concurrency by optimizing how network interface cards interact with system memory.
- Execute administrative commands to modify the maximum socket receive buffer size, ensuring the operating system allocates sufficient space for high-volume burst absorption.
- Adjust the network device backlog parameter to expand the queue of packets waiting to be processed by the CPU after being pulled from the network interface card ring buffer.
- Configure the TCP window scaling factors to allow larger data windows, preventing transmission bottlenecks across high-speed enterprise interconnects.
- Modify interrupt moderation settings within the kernel driver parameters to balance CPU utilization and packet polling frequency during heavy traffic events.
- Disable unnecessary socket accounting features that introduce CPU overhead and latency during high-density packet ingestion cycles.
Thermal imaging characteristics of high-performance processing cards
Visualizing the physical manifestation of heavy computational loads provides vital insights into hardware endurance during peak filtering operations. Thermal diagnostics reveal how efficiently processing cards dissipate the intense heat generated by continuous high-speed packet ingestion and memory manipulation.A high-resolution thermal imaging illustration capturing a high-performance packet filtering card under maximum workload exhibits a vivid and dynamic color gradient across the printed circuit board.
The central processing units and dedicated field-programmable gate arrays glow in intense, brilliant shades of white and fiery orange, indicating extreme thermal output as millions of packets are parsed per second. Surrounding this central processing core, the adjacent high-density memory modules display a vibrant amber hue, showing consistent heat distribution resulting from aggressive buffer read and write operations. The heavy copper power delivery planes radiate a steady yellow glow, demonstrating uniform thermal dissipation across the multi-layer board.
In stark contrast, the peripheral input and output interfaces and the optical transceiver cages remain in cooler shades of deep blue and emerald green, maintained by forced-air cooling channels. This thermal map visually confirms that the cooling architecture effectively channels extreme thermal energy away from sensitive silicon components, preventing thermal throttling and ensuring sustained operational stability during severe enterprise bandwidth saturation events.
Memory garbage collection routines for expired session state tables
Maintaining optimal performance across continuous filtering operations requires proactive memory reclamation to purge stale data without causing system latency. Expired session state tables accumulate rapidly in high-throughput enterprise networks, consuming valuable RAM that is urgently needed for active traffic streams. To resolve this challenge without inducing central processing unit stalls that could drop live packets, network appliances deploy asynchronous, lock-free garbage collection routines.
Traditional memory sweeping mechanisms often lock entire data tables during cleanup, freezing processing threads and causing devastating micro-burst packet drops. In contrast, advanced filtering engines utilize generational memory partitioning combined with read-copy-update primitives. The session state memory is segregated into distinct time-based tiers, allowing the garbage collector to target exclusively expired tiers without locking active session blocks. Background worker threads systematically traverse these isolated tiers, unlinking stale state entries and returning memory pages to the pool in microsecond increments.
This non-blocking approach ensures that the central processing units remain entirely dedicated to inspecting live packet streams, maintaining deterministic processing latency even while millions of expired session records are purged simultaneously during peak operational hours.
Closure: Netscout Commercial Filtering Network Data Transfer Product Models

Source: slidesharecdn.com
Mastering the intricacies of high-speed enterprise telemetry and commercial packet scrubbing is no longer just a technical necessity; it is the fundamental bedrock upon which resilient digital operations are built. By harmonizing advanced hardware acceleration, dynamic memory allocation, and seamless security orchestration, organizations can transform chaotic torrents of data into structured, secure insights. As we look toward an increasingly interconnected future, the continuous refinement of these filtering paradigms ensures that our digital networks will remain steadfast, transparent, and fully prepared for the challenges of tomorrow.
